

AI has become a core asset for modern businesses, on par with data: It drives workflows, customer experiences, and operational models across every sector. In McKinsey's 2025 survey, 88% of respondents reported regular AI use in at least one business function. With 75% of organizations now self-hosting AI models, teams are taking greater control of their AI stacks, and with that comes greater security responsibility.
If you're a CISO, security architect, developer, or GRC leader, you're probably asking: How do we secure AI systems without slowing innovation down?
The sections below map the evolving landscape of AI security best practices, compare solution categories, and show why AI security posture management (AI-SPM) is a foundational pillar of proactive AI risk management.
AI Security Starter Pack
Turn the AI-first strategy into practical controls for discovering assets, evaluating exposure, and prioritizing risk.

What are AI security solutions?
AI security solutions are tools that protect the models, data pipelines, infrastructure, interfaces, and agents that make up your AI systems across their full lifecycle. They differ from AI-powered security tools, which use machine learning to detect threats elsewhere. This guide focuses on securing AI itself.
To build safeguards at every layer, AI security spans five domains:
1. Cloud & infrastructure security
Actionable steps: Secure compute environments against misconfigurations and unauthorized access that could expose sensitive data or compromise models.
2. Data governance & protection
Actionable steps: Safeguard training datasets and inference logs from unauthorized access and ensure compliance with privacy regulations (e.g., masking PII in prompts).
3. Identity & permissions for AI workloads
Actionable steps: Enforce least privilege for AI service accounts and API keys to shrink the blast radius of over-permissioned systems.
4. Application & API security
Actionable steps: Protect AI-powered web apps and model-serving APIs from misuse that could expose sensitive data or create compliance issues. For example, prompt injection attacks use adversarial prompts to steer a model toward unsafe actions.
5. Runtime observability & behavior monitoring
Actionable steps: Monitor production models for anomalies like toxic outputs or data exfiltration attempts, using logs and telemetry.
To secure each layer, consider posture-aware controls that understand the unique risks AI presents. That is the essence of modern AI security: finding and fixing risks based on how AI systems actually behave in your environment.
Why AI security solutions matter in 2026
AI security solutions matter because AI adoption is outpacing the controls built for older workloads. Copilots, generative AI apps, and autonomous agents reach production faster than most security programs can inventory them. Gallup found that 44% of US employees say their organization has begun integrating AI, yet only 22% say it has shared a clear plan.
Traditional security frameworks weren't built for non-deterministic models, dynamic prompts, or AI agents making real-time decisions. The gap shows up as shadow AI deployments, unrestricted data exposures, and adversarial manipulation of model behavior. Regulatory pressure is rising too, with global regulations like the EU AI Act kicking in.
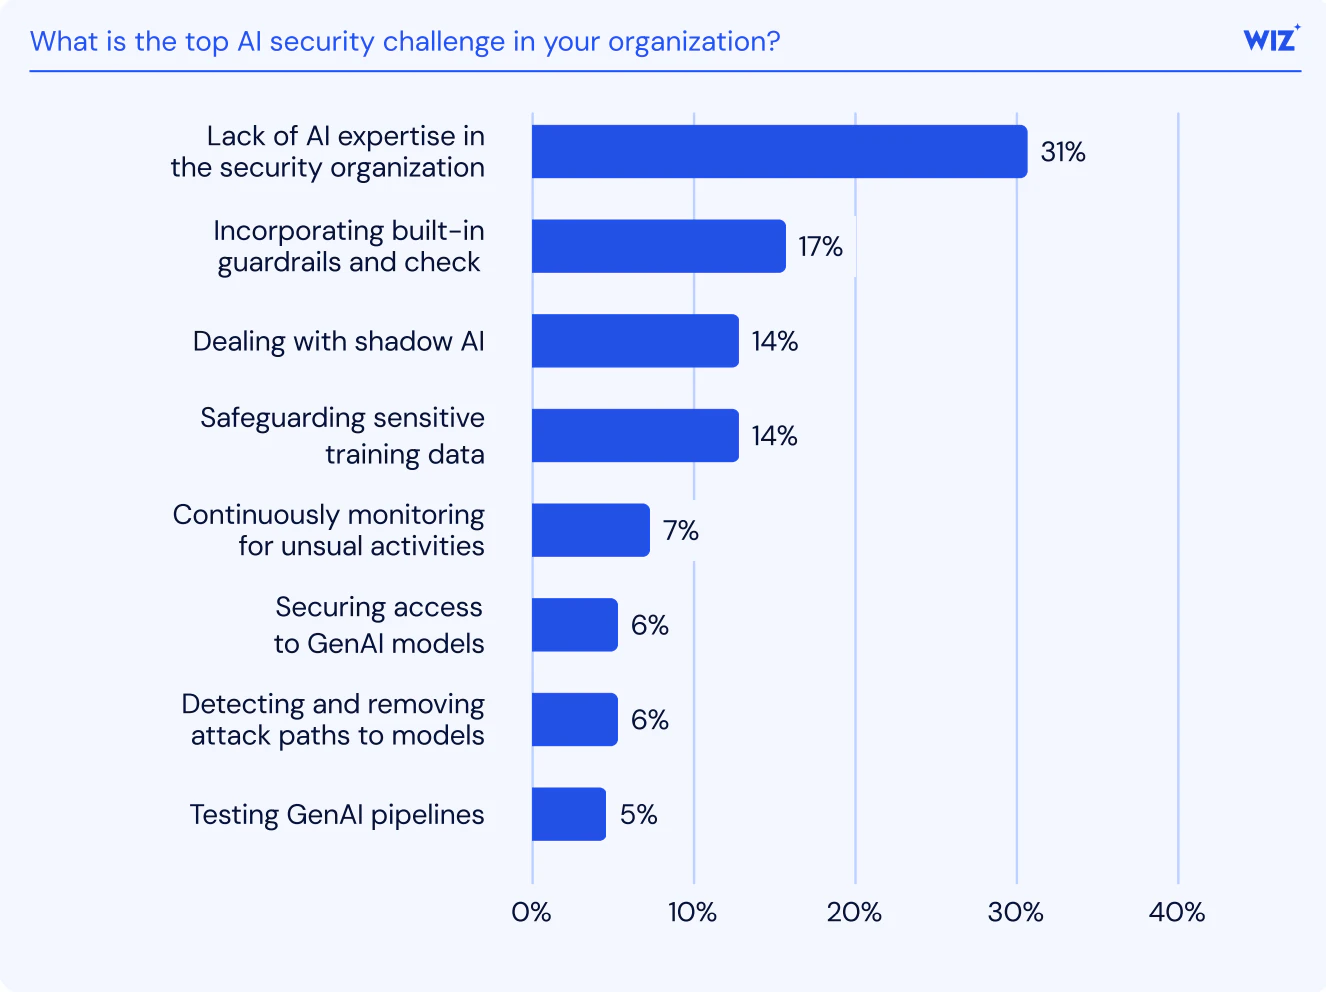
The threats themselves are new, too. Prompt injection barely registered a few years ago. Today it's a top concern for any team using large language models (LLMs) that have memory or interact with external tools, with attackers capable of manipulating even state-of-the-art commercial and open-source foundation models.
Our AI Security Risks guide covers many more, but three deserve early attention in 2026:
Model extraction: Attackers reverse-engineer your AI models to steal intellectual property or replicate their functionality. This could compromise proprietary algorithms or expose your competitive edge.
Training data poisoning: By introducing malicious data into your training datasets, attackers can undermine model integrity, causing models to produce faulty or biased predictions.
Over-permissioned AI agents: When AI systems are given more access than they need, whether to data, systems, or services, there's a greater risk that an attacker could exploit this excessive access, leading to larger-scale breaches.
The bottom line: Scaling AI securely requires an AI-first strategy built for dynamic systems and rapid change. Each of these risks maps to a control you can test.
AI security solution evaluation criteria
Anchor every evaluation to requirements you can test in a proof of concept. Governance is still catching up, too: only 21% of leaders in a Deloitte survey report a mature governance model for agentic AI. These six criteria show whether a tool sees your whole AI environment or one slice of it.
AI asset discovery coverage: Find every model, AI service, and agent, including shadow AI and Model Context Protocol (MCP) servers. Exposure is already real, since 5% of environments using MCP servers have at least one internet-facing server, so test against a known inventory and count what it misses.
Context across cloud, identity, and data: Each finding should show who can reach a model and what data it touches. An exposed endpoint matters far more when its identity can read a customer database.
Code-to-runtime lifecycle coverage: The same policy should follow an AI component from the repository through deployment into production. Gaps between stages are where risky changes slip through.
Framework mapping: Findings should map to the OWASP Top 10 for LLM Applications, the NIST AI Risk Management Framework (AI RMF), and MITRE ATLAS. Auditors and GRC teams already speak those frameworks.
Workflow integrations: Alerts should flow into security information and event management (SIEM) and security orchestration, automation, and response (SOAR) tools. Checks should also run inside continuous integration and delivery (CI/CD) pipelines.
Deployment speed and operating model: Agentless tools connect through cloud APIs and usually reach broad coverage faster. Agent-based tools add depth inside workloads but take more effort to roll out and maintain.
In practice, three vendor questions expose most differences during a demo. Ask the vendor to trace one AI agent to its identity, tools, and reachable data in a single view. Then ask how a code-level finding links to the running workload it affects, and what a new cloud account needs before its AI assets appear in inventory.
Types of AI security solutions
Solutions in this space fall into three categories. Knowing where these AI security tools fit shows you which gaps a single platform already closes:
AI-APP for full-lifecycle visibility, risk management, and governance across your AI environment
AI lifecycle-specific tools for deeper security at specific stages of the AI lifecycle, in development and production
AI use case-specific solutions for particular types of AI workloads, especially LLMs, autonomous agents, or third-party AI supply chains
The table summarizes the six sub-categories below. Where Wiz provides native platform capabilities, it is listed first; other solutions are listed in no particular order.
| Category | Lifecycle coverage | Top risks | Best for |
|---|---|---|---|
| AI-APP and AI-SPM | Development ➔ deployment ➔ production | Shadow AI, exposed endpoints, over-permissioned agents | Any AI maturity level, multi-team AI programs |
| AI development security | Design ➔ development ➔ testing | Malicious dependencies, model bugs, adversarial flaws | ML teams building or fine-tuning models |
| AI data security | Data collection ➔ transformation ➔ training | PII in training data, leakage through outputs | Regulated industries with sensitive data |
| AI runtime security monitoring | Deployment ➔ monitoring ➔ maintenance | Malicious usage, model exfiltration | Customer-facing or business-critical AI |
| LLM security | Deployment ➔ production | Prompt injection, jailbreaks, response leakage | Chatbots and apps built on foundation models |
| AI supply chain security | Design ➔ development ➔ deployment | Model tampering, unsafe open-source models, missing provenance | Teams using third-party or pre-trained models |
Layer 1: AI application protection platforms
AI-APP is the comprehensive category. It extends cloud native application protection platforms (CNAPP) to AI-native applications by connecting code, posture, data, and runtime in one view. For many organizations, this is the first step in scaling secure AI. It closes a real gap: in Wiz's AI Security Readiness report, 25% of respondents didn't know which AI services were running.
AI security posture management (AI-SPM) tools
AI-SPM is a foundational pillar of AI-APP. It acts as your posture control plane, providing visibility and enforcement across development, deployment, and runtime.
Leading AI-APP solution:
Wiz AI-APP: Builds a live inventory of your AI estate, including shadow AI, deployed agents, and unmanaged resources. It ranks risks like exposed inference endpoints using infrastructure context.
Other AI-SPM solutions:
Microsoft Defender for Cloud: Cloud security posture management (CSPM) with AI and ML asset support
Palo Alto Networks Prisma Cloud AI-SPM: CSPM with AI/ML visibility and threat detection
Key capabilities:
Continuous discovery and inventory of AI assets across your environment
Risk assessment for AI-specific misconfigurations and vulnerabilities, including model-serving endpoints, over-permissioned agents, and prompt injection risks
Identity, access, and permissions management for AI workloads
Code-to-cloud correlation to trace AI model exposure back to the originating code, pipeline, or misconfiguration for remediation prioritization
Integration with broader cloud security frameworks
AI lifecycle coverage: Development ➔ deployment ➔ production operations
Risks addressed: Shadow AI, exposed endpoints, misconfigured services, over-permissioned AI agents, compliance violations
Best for: Organizations at any AI maturity level seeking a foundation for their AI security strategy, especially those with AI initiatives spanning multiple teams
Layer 2: AI lifecycle-specific tools
Once AI-SPM gives you foundational visibility, lifecycle-specific solutions add deeper controls at one phase, such as development, data preparation, or production.
AI development security tools
Development-phase security tools protect your AI at its source, addressing vulnerabilities before they reach production. Credentials are a common weak spot, with 4 of the top 5 secrets in public repos tied to AI platforms.
Key capabilities:
Secure coding practices for AI development environments
Static and dynamic scanning of AI code and notebooks
Dependency scanning for ML frameworks and libraries
Model robustness, fairness, and explainability testing
Vendors:
Protect AI: AI security platform with advanced model scanning via ModelScan and notebook security with open-source NB Defense
Robust Intelligence: AI stress-testing platform with automatic adversarial and robustness testing for models
Weights & Biases: AI experiment tracking tool with built-in security
Best for: Data science and ML engineering teams building custom models or fine-tuning foundation models, especially for high-risk use cases
AI data security solutions
Data is the bedrock of AI, so data security tools protect sensitive information throughout the AI lifecycle.
Key capabilities:
Sensitive data discovery and classification in AI datasets
Redaction and masking tools for protecting PII
Encryption and tokenization of training data
Vendors:
Wiz AI-APP: Scans datasets and vector stores for PII, secrets, and IP through Wiz Data Security, then maps which models can reach that data.
Sentra: Cloud-native DSP with AI-specific context
Immuta: Data access control platform with dynamic data-policy enforcement for AI training data
BigID: Data privacy and governance platform with sensitive-data discovery and compliance automation
Best for: Organizations working with sensitive or regulated data, particularly in healthcare, financial services, or government sectors
AI runtime security monitoring
In production, runtime security tools continuously watch for threats, anomalies, and misuse so teams can respond in real time.
Key capabilities:
Real-time telemetry and anomaly detection
Output monitoring and behavioral baselining
Integration with SOC/SIEM pipelines for unified security operations
Vendors:
Wiz Defend: Detects prompt injection, jailbreaks, model invocation anomalies, and control-plane exfiltration, correlated with cloud context.
HiddenLayer: ML threat detection platform with real-time protection against model theft and adversarial attacks
Protect AI: AI security platform with real-time model behavior monitoring and drift detection via Layer
Fiddler: AI observability platform with security-centric anomaly detection and bias monitoring
Best for: Organizations with customer-facing or business-critical AI systems that need active protection against exploitation and abuse
Watch 12-min demo
Learn what makes Wiz the platform to enable your AI security operation

Layer 3: AI use case-specific solutions
The outer layer covers use case-specific solutions for specialized AI components. These tools target risks that emerge in LLMs, autonomous agents, and AI supply chains.
LLM security solutions
Protect LLMs and LLM-powered applications from attacks like prompt injection and output manipulation.
Key capabilities:
Prompt filtering and jailbreak detection
Output scanning for sensitive information
Customizable guardrails and safety policies
Monitoring of LLM usage patterns
Vendors:
Wiz AI-APP: Secures LLM apps and AI agents by mapping tool permissions, MCP boundaries, and API exposure on the Wiz Security Graph.
Prompt Security: GenAI security platform focused on prompt risk management and attack detection
Lakera: AI-native security platform specialized in adversarial prompt protection and secure LLM operations
Protect AI: AI security platform with a specialized toolkit, LLM Guard, for securing GenAI apps against attacks
Best for: Organizations deploying customer-facing chatbots, internal productivity tools using LLMs, or any application built on foundation models
AI supply chain security
Supply chain security tools secure the components and models you source from third parties, open-source repositories, or external vendors.
Key capabilities:
AI-specific software bill of materials (SBOM)
Model lineage and provenance tracking
Risk scoring of external model components
Continuous monitoring for vulnerabilities in AI dependencies
Vendors:
Wiz AI-APP: Detects malicious code and vulnerabilities in third-party models (e.g., from Hugging Face) and open-source libraries before they reach production AI.
Protect AI: AI security platform with fast-tracked automated remediation for vulnerabilities discovered in their huntr GenAI bounty platform
AI Risk Repository: Living database of AI risks co-created by MITRE ATLAS and Robust Intelligence
Anchore: Software supply chain security platform with support for AI/ML artifacts
Best for: Organizations building applications on third-party foundation models or using pre-trained components from various sources
How to choose an AI security solution
Choosing an AI security solution starts with two questions: how mature your AI program is, and which risks would hurt most if they landed. The answers tell you which parts of the AI stack your platform needs to cover first. Settle ownership early as well, since PwC found there is no single ownership model yet for AI governance and risk management.
1. Assess your AI maturity
Ask: "Where am I on my AI journey?"
Just starting? Turn on AI-SPM first for visibility across your AI estate.
Building GenAI apps? Extend the same platform to runtime monitoring, LLM security, and API protection.
Reached enterprise-wide AI adoption? Cover the full stack in one platform: development security, data governance, compliance, and runtime observability.
Map your AI systems to business impact. Prioritize securing systems that interact with sensitive data, drive customer decisions, or automate high-risk operations.
2. Evaluate tools against your risk profile
Don't get caught in feature checklist hell. When choosing a security solution or tool, focus on:
Cloud-native, developer-friendly integrations
Cross-team usability (security + ML + compliance)
Vendor roadmap agility (AI threats are moving fast!)
Point tools each see one slice of the stack, which is why they miss the risks that sit between layers. An exposed endpoint, an over-permissioned agent identity, and a sensitive training bucket only look critical when you see them together. A unified AI-APP puts those signals on one graph. Teams then fix the combination that matters instead of triaging three separate alerts.
Use a weighted scorecard to objectively rank tools against your must-haves. Bonus if you get input from GRC, data science, and engineering teams early on!
Wiz AI Security starts with visibility
Wiz brings AI security into the same view you already use for cloud risk, so AI models, agents, and data paths sit alongside the infrastructure they run on. That shared view lets teams secure new AI work without slowing it down. Konverso reached zero criticals for its GenAI platform by using Wiz to find and fix risks to the customer data behind its virtual assistants.
Wiz AI-APP brings the AI security solutions above into one platform: Wiz Code, Wiz Cloud, Wiz Data Security, and Wiz Defend, connected by the Wiz Security Graph. That connected view of real attack paths is why Wiz was named an AI Security Technical Innovator in Latio's 2026 AI Security Report.
The graph also discovers shadow AI agents, MCP servers, and vector databases, then classifies each tool and plugin permission as Read, Write, Execute, or Expose Data. Teams can enforce least privilege before prompt injection hijacks an agent.
Built-in AI capabilities act on that context:
Mika AI: Ask plain-language questions like "Which of my LLMs have access to production databases?"
Red Agent: Simulate attacks and validate exploitable AI and cloud paths.
Blue Agent: Automate threat investigation and triage, cutting response times from hours to minutes.
Green Agent: Generate code-level and cloud remediations.
Wiz Defend: Catch AI runtime threats like prompt injection or data exfiltration as they happen.
Request a demo to see how Wiz AI-APP secures your AI pipeline, models, and autonomous agents across your cloud environment.
See your AI attack surface in context
Explore how Wiz correlates AI assets, identities, data access, exposure, and runtime signals across your cloud environment.
