The AI Security Summit
Join Figma, Perplexity, and Wiz to learn how to monitor rogue agents, automate triage, and secure code.
Nuovo modello operativo di IA per la sicurezza
Scala l'impatto del tuo team con agenti di sicurezza specializzati e Mika—il tuo compagno AI onnipresente—tutto radicato nel contesto del Wiz Security Graph.
Difesa code-to-cloud alimentata dall'IA
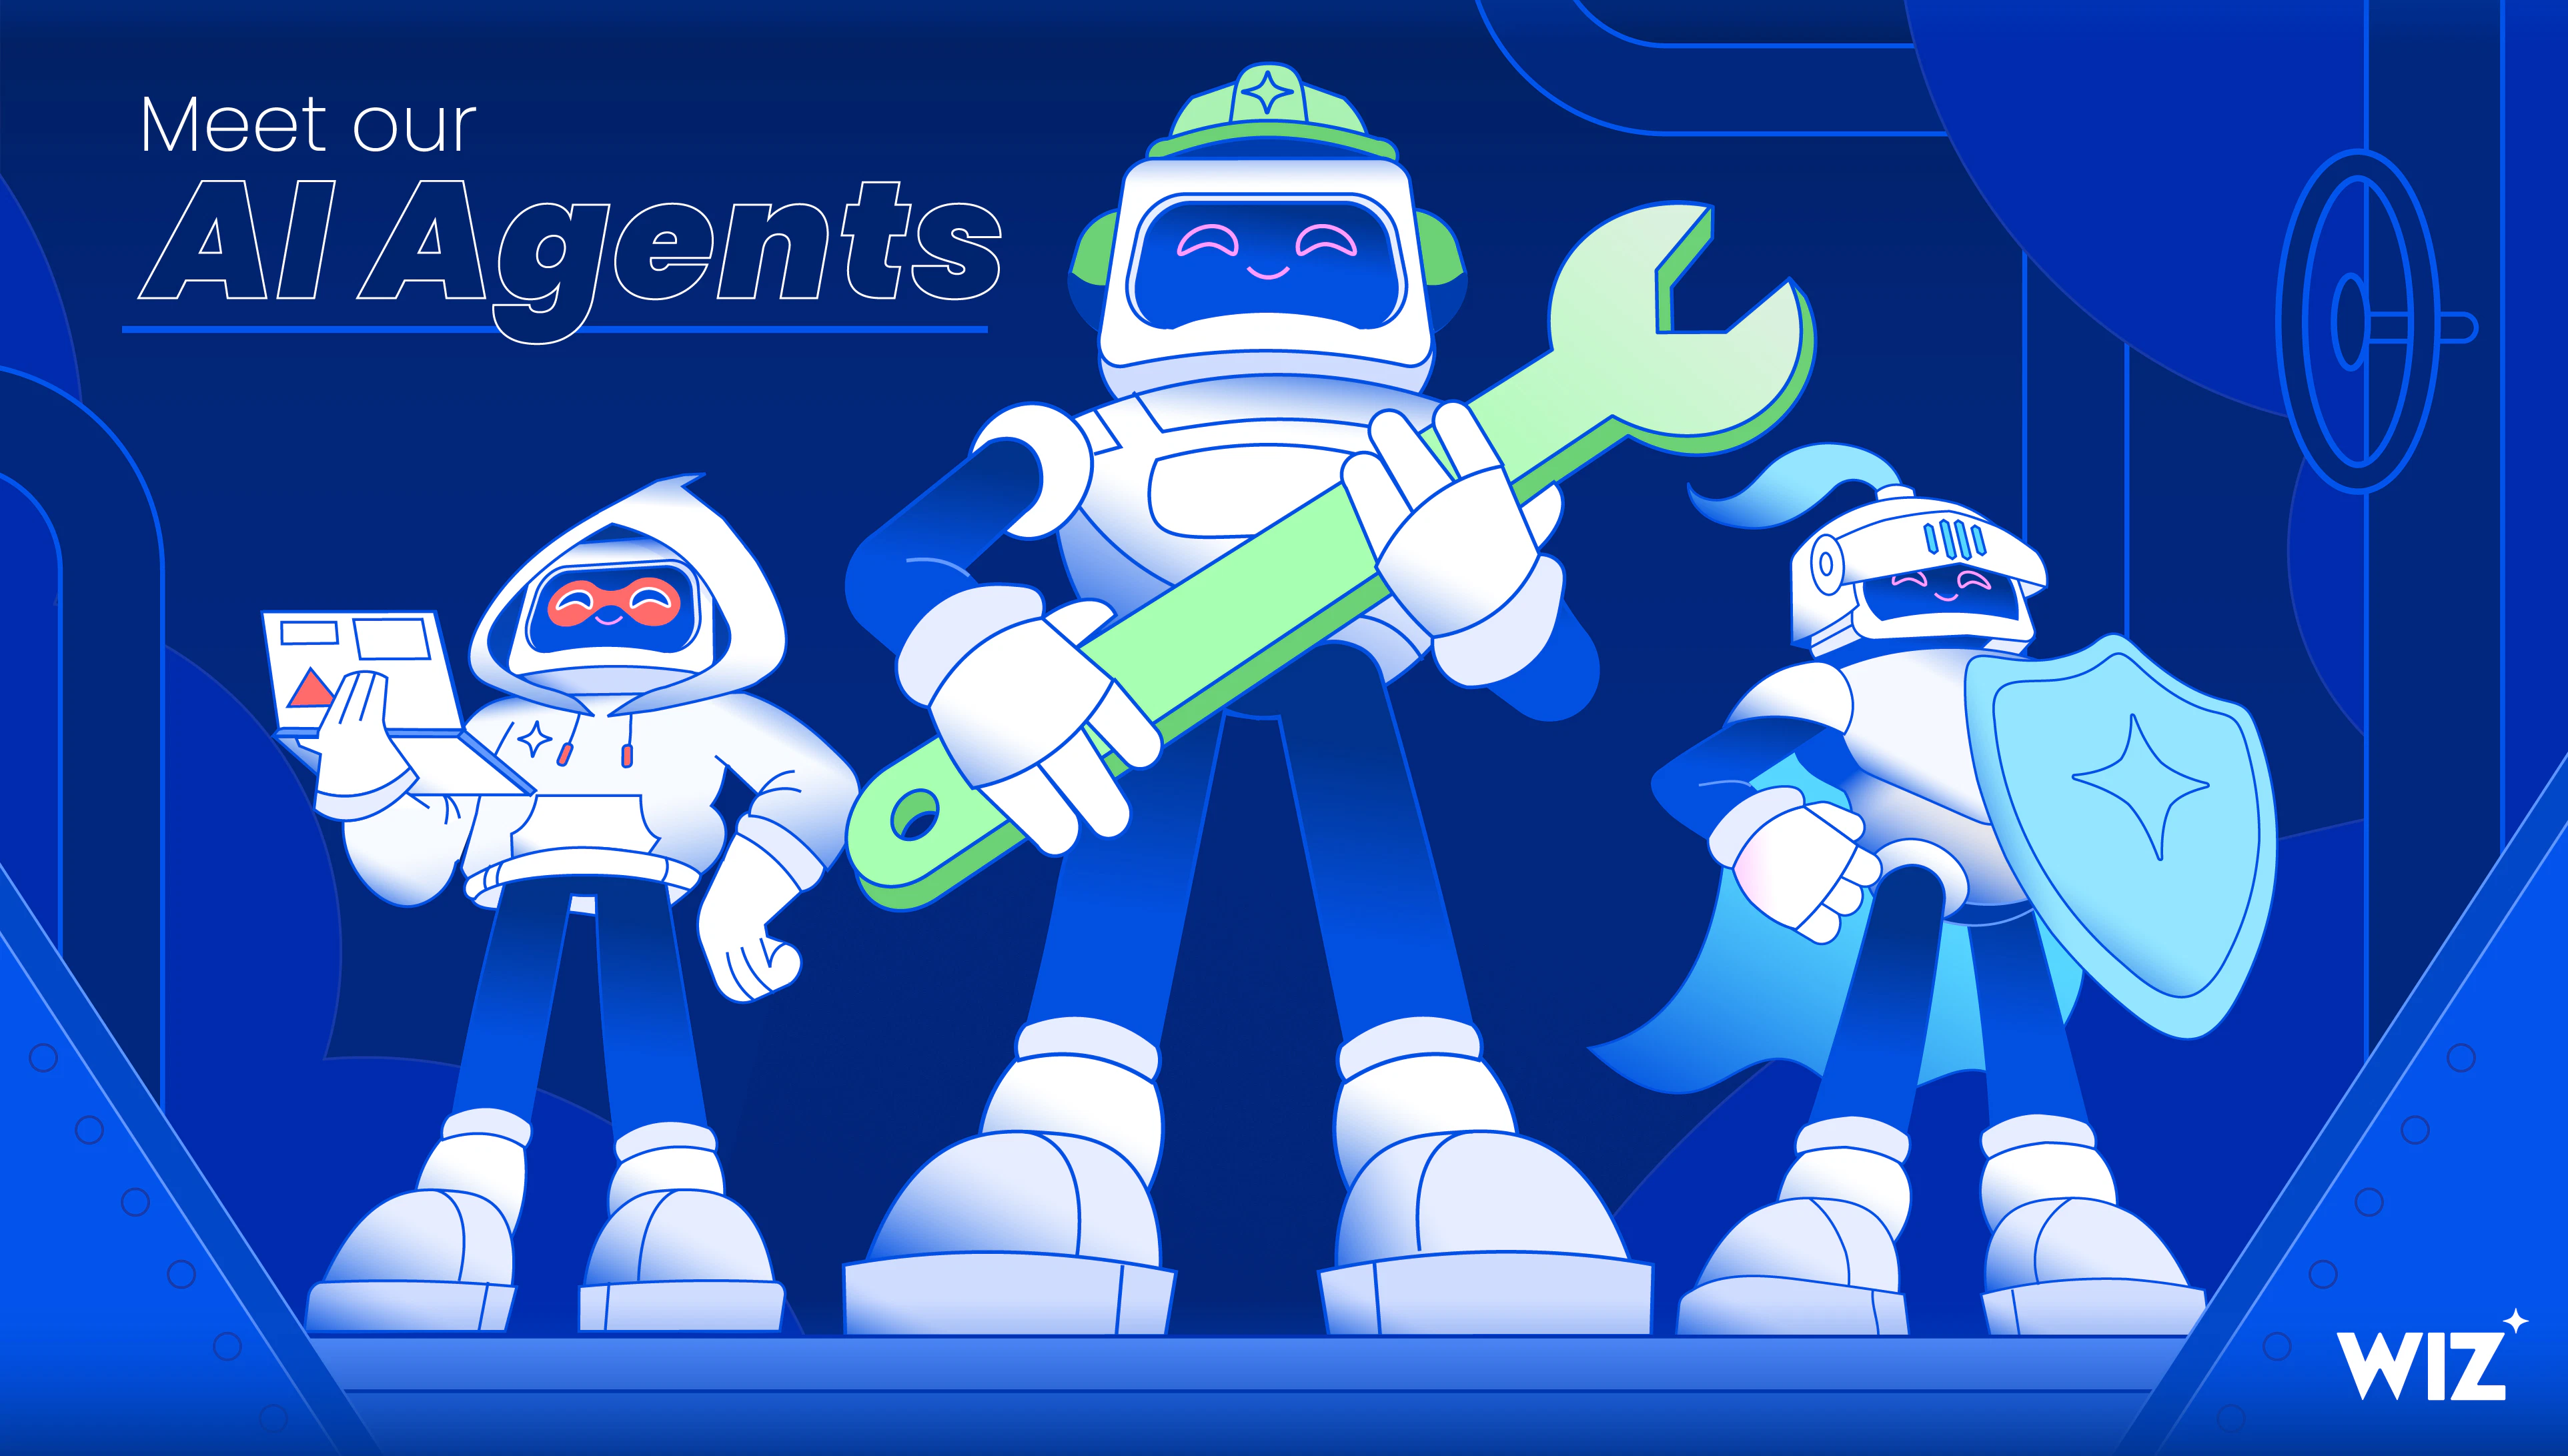
Il moltiplicatore di forza del tuo team: agenti AI specializzati che lavorano insieme per eliminare il lavoro manuale e accelerare ogni fase del ciclo di vita della sicurezza.
Beh, beh… Un punto finale esposto. Vediamo quanto in profondità arriva.
Simula continuamente percorsi di attacco reali attraverso il tuo cloud e lo stack AI per dimostrare cosa è realmente sfruttabile, eliminando rumori teorici e mettendo in luce i rischi che contano davvero.
Modalità detective attivata… Vediamo cosa è successo davvero.
Indaga autonomamente gli avvisi su cloud e codice, correla le prove end-to-end e offre un verdetto chiaro e difendibile con un raggio di massimo esplosione.
Bel colpo. Facciamo questo critico.
Colma il divario tra trovare e risolvere generando una bonifica consapevole del contesto alla fonte — portando i team verso rischi critici zero.
Visita guidata
Partecipa al tour guidato interattivo qui sotto
Mika porta l'intelligenza del Wiz Graph e degli agenti specializzati nei tuoi strumenti quotidiani, così puoi prendere decisioni informate senza mai uscire dal tuo flusso di lavoro.

Il Gateway to Custom Automation - Il Wiz MCP Server ti permette di collegare direttamente il Security Graph ai tuoi custom agent, alle knowledge base interne e agli IDE degli sviluppatori. Crea flussi di lavoro personalizzati che combinino l'intelligenza Wiz con i tuoi dati aziendali unici per automatizzare la sicurezza ovunque tu lavori.

Red Agent finds what humans miss. It caught critical authorization flaws across services where traditional testing and our bug bounty program came up short. We had continuous AI-powered attack surface testing on our roadmap. Wiz got there first, and did it better than we would have.

We are now fully relying on the Blue Agent for some of the low severity alerts. Instead of having a lot of tickets, it's just one task at the end of each shift — checking all those detections that have been closed by the Blue Agent. That is allowing our team to focus more on the advanced work.

The Green Agent creates a Jira ticket with the full description, attack path analysis, and remediation steps already populated. Developers have everything they need to act immediately.

What is most amazing about Red Agent is the way that we can track and get alerting or visibility on endpoints that can be attacked or manipulated from the outside. It tells me: 'You have an endpoint here, you are missing authentication,you have an exposure.' All of those insights are really, really helping me to close gaps fast.

My favorite thing about the Blue Agent is how quickly it helps us understand why an alert happened and what it actually means in our environment.

At first we continued our manual investigation side by side with the agents, but 10 out of 10 times we were getting the same threat assessment conclusions, building this trust enabled us to rapidly accelerate.

AI workflows with Wiz MCP connectivity ensure our minimum level of triage is the same high standard our systems maintain consistently.
Progetta i tuoi manuali di sicurezza: Indirizza Mika e i tuoi agenti specializzati con una tela visiva e senza codice. Concatena le azioni in sequenze automatizzate personalizzate—dal triage istantaneo alla vera e propria bonifica—adattate alla logica di risposta unica della tua organizzazione.