


What is API security?
Every API is a door into your application. API security decides who gets through, what they can do, and what data they leave with. That covers the endpoints an API exposes, the identities that call it, and the data it returns. In practice, you need to know what exists, check every request, and limit what each response contains.
APIs differ from classic web apps because many callers are services, scripts, and AI agents rather than people in a browser. Attackers go after object-level access and business logic, requesting records they shouldn't see or chaining calls in an unplanned order. That's why an API's real risk depends on cloud context: whether it's reachable, which identity it runs as, and what data it can touch.
Advanced API Security Best Practices [Cheat Sheet]
Download the Wiz API Security Best Practices Cheat Sheet to master advanced API security. Implement proven techniques to harden your infrastructure and ensure secure, high-performance API management across the lifecycle.

Why traditional API security falls short
Traditional API security controls can check whether a request has a valid token or matches an expected format. But a valid request can still expose data if the API doesn’t check whether the caller is allowed to access the requested record.
That distinction matters because APIs often give users and services direct access to application data and actions. A gateway alone can’t always tell whether a customer should be able to view a particular order or whether a series of valid calls abuses a business process.
Look for these common gaps when reviewing your API security:
Incomplete API inventory: An older API version or undocumented test API may still accept requests, even after teams stop maintaining it.
Missing object-level checks: An API may authenticate a caller but fail to verify that the caller can access the specific record they requested.
Limited business logic visibility: Individual requests may look legitimate while a sequence of calls lets someone bypass a purchase limit or abuse a promotional offer.
For example, a customer might call GET /v1/orders/123 and then change the order number to request another customer’s record. The API needs to check ownership or other access rules for each order, not just confirm that the customer is signed in.
Cloud details help you decide what to fix first. An authorization flaw in a public API that can read sensitive records deserves closer attention than the same flaw in an API with no reachable path from outside the environment.
12 API security best practices and recommendations
Securing an API comes down to four jobs: know every endpoint, control who can call it, limit what it returns, and watch how it is used. The 12 practices below follow that order, and each one works best when paired with the right API security tools.
1. Implement continuous API discovery
When you manage hundreds of APIs across teams, manual tracking fails to keep pace with development velocity. Automated scanning identifies and catalogs every API across your infrastructure as it appears.
Many teams lack a complete API inventory, which makes automated discovery essential for full security coverage. This gap is further compounded by the explosion of AI infrastructure. The Wiz State of AI in the Cloud 2026 report reveals that 81% of organizations use managed AI services, and 90% run self-hosted AI software. Yet, despite this massive adoption, the Wiz AI Security Readiness report found 25% of respondents don't know which AI services run in their environment.
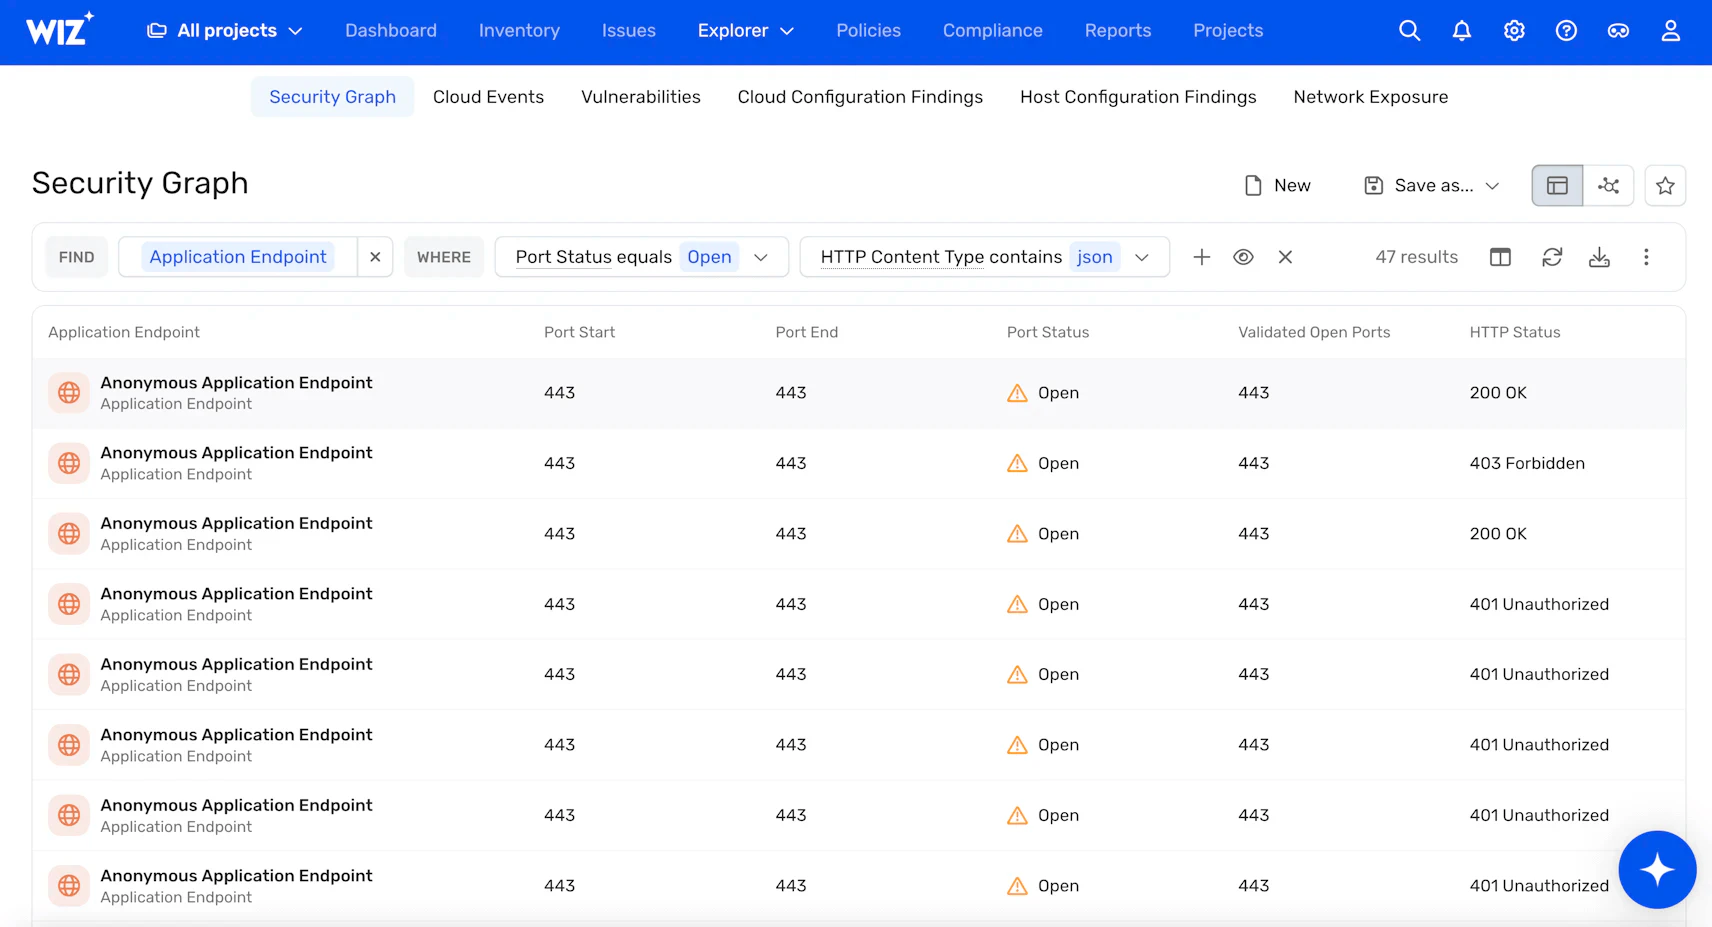
Continuous API discovery helps you identify shadow APIs and unmapped AI endpoints before attackers do. For example, developers may create a vulnerability when they deploy an API endpoint like /old_endpoint or spin up an unmonitored machine learning model endpoint, leaving it exposed. Implement a system to detect unauthorized or forgotten APIs so you can bring them into compliance or decommission them.
2. Encrypt traffic in every direction
Data moving between clients and servers needs protection from interception. TLS encryption secures this traffic, preventing attackers from capturing sensitive information during transmission.
HTTPS with valid SSL certificates: Required for all API communications
TLS 1.2 or higher: Defends against man-in-the-middle attacks
End-to-end encryption: Protects API keys and authentication tokens throughout their lifecycle
Modern TLS versions automatically defend against message tampering and forgery attempts. This makes encryption your first line of defense against network-based attacks, especially as 4% of cloud environments expose sensitive data through misconfigured HTTP/S endpoints.
3. Authenticate and authorize everything
// Example JWT validation
const jwt = require('jsonwebtoken');
const token = "JWT_TOKEN";
const secret = "SECRET_KEY";

try {
 const decoded = jwt.verify(token, secret);
 console.log(decoded);
} catch(err) {
 console.log("Invalid token.");
}
Verifying who makes a request is different from controlling what they can access. Authentication confirms identity through credentials or tokens, while authorization determines which resources that identity can reach.
Keep tokens short-lived and narrowly scoped, and validate the signature, issuer, audience, and expiry on the server for every call. A token that works everywhere for days turns one leak into a long incident.
JSON Web Tokens (JWT): Stateless verification that scales across distributed systems
OAuth 2.0: Delegates access to third-party applications without exposing credentials
OpenID Connect (OIDC): Adds an identity layer on top of OAuth for user authentication
These protocols allow users to grant limited access to applications without exposing their primary credentials. This reduces the risk of credential theft and misuse, particularly since fewer than 45% of customers enforce MFA for ROPC, according to Wiz data.
4. Follow the principle of least privilege
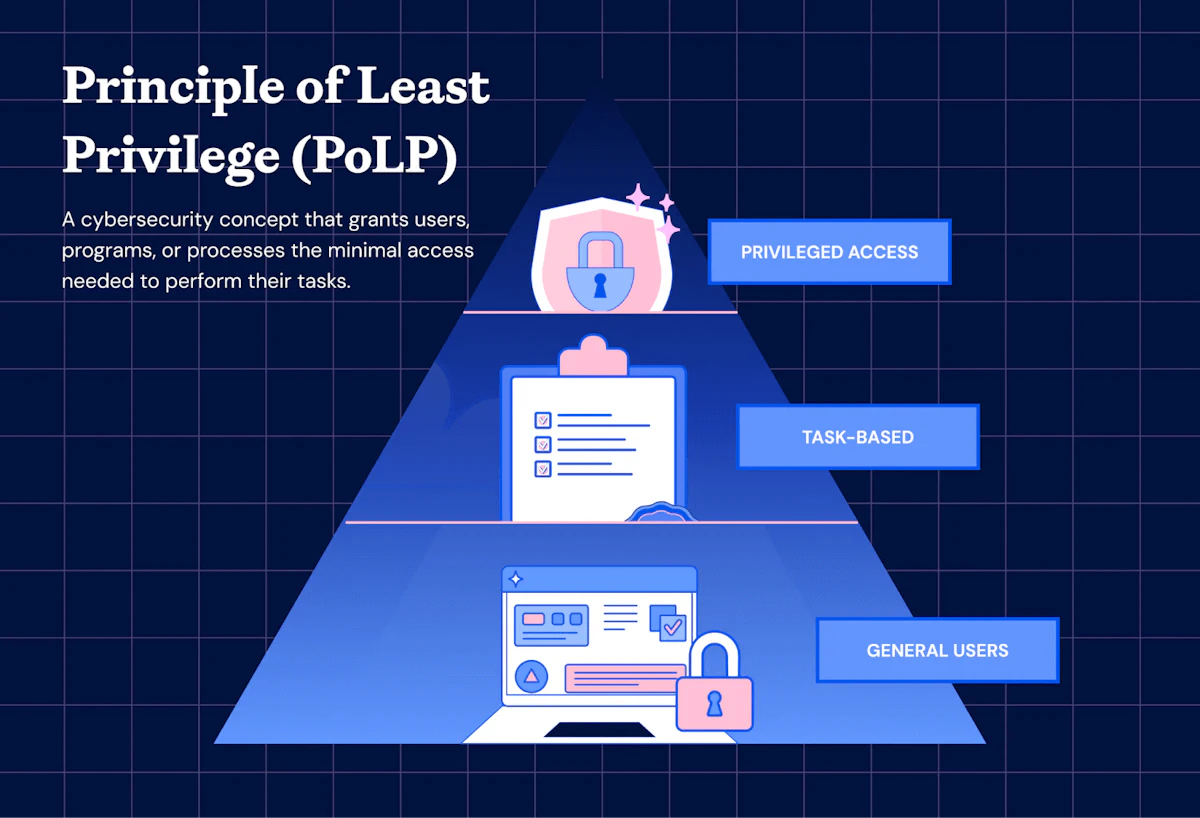
Every user, system, and automated service account interacting with your API should receive only the minimum access rights required for their role. In modern cloud ecosystems, this extends heavily to machine-to-machine communications.
The Wiz research notes that 57% of organizations have deployed self-hosted AI agents, and 80% have adopted Model Context Protocol (MCP) servers. These orchestration layers introduce massive control plane risks. If an autonomous agent or API service account is overprivileged, it creates an aggressive attack path where an actor can hijack the entity to move laterally through sensitive cloud data stores.
Following the principle of least privilege (PoLP) limits the potential damage a malicious actor can inflict if they gain access. In practice, that means pairing role-based access control (RBAC) with attribute-based access control (ABAC). A caller's role, tenant, and the object it requests all have to line up before the API responds.
5. Be diligent about API documentation
Because APIs expose more endpoints than traditional web applications, outdated API documentation can lead to misuse or unintended vulnerabilities. Furthermore, AI-assisted code generation has altered how code is shipped. Wiz Research found that 80% of organizations now use AI IDE extensions ("vibe coding"), and roughly 1 in 5 organizations using these platforms have systemic security weaknesses due to insecure, AI-generated defaults.
When code is generated and changed at this velocity, auto-generating and auditing API documentation (via tools like Swagger or Redoc) is non-negotiable to ensure that security defaults are explicitly validated and not blindly accepted.
6. Validate your data
// Example input validation
const { check, validationResult } = require('express-validator');

app.post('/user', [
 check('username').isAlphanumeric(),
 check('password').isLength({ min: 5 })
], (req, res) => {
 const errors = validationResult(req);
 if (!errors.isEmpty()) {
 return res.status(400).json({ errors: errors.array() });
 }
 // Continue processing
});
Strict input validation blocks injection attacks before malicious data reaches your back end. Libraries like express-validator in Node.js enforce these checks automatically. Schema validation ensures data structure and size match expected formats, preventing buffer overflow attacks and malformed payloads from causing harm.
7. Limit data exposure
Your API should return only the data that is necessary for its function. Excessive data exposure increases the risk of unintended data breaches. At Moltbook, one misconfigured database exposed 1.5M API tokens and 35,000 emails.
Always encrypt sensitive data, such as passwords, credit card numbers, and personal identification information, both at rest and in transit. Object-relational mapping (ORM) tools can also help you effectively filter out sensitive data.
8. Introduce rate limiting and throttling
Rate limiting caps how many requests a caller can make in a set window, which stops brute-force attempts and runaway scripts before they drain resources. Limit per API key or identity, not just per IP, since attackers rotate addresses easily.
For public APIs, add bot detection and a web application firewall (WAF) in front of the gateway to filter automated abuse. Content delivery networks then absorb traffic spikes, including distributed denial-of-service (DDoS) floods, that would otherwise overwhelm a single origin.
Watch 12-min demo
Learn what makes Wiz the platform to enable your cloud security and API security operations.

9. Use gateways to centralize security controls
A gateway creates a single entry point where you enforce security policies before requests reach backend services. This centralization simplifies management across dozens or hundreds of APIs. From the gateway, you can:
Apply rate limits
Require TLS encryption
Validate inputs
Block common attack patterns, like injection or cross-site scripting
10. Test your APIs regularly
Scheduled vulnerability scans catch configuration errors and known weaknesses before attackers find them. Testing should cover both API endpoints and the workloads that support them.
Run API tests in your CI/CD pipeline so a broken authorization check fails the build instead of reaching production. Checking risk in the pipeline is how Datavant cut container vulnerabilities by 51%. Keep frameworks and libraries patched too, since a vulnerable dependency can undo a well-designed endpoint.
Nuclei, an open-source scanner, uses YAML templates to detect specific vulnerabilities and misconfigurations across your API surface.
11. Conduct diligent API key management
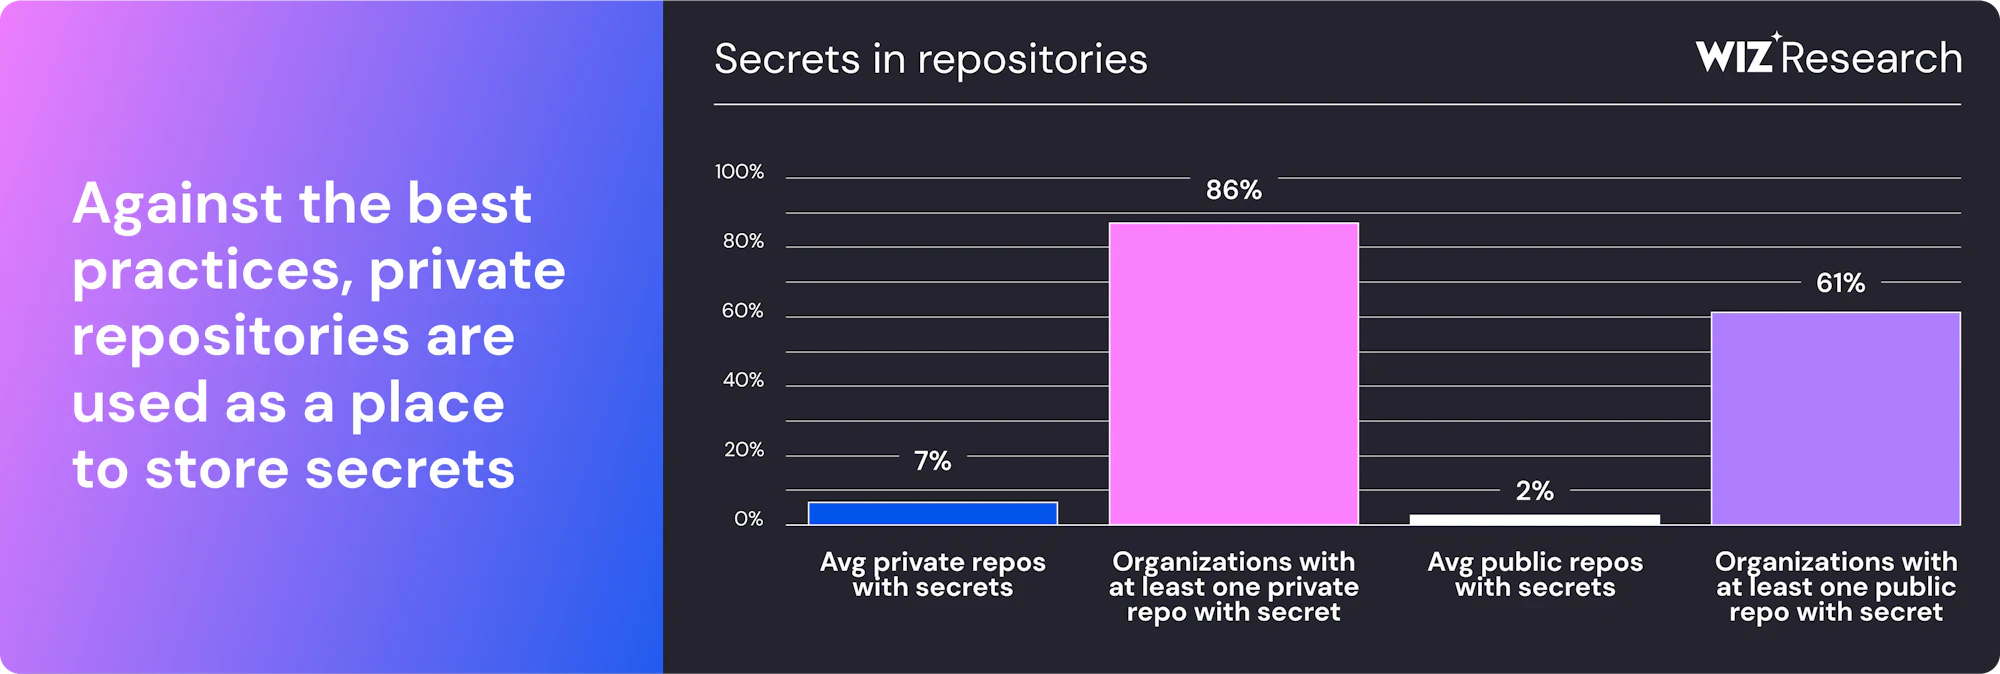
API keys function like passwords, so you must safeguard them diligently. Compromised credentials were an initial access vector in 22% of breaches in Verizon's 2025 DBIR. The widespread exposure of secrets—with 61% of organizations having secrets exposed in public repositories, according to Wiz's State of Code Security Report 2025—makes credential scanning critical.
Rotate your API keys regularly to prevent unauthorized access, and use short-lived tokens for added security. You can also securely store your API keys using environment variables or secret management tools.
12. Implement comprehensive auditing and logging
Auditing is what makes API security measurable. You need logs that let you answer who called what, from where, and what they touched.
At a minimum, capture these fields for every request:
Caller identity: User ID, client ID, service account, token issuer, and the auth method used
Request target: Endpoint, method, version, and the object identifier you authorized against
Outcome: Status code, authorization decision, and error type for failures
Abuse signals: Rate limit events, unusual spikes per identity, and repeated 401 or 403 patterns
Route logs to a central place, alert on high-signal patterns, and set retention that matches your incident response and audit needs. Gateways help, but you still need app-side logs for object-level and business-flow decisions.

OWASP API Security Top 10: Critical risks you must address
OWASP's list of top API risks identifies the most critical weaknesses attackers exploit against APIs. Three of the top five OWASP API risks relate directly to authorization failures—Broken Object Level Authorization (BOLA), Broken Object Property Level Authorization, and Broken Function Level Authorization—making access control the most recurring theme in the list.
Broken Object Level Authorization (BOLA): APIs that don't properly check if a user should access a specific object can leak or expose sensitive data. Always validate user permissions for object requests.
Broken Authentication: Weak or missing authentication lets attackers impersonate legitimate users or skip identity checks entirely. Enforce strong authentication flows, disable default credentials, and expire and rotate tokens.
Broken Object Property Level Authorization: Failing to restrict access to sensitive object properties can expose confidential information. Make sure users can only access properties they're allowed to see.
Unrestricted Resource Consumption: APIs that don't limit resource usage can be abused, leading to denial of service or high cloud bills. Set sensible rate limits and quotas.
Broken Function Level Authorization: Not checking if a user is allowed to perform a certain action can let attackers escalate privileges. Always enforce authorization for every function or endpoint.
Unrestricted Access to Sensitive Business Flows: APIs that expose sensitive business processes without controls can be abused or used for fraud. Protect critical flows with extra checks and monitoring.
Server Side Request Forgery (SSRF): APIs that fetch URLs or resources on behalf of users can be tricked into accessing internal systems. Validate and restrict outbound requests.
Security Misconfiguration: Default settings, verbose error messages, or unnecessary features can open up vulnerabilities. Harden your API configuration and keep it simple.
Improper Inventory Management: Not keeping track of all your APIs, versions, and endpoints can leave old or undocumented APIs exposed. Maintain a complete, up-to-date API inventory.
Unsafe Consumption of APIs: Trusting data from third-party APIs without validation can introduce vulnerabilities. Always validate and sanitize data from external sources.
Real-world API security examples
Securing your APIs requires a multifaceted and continual approach. Here are some examples of successful and unsuccessful API security.
When API security goes wrong
On Dec. 30, 2024, the US Department of the Treasury disclosed that Chinese state-backed hackers stole data from government workstations through a compromised API key. BeyondTrust, the cybersecurity vendor, issued a security advisory on Dec. 8 after attackers used the stolen key to override the security of its Remote Support service and reach Treasury workstations.
One compromised API key in a third-party remote support service was enough to reach government systems.
The lesson is practical: scope every key to the least access it needs, rotate it on a schedule, and alert when it is used from an unexpected place. CISA notes that rotating API keys disrupts lateral movement and persistence by attackers holding stolen keys.
Advanced API security: Zero trust and real-time monitoring
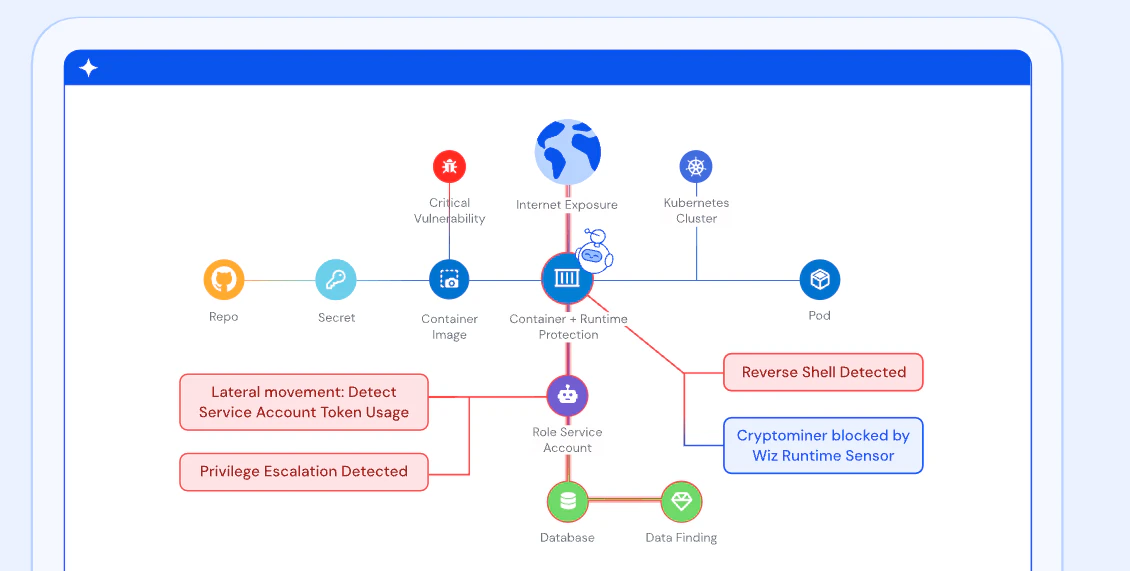
Zero trust treats every API request as potentially hostile. Each call requires fresh authentication rather than relying on session state or network perimeter trust. For service-to-service communication, mutual TLS ensures both sides verify identity before exchanging data. This is critical, as APIs connect cloud applications to AI services where a single weak endpoint can expose sensitive training data. IBM's 2025 research found one in five organizations studied had breaches linked to shadow AI.
Real-time monitoring closes the loop. Stream API logs into detection so unusual call patterns surface quickly, and use risk-based adaptive authentication to step up checks when a request looks out of character.
How Wiz strengthens API security across your cloud
Wiz API-SPM discovers every API endpoint across your cloud, documented in specs, detected at runtime, or exposed on your attack surface. The platform assesses each API for authentication gaps, excessive data exposure, and OWASP API Security Top 10 misconfigurations, then prioritizes risks by connecting vulnerabilities to cloud context.
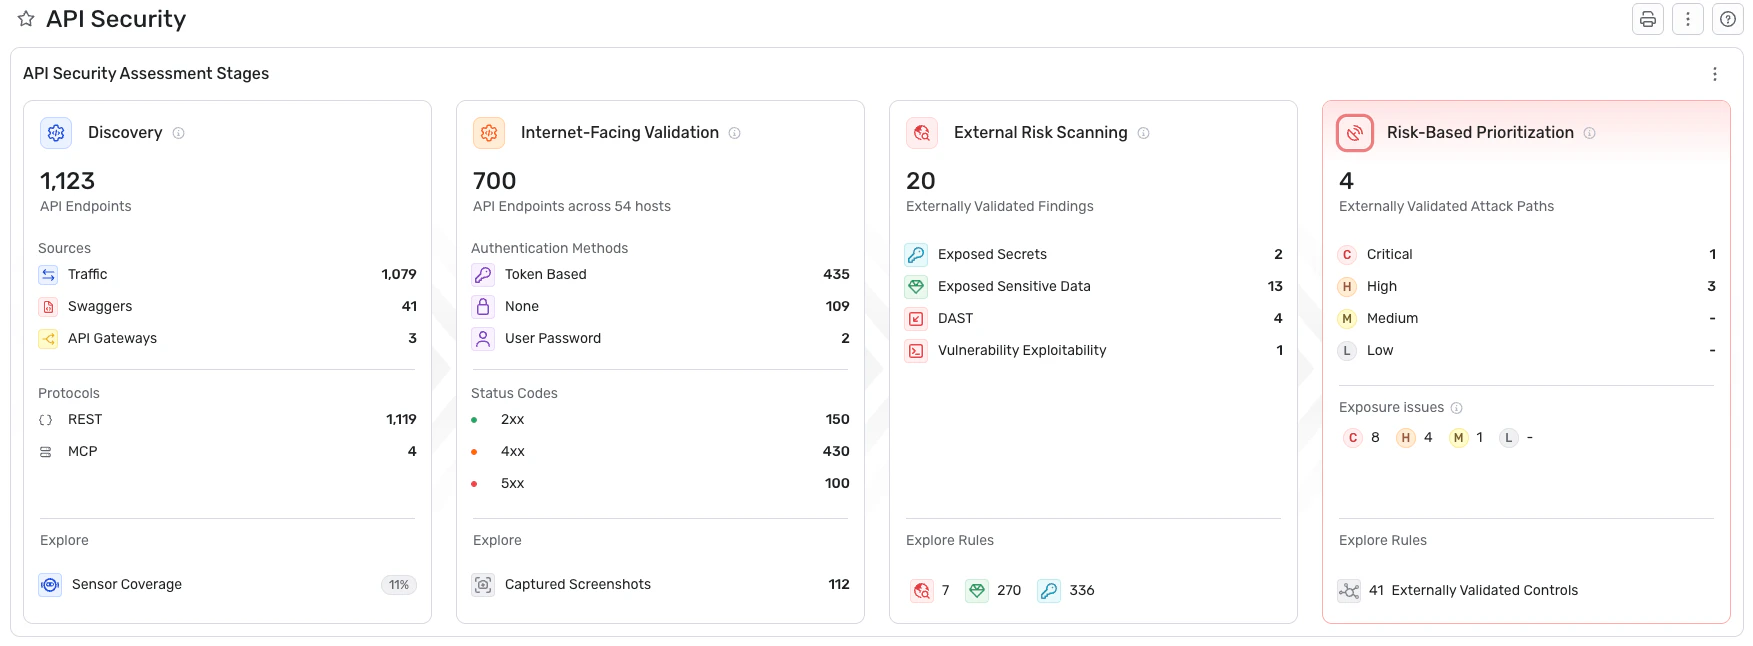
All of this runs in a single platform, so you can enforce policies, assess exposure with Attack Surface Scanner, and track API risk from build to runtime in one place.
Discover: Build a complete API inventory from Runtime Sensor, API gateways, attack surface signals, or specifications. Identify managed, unmanaged, shadow, and zombie APIs, then classify endpoints to eliminate blind spots.
Assess: Validate external exposure and dynamically test APIs for OWASP API Security Top 10 risks. Identify authentication and authorization misconfigurations, and scan for sensitive data exposure.
Prioritize: Leverage toxic combinations such as sensitive data processing, external exposure, identity permissions, and network reachability to surface the most critical issues first.
This context extends to APIs serving AI workloads, where a misconfigured model endpoint can expose training data faster than teams expect. Request a demo to see how Wiz secures your APIs and cloud environment.
An agentless, contextual approach to API security
Learn how Wiz enables customers to easily identify exposed APIs across their environment, complete with the full context of their execution layer.

FAQs about API security best practices
Other security best practices you might be interested in: