The AI Security Summit
Join Figma, Perplexity, and Wiz to learn how to monitor rogue agents, automate triage, and secure code.
Novo Modelo Operacional de IA para Segurança
Amplie o impacto da sua equipe com agentes de segurança especializados e Mika — seu onipresente companheiro de IA — tudo fundamentado no contexto do Wiz Security Graph.
Defesa de código para nuvem alimentada por IA
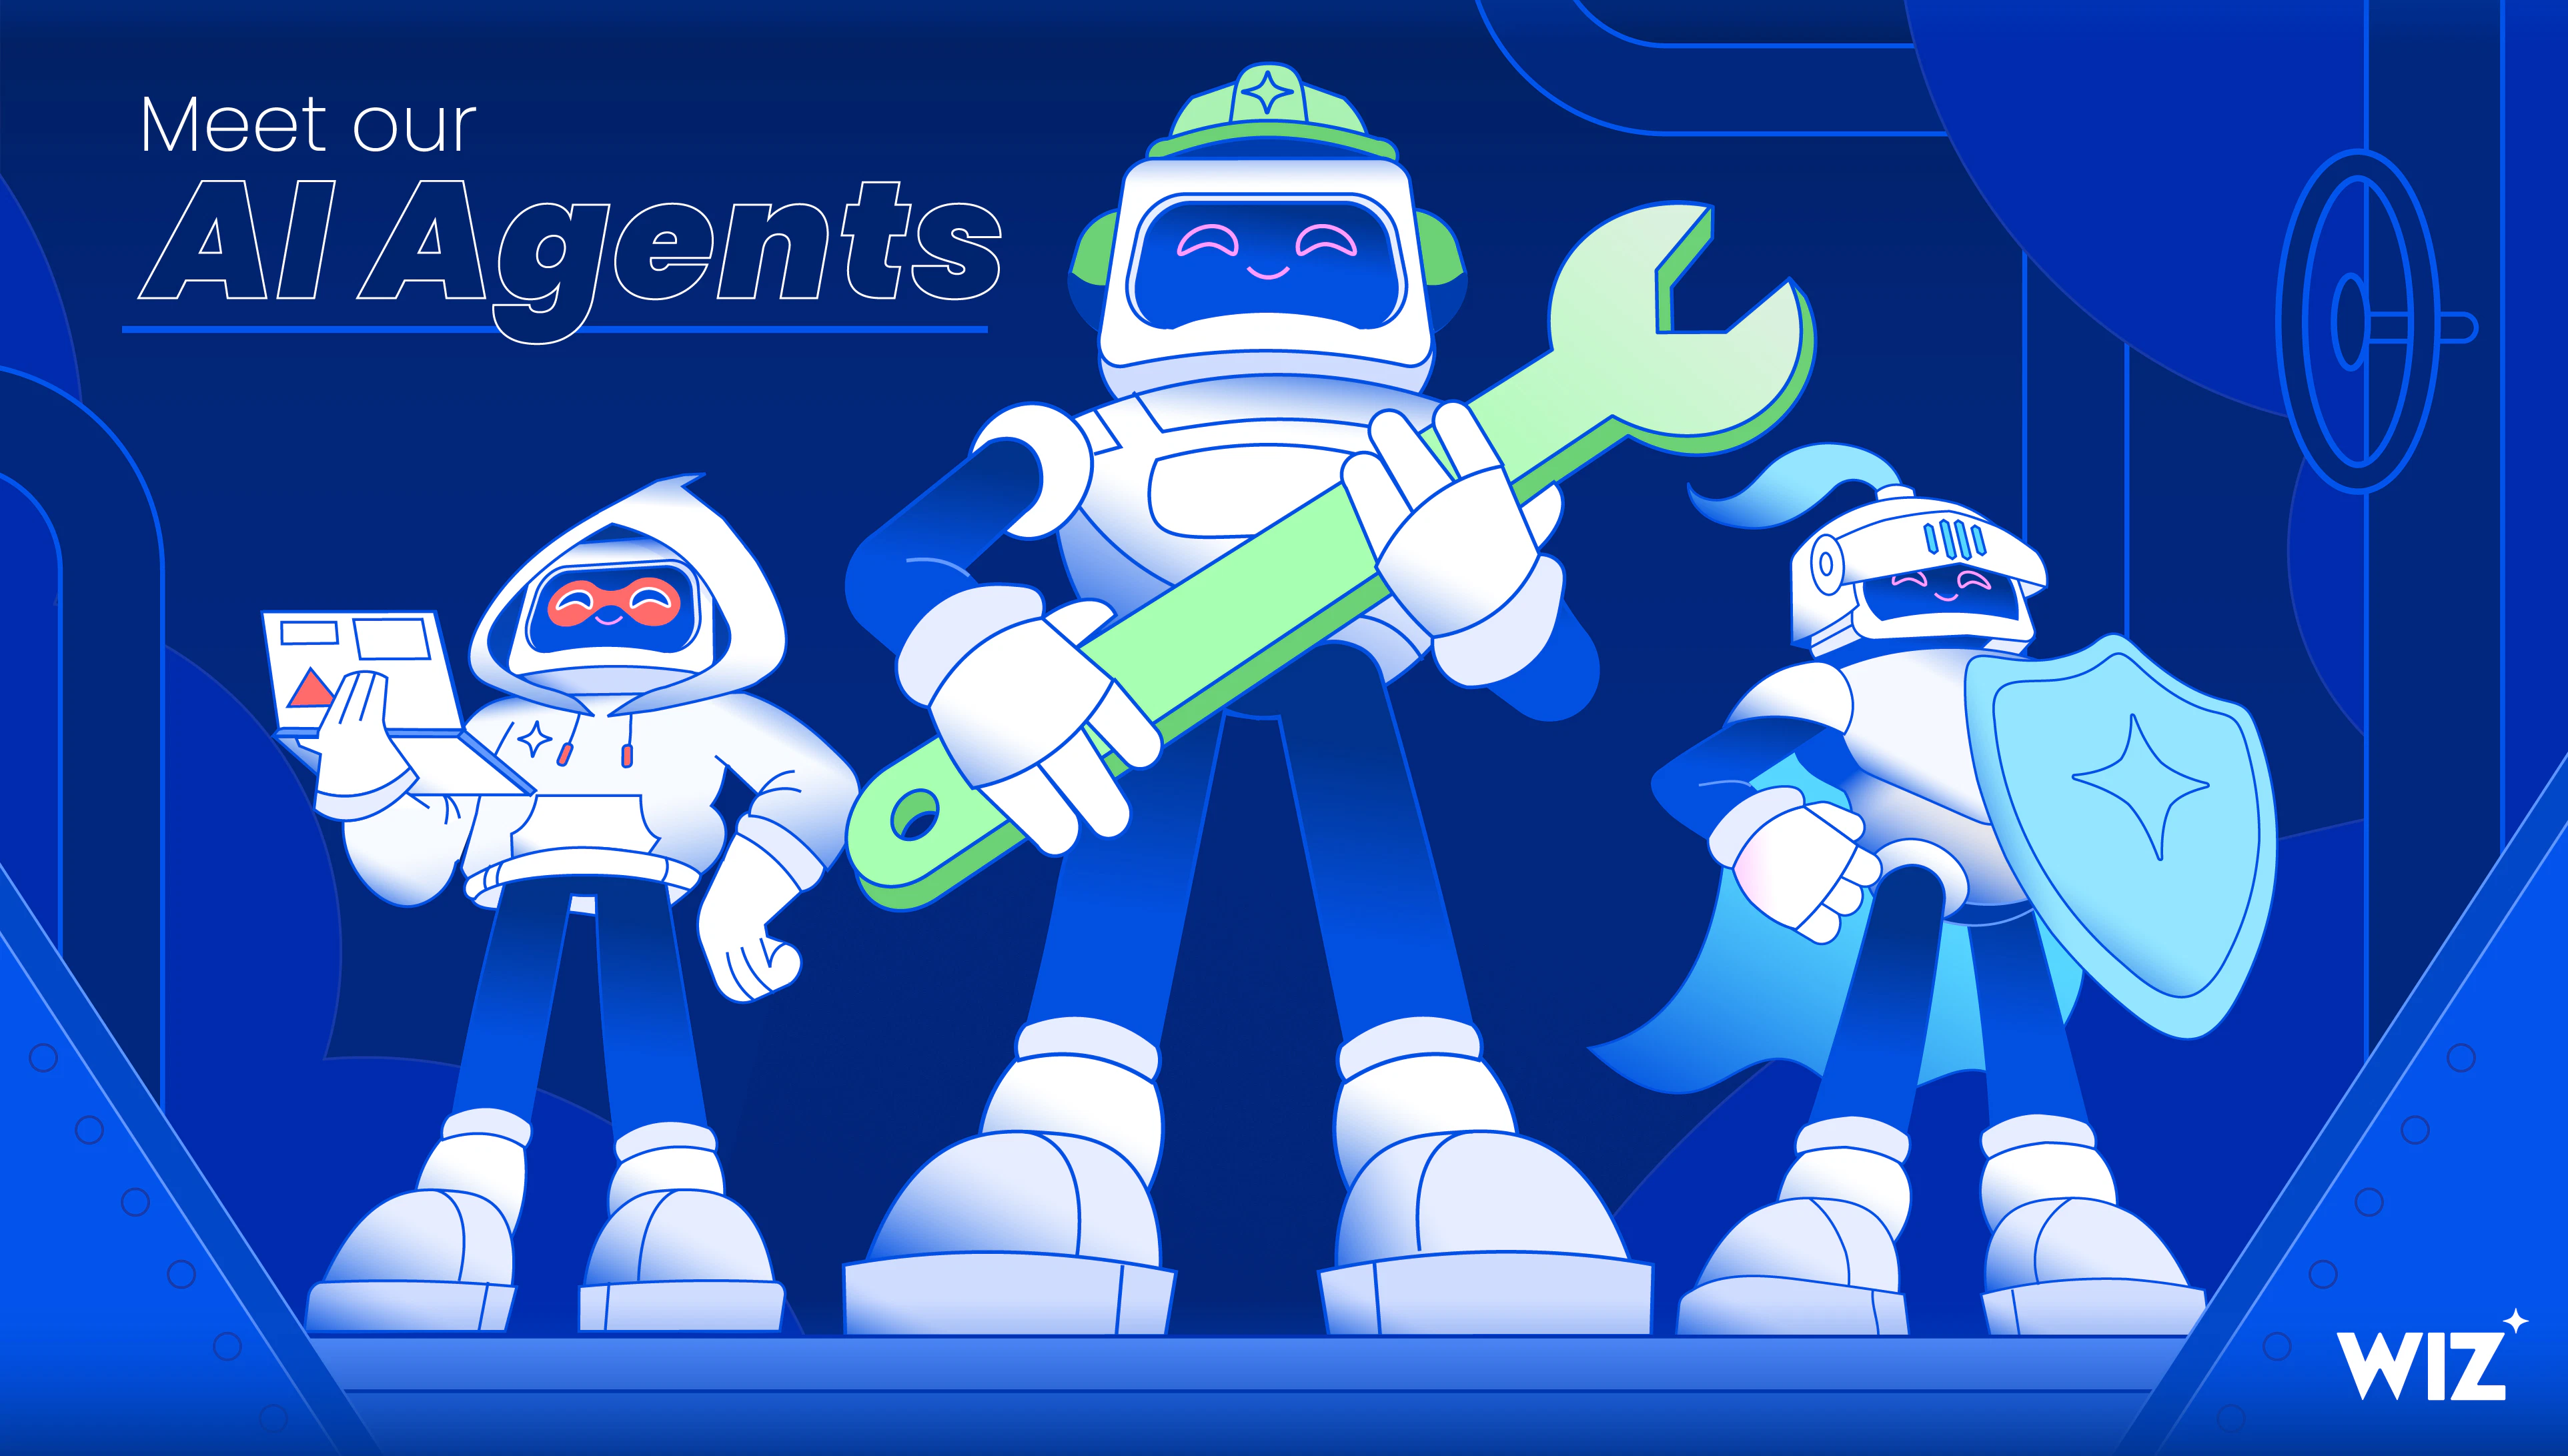
Multiplicador de força da sua equipe: agentes especializados de IA que trabalham juntos para eliminar o trabalho manual e acelerar todas as fases do ciclo de vida da segurança.
Bem, bem,… Um ponto final exposto. Vamos ver até onde isso vai.
Simula continuamente caminhos de ataque reais através da sua nuvem e da pilha de IA para provar o que é realmente explorável, eliminando ruídos teóricos e revelando os riscos que realmente importam.
Modo detetive ativado… Vamos ver o que realmente aconteceu.
Investiga alertas de forma autônoma em nuvem e código, correlaciona as evidências de ponta a ponta e entrega um veredito claro e defensável com raio total de potencia.
Boa captura. Vamos acabar com esse crítico.
Preenche a lacuna entre encontrar e corrigir gerando remediação consciente do contexto na fonte — impulsionando as equipes para um risco crítico zero.
Visita guiada
Faça o tour guiado interativo abaixo
Mika traz a inteligência do Wiz Graph e agentes especializados para suas ferramentas diárias, para que você possa tomar decisões informadas sem nunca sair do seu fluxo de trabalho.

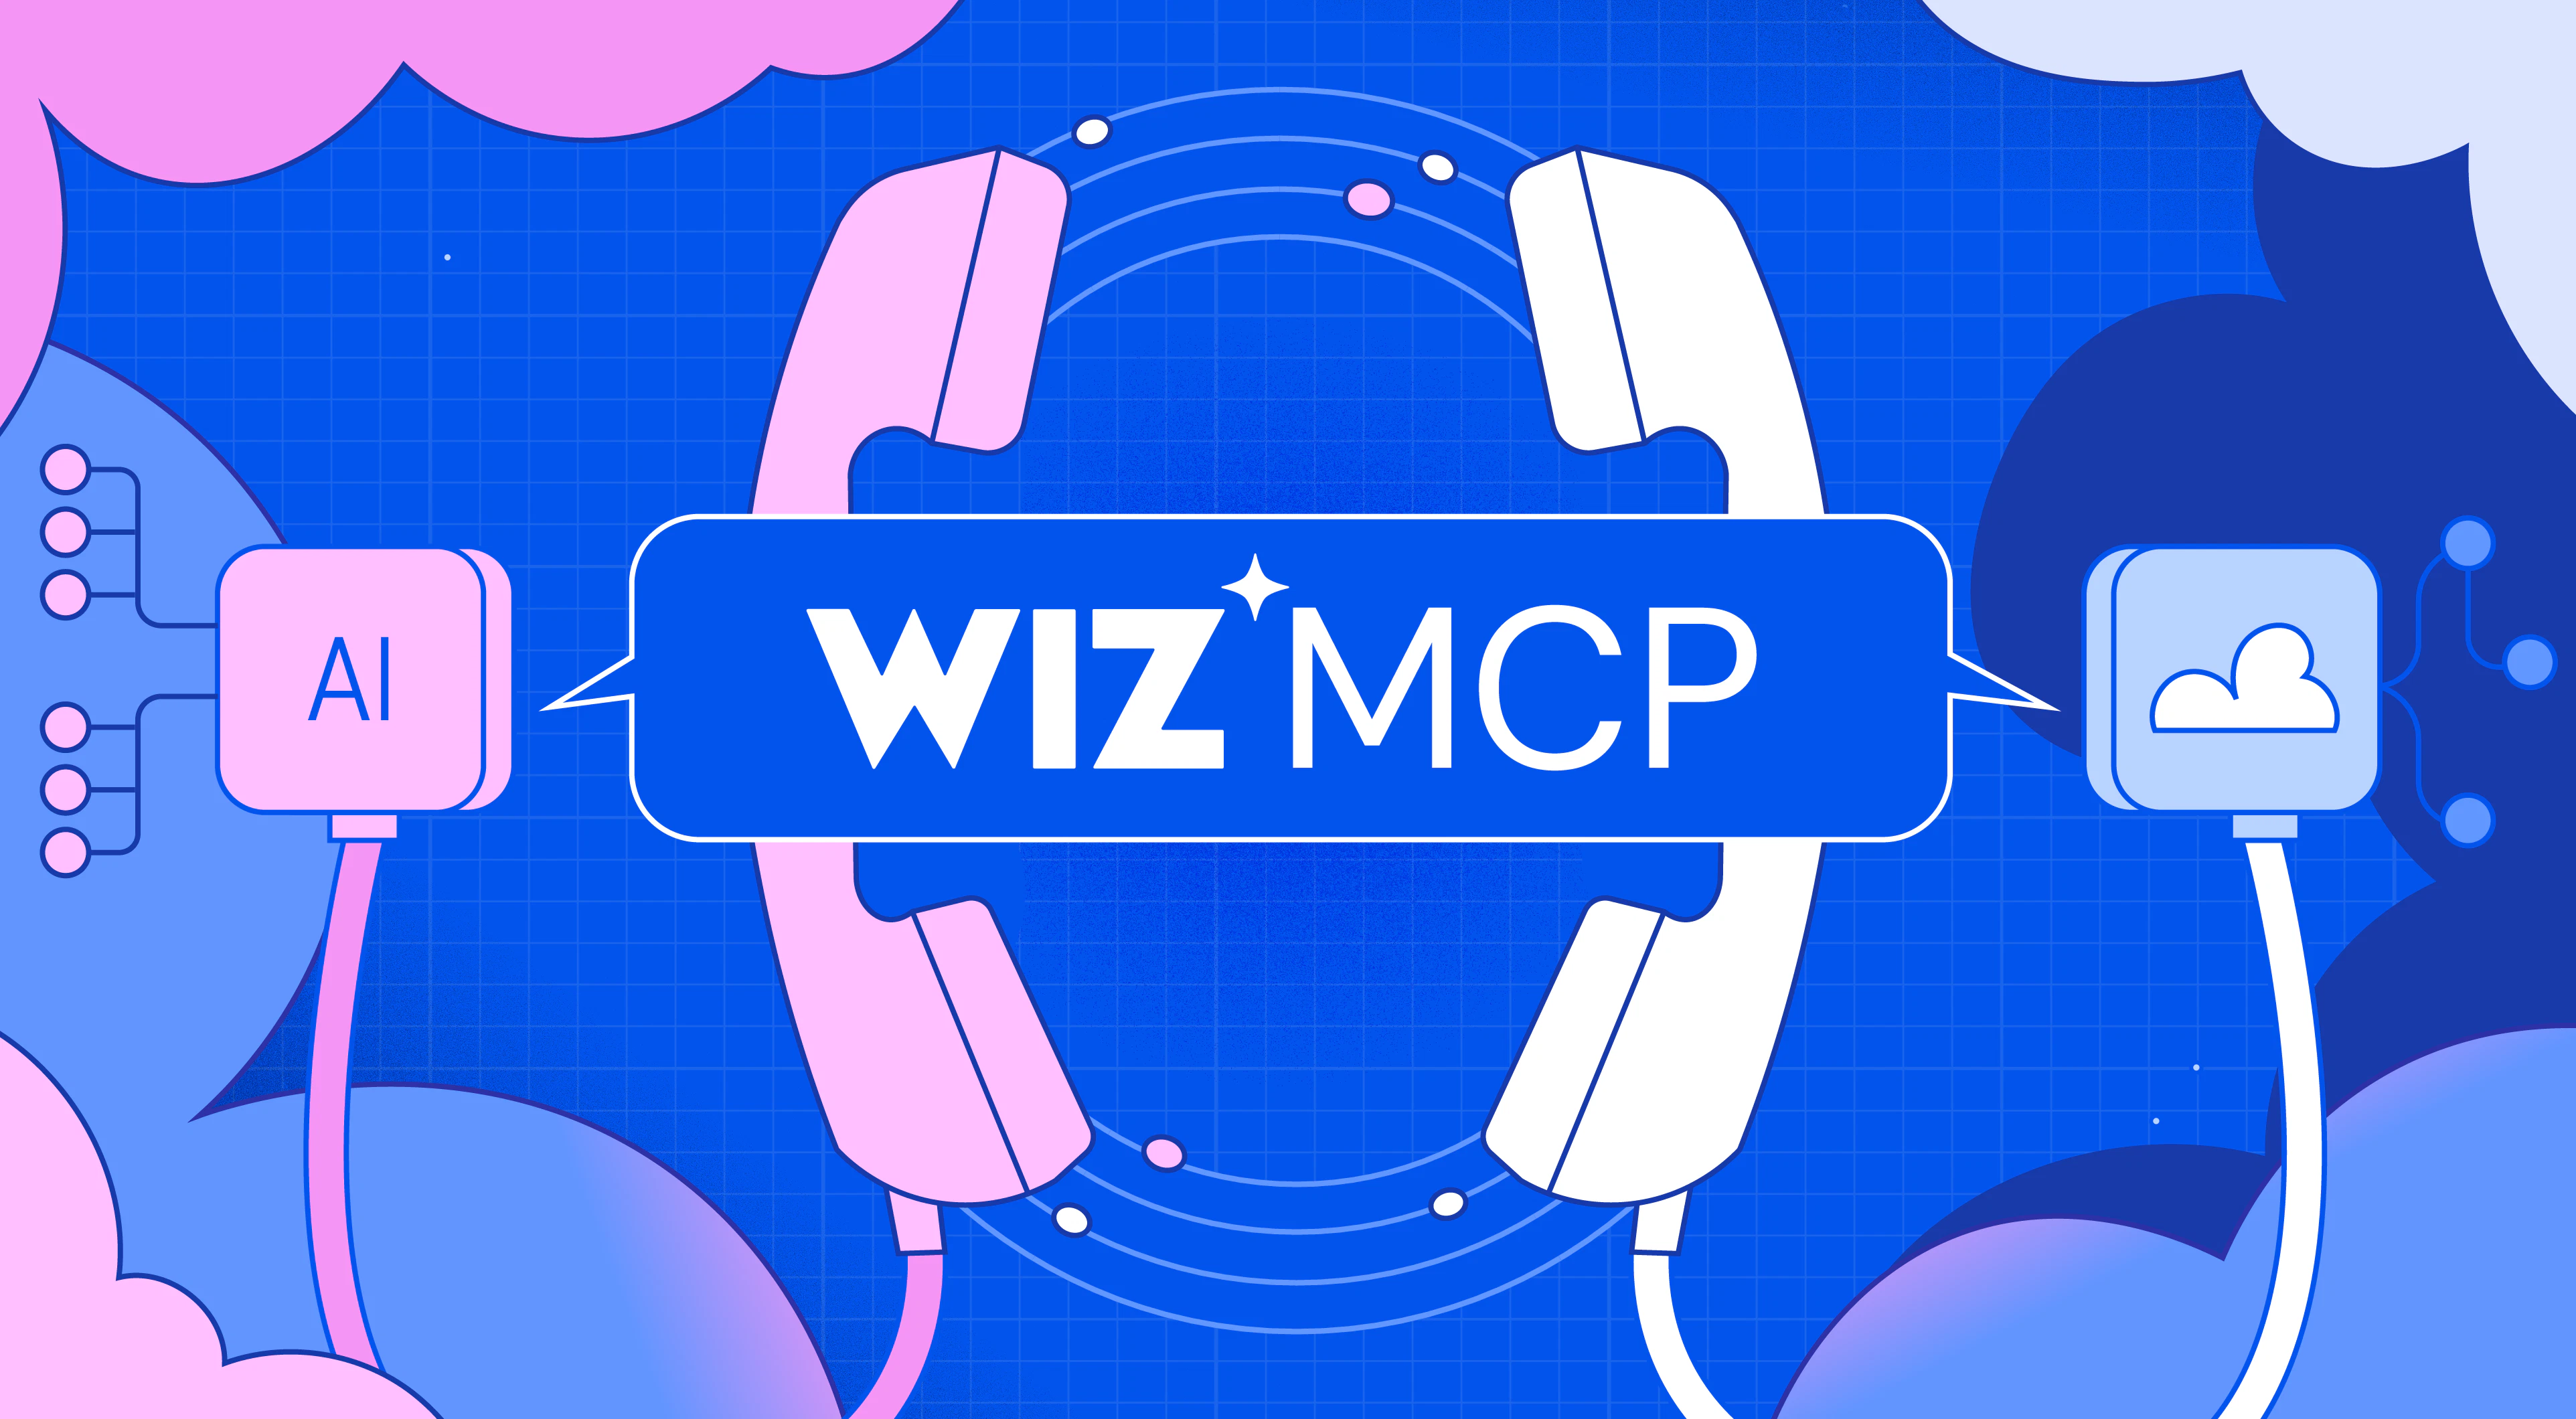
O Gateway para Automação Personalizada - O Wiz MCP Server permite que você conecte o Security Graph diretamente aos seus agentes personalizados, bases de conhecimento internas e IDEs de desenvolvedores. Construa fluxos de trabalho personalizados que combinem a inteligência do Wiz com seus dados únicos de negócio para automatizar a segurança em todos os lugares onde você trabalha.

Red Agent finds what humans miss. It caught critical authorization flaws across services where traditional testing and our bug bounty program came up short. We had continuous AI-powered attack surface testing on our roadmap. Wiz got there first, and did it better than we would have.

We are now fully relying on the Blue Agent for some of the low severity alerts. Instead of having a lot of tickets, it's just one task at the end of each shift — checking all those detections that have been closed by the Blue Agent. That is allowing our team to focus more on the advanced work.

The Green Agent creates a Jira ticket with the full description, attack path analysis, and remediation steps already populated. Developers have everything they need to act immediately.

What is most amazing about Red Agent is the way that we can track and get alerting or visibility on endpoints that can be attacked or manipulated from the outside. It tells me: 'You have an endpoint here, you are missing authentication,you have an exposure.' All of those insights are really, really helping me to close gaps fast.

My favorite thing about the Blue Agent is how quickly it helps us understand why an alert happened and what it actually means in our environment.

At first we continued our manual investigation side by side with the agents, but 10 out of 10 times we were getting the same threat assessment conclusions, building this trust enabled us to rapidly accelerate.

AI workflows with Wiz MCP connectivity ensure our minimum level of triage is the same high standard our systems maintain consistently.
Crie Seus Próprios Manuais de Segurança: Direcione Mika e seus agentes especializados com uma tela visual sem código. Encadeie ações em sequências automatizadas personalizadas — desde triagem instantânea até remediação em larga escala — adaptadas à lógica de resposta única da sua organização.