
Understanding AI SAST in modern application security
AI SAST is static application security testing enhanced with artificial intelligence to make code scanning more accurate, contextual, and actionable. You still perform static analysis on source or compiled code, but AI helps teams understand which findings matter and how to fix them.
Traditional SAST examines code without running it – unlike DAST, which analyzes a live application – and identifies vulnerabilities such as SQL injection, command injection, insecure deserialization, and unsafe input handling. While essential, these scanners often overwhelm teams with noisy findings, inconsistent rule quality, and limited context about what is actually exploitable.
AI SAST addresses these limits by adding an intelligent reasoning layer on top of the scanner. Instead of treating every flagged pattern as equal, AI can interpret the code, group related issues, and summarize the real risk in clear, developer-friendly language.
Think of the difference this way:
Traditional SAST: A rules engine that flags every pattern it’s configured to detect.
AI SAST: A smart reviewer that interprets the results, understands how your application works, and highlights what needs attention first.
This matters even more as teams build microservices, adopt multiple languages, and increasingly rely on AI-generated code – which studies show often introduces security flaws. AI SAST helps teams navigate this complexity by reducing noise and surfacing the issues most likely to create real exposure in production.
But AI alone isn’t enough. AI SAST becomes most powerful when paired with environment context – linking code findings to the cloud services, identities, and data they impact. This shift turns static analysis from a list of patterns into a view of actual attack paths and risks that matter.
Get the Application Security Best Practices [Cheat Sheet]
This 6-page guide goes beyond basics — it’s a deep dive into advanced, practical AppSec strategies for developers, security engineers, and DevOps teams.

How AI transforms static application security testing
The SAST scanner still performs the foundational work: parsing code, tracing data flows, and applying security rules. AI then builds on this raw output to deliver cleaner, more contextual, and more actionable results. This shift turns static analysis from a noisy signal into a risk-focused workflow developers can trust.
Smarter detection through code understanding
AI models excel at interpreting patterns and meaning in text, and source code is no exception. When applied to static analysis, AI can:
Recognize custom or framework-specific patterns that rigid rules often miss.
Follow complex, multi-service data flows, even when they cross language or repository boundaries.
Reason across mixed stacks –modern applications that combine multiple languages, frameworks, and autogenerated code.
This enables richer detection while reducing brittle rules and false alarms that plague traditional scanners.
Automated triage and meaningful noise reduction
For most teams, the bottleneck in SAST isn’t finding issues – it’s triaging them. AI dramatically improves this step by:
Grouping hundreds of similar alerts into a handful of root-cause issues.
Eliminating duplicates created by overlapping rules or repeated patterns across services.
Flagging likely false positives based on deeper code understanding and surrounding context.
Instead of a wall of alerts, teams get a smaller, higher-confidence set of issues they can fix quickly. This AI-assisted triage is the foundation of the SAST AI Agent in Wiz Code, which turns raw scanner output into a clear, deduplicated issue list.
Better prioritization through real environment context
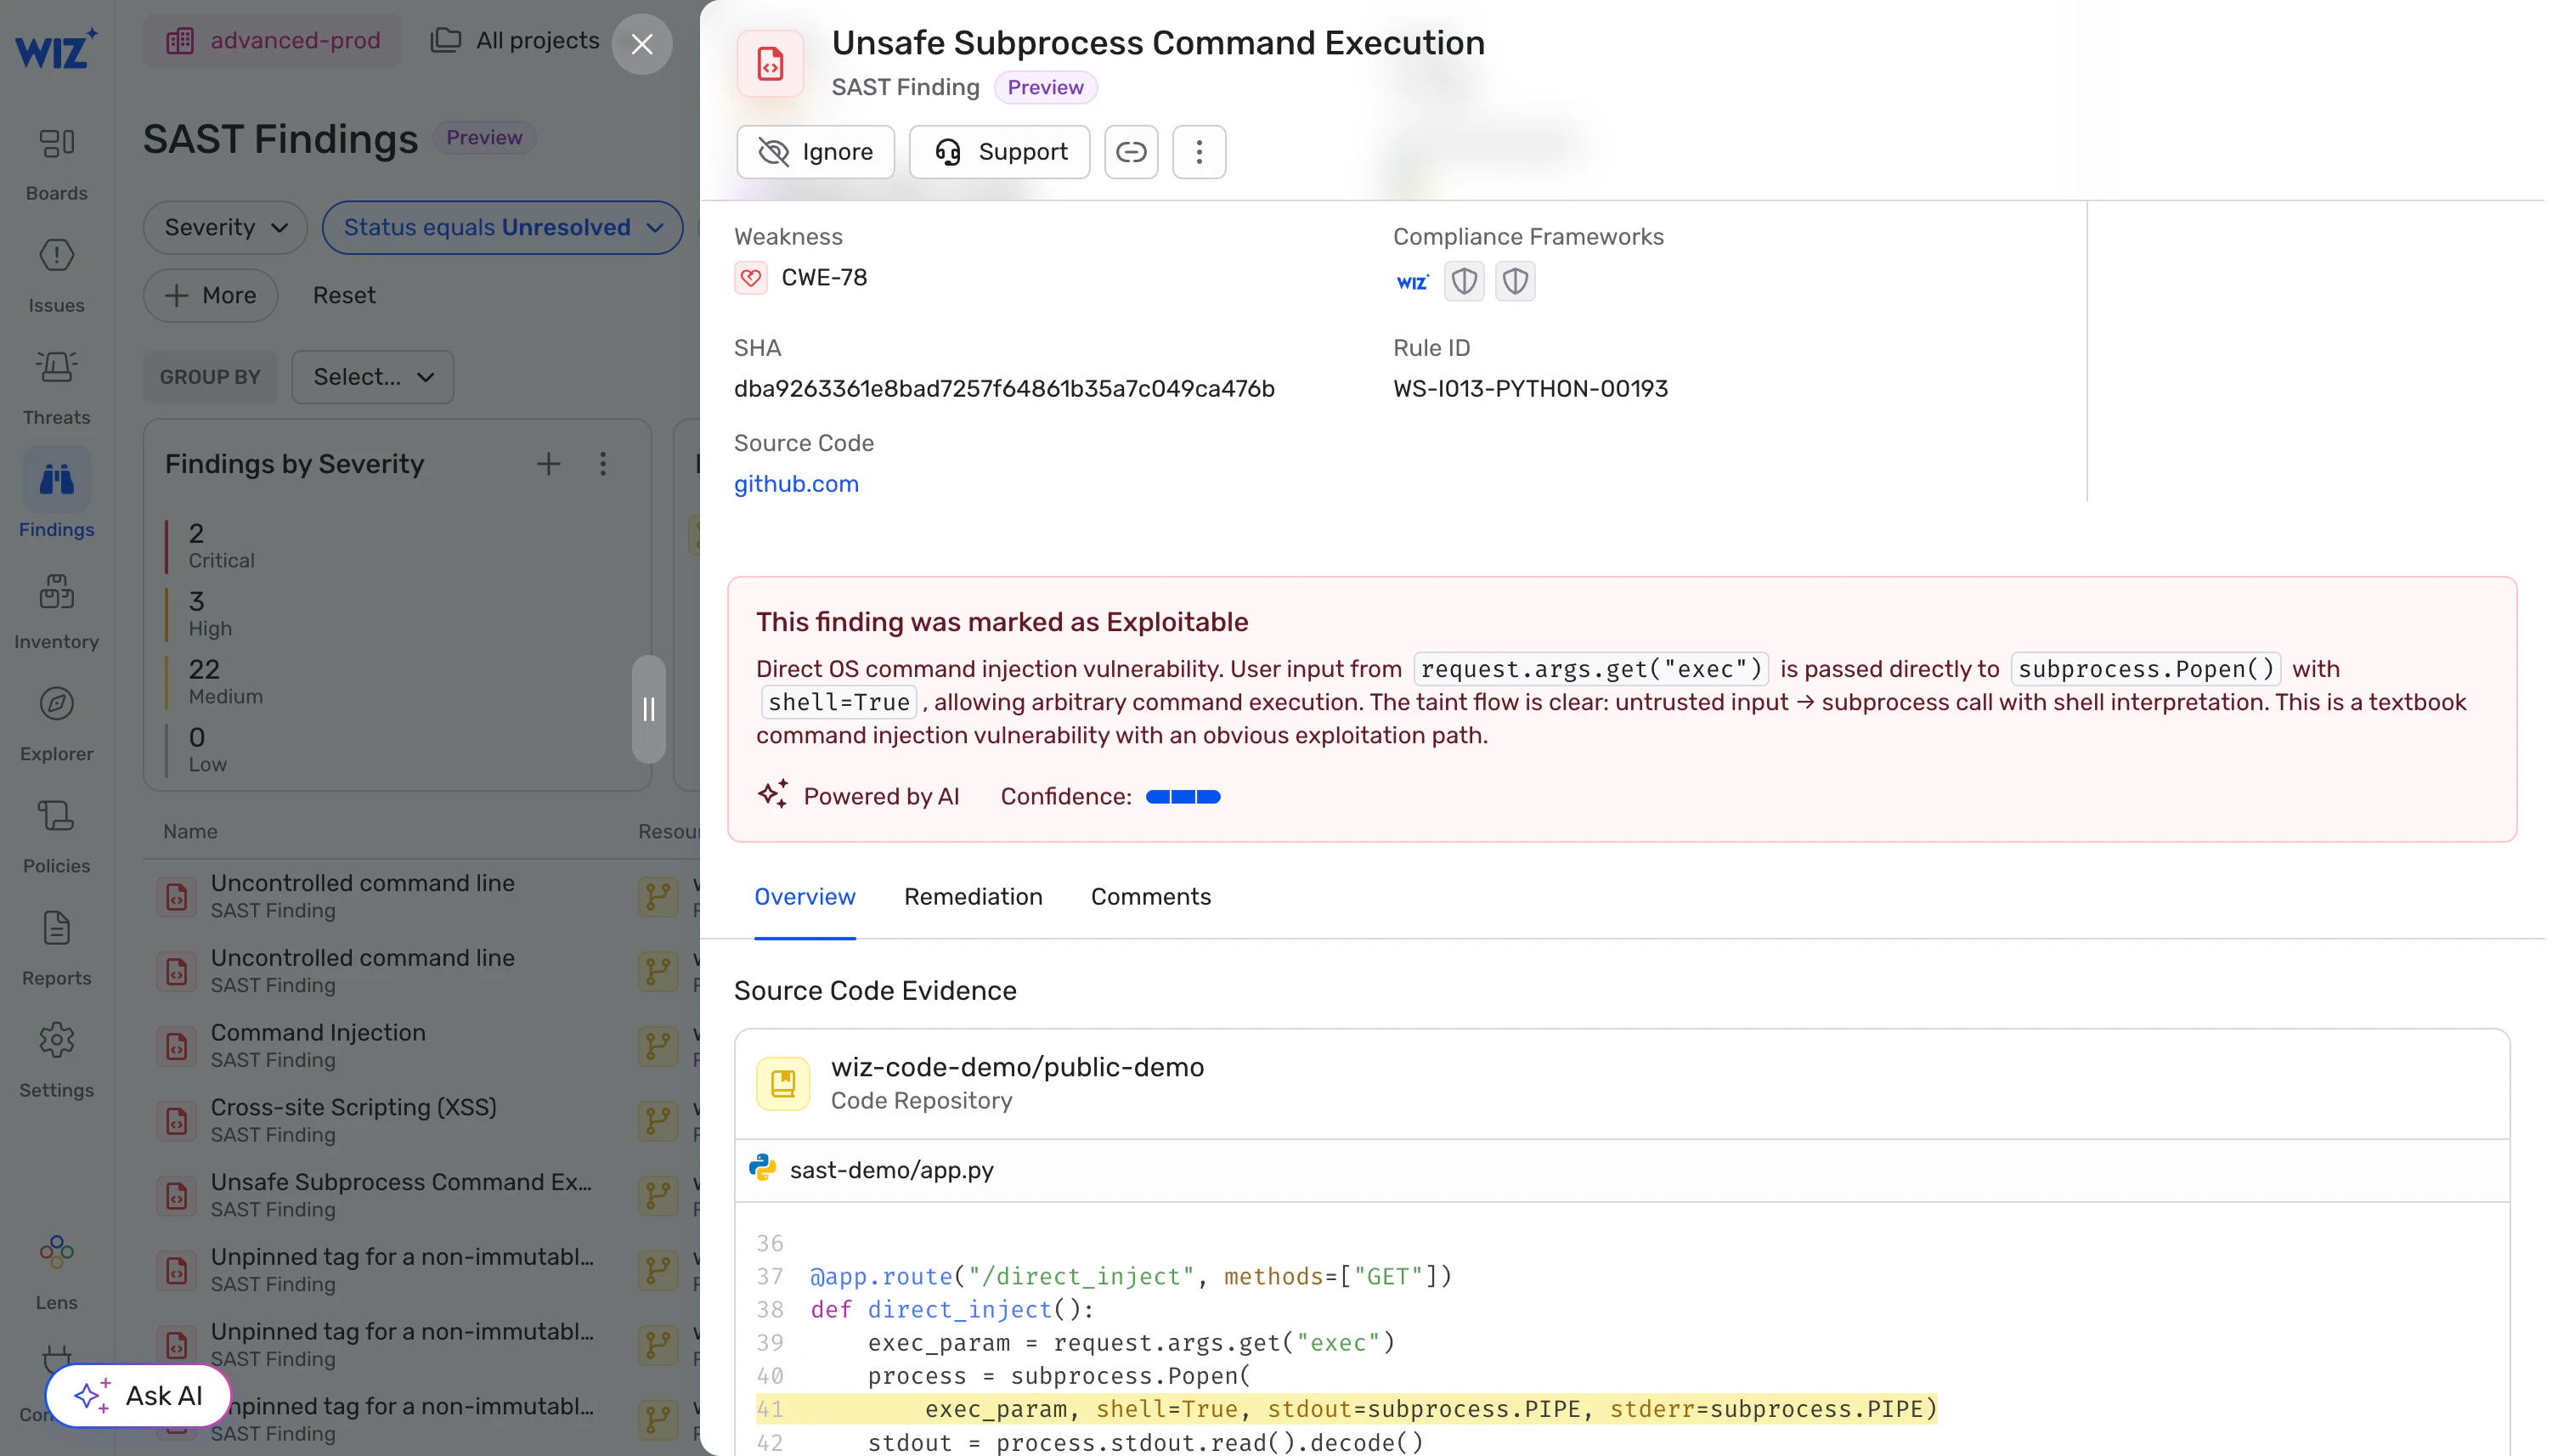
A code issue isn’t inherently “high severity” until you know how and where it runs. AI SAST becomes significantly more powerful when it incorporates:
Cloud infrastructure context
Identity and permission data
Runtime signals and exposure
Dependency and supply chain information
With this context, you move from “this pattern is dangerous” to “this issue creates an exploitable attack path in production.”
This is the core of Wiz’s approach: connecting code-level findings to the cloud resources, identities, and data stores they affect so teams can fix risks, not just fix findings.
Clear explanations and actionable fixes
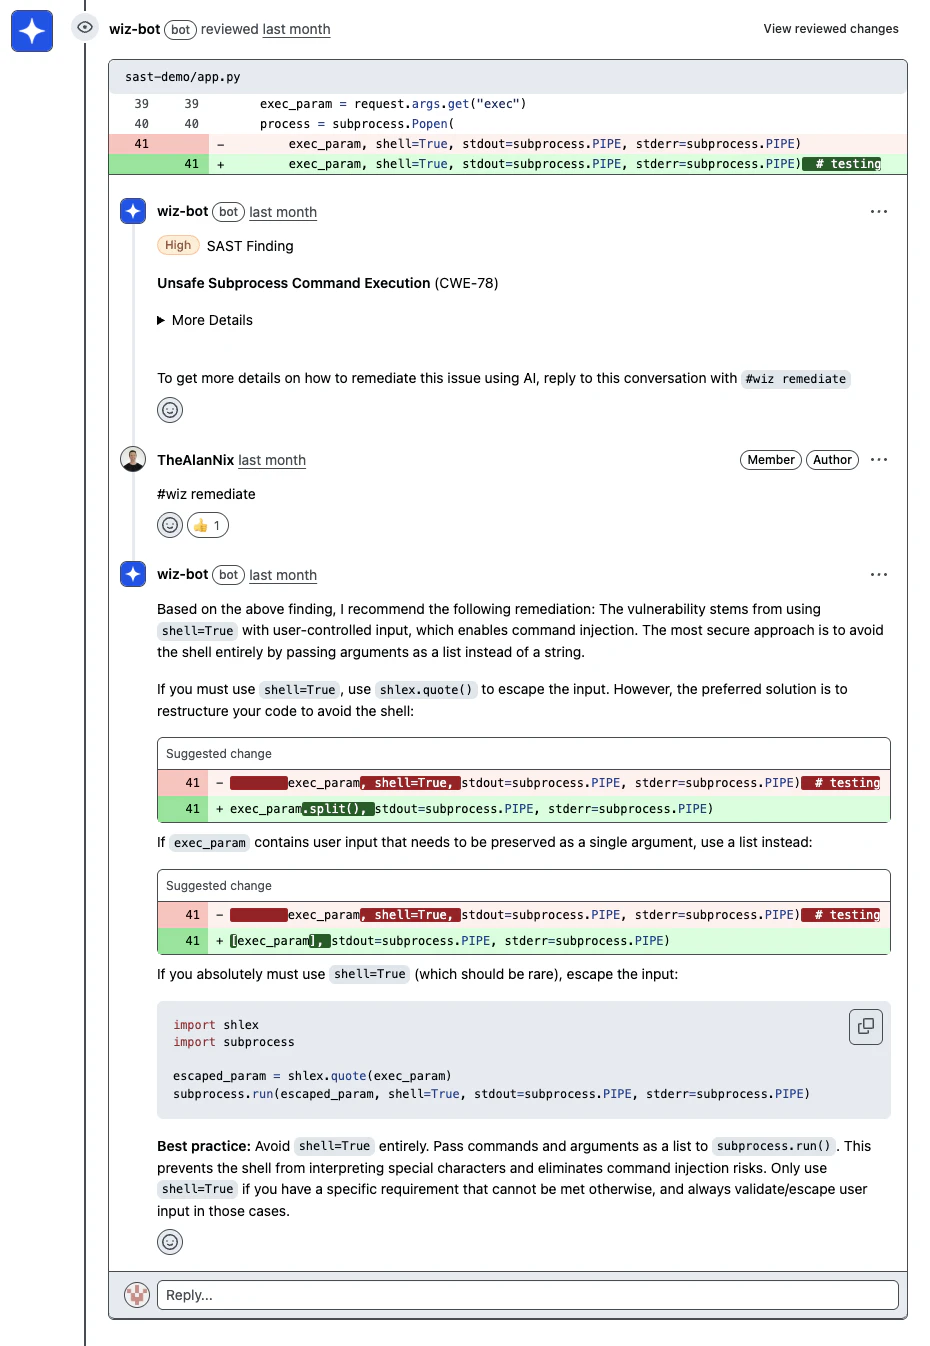
Finding an issue is only half the work – developers need to understand what to do next.
AI helps by generating:
Concise, plain-language summaries of what’s wrong
Data flow explanations or diagrams showing how untrusted input moves
Code-level remediation suggestions aligned with the project’s libraries and idioms
These suggestions always require human validation, but they give developers a strong head start and reduce back-and-forth with security teams. Delivered directly in the IDE, pull request, or CI output, this makes security feel integrated – not bolted on.
Watch 5-min demo
Learn how Wiz Code scans IaC, containers, and pipelines to stop misconfigurations and vulnerabilities before they hit your cloud.

How to evaluate AI SAST solutions
Choosing an AI SAST solution means looking beyond flashy AI claims and assessing whether the platform can reliably reduce noise, surface real risk, and accelerate fixes. The strongest platforms demonstrate measurable improvements across detection quality, triage efficiency, developer experience, and contextual risk understanding.
Evaluate solutions across these dimensions:
Detection accuracy and coverage
A strong AI SAST platform maintains the rigor of a traditional static analysis engine while improving precision.
Evaluate:
Precision and recall against known vulnerable test suites (e.g., OWASP Benchmark, Juliet)
Coverage across your stack –Java, JavaScript/TypeScript, Python, Go, C#, IaC templates, etc.
Handling of framework-specific patterns that rigid rule sets miss
Support for polyglot and microservice architectures
AI should improve detection quality, not disguise weak scanning.
Noise reduction and triage efficiency
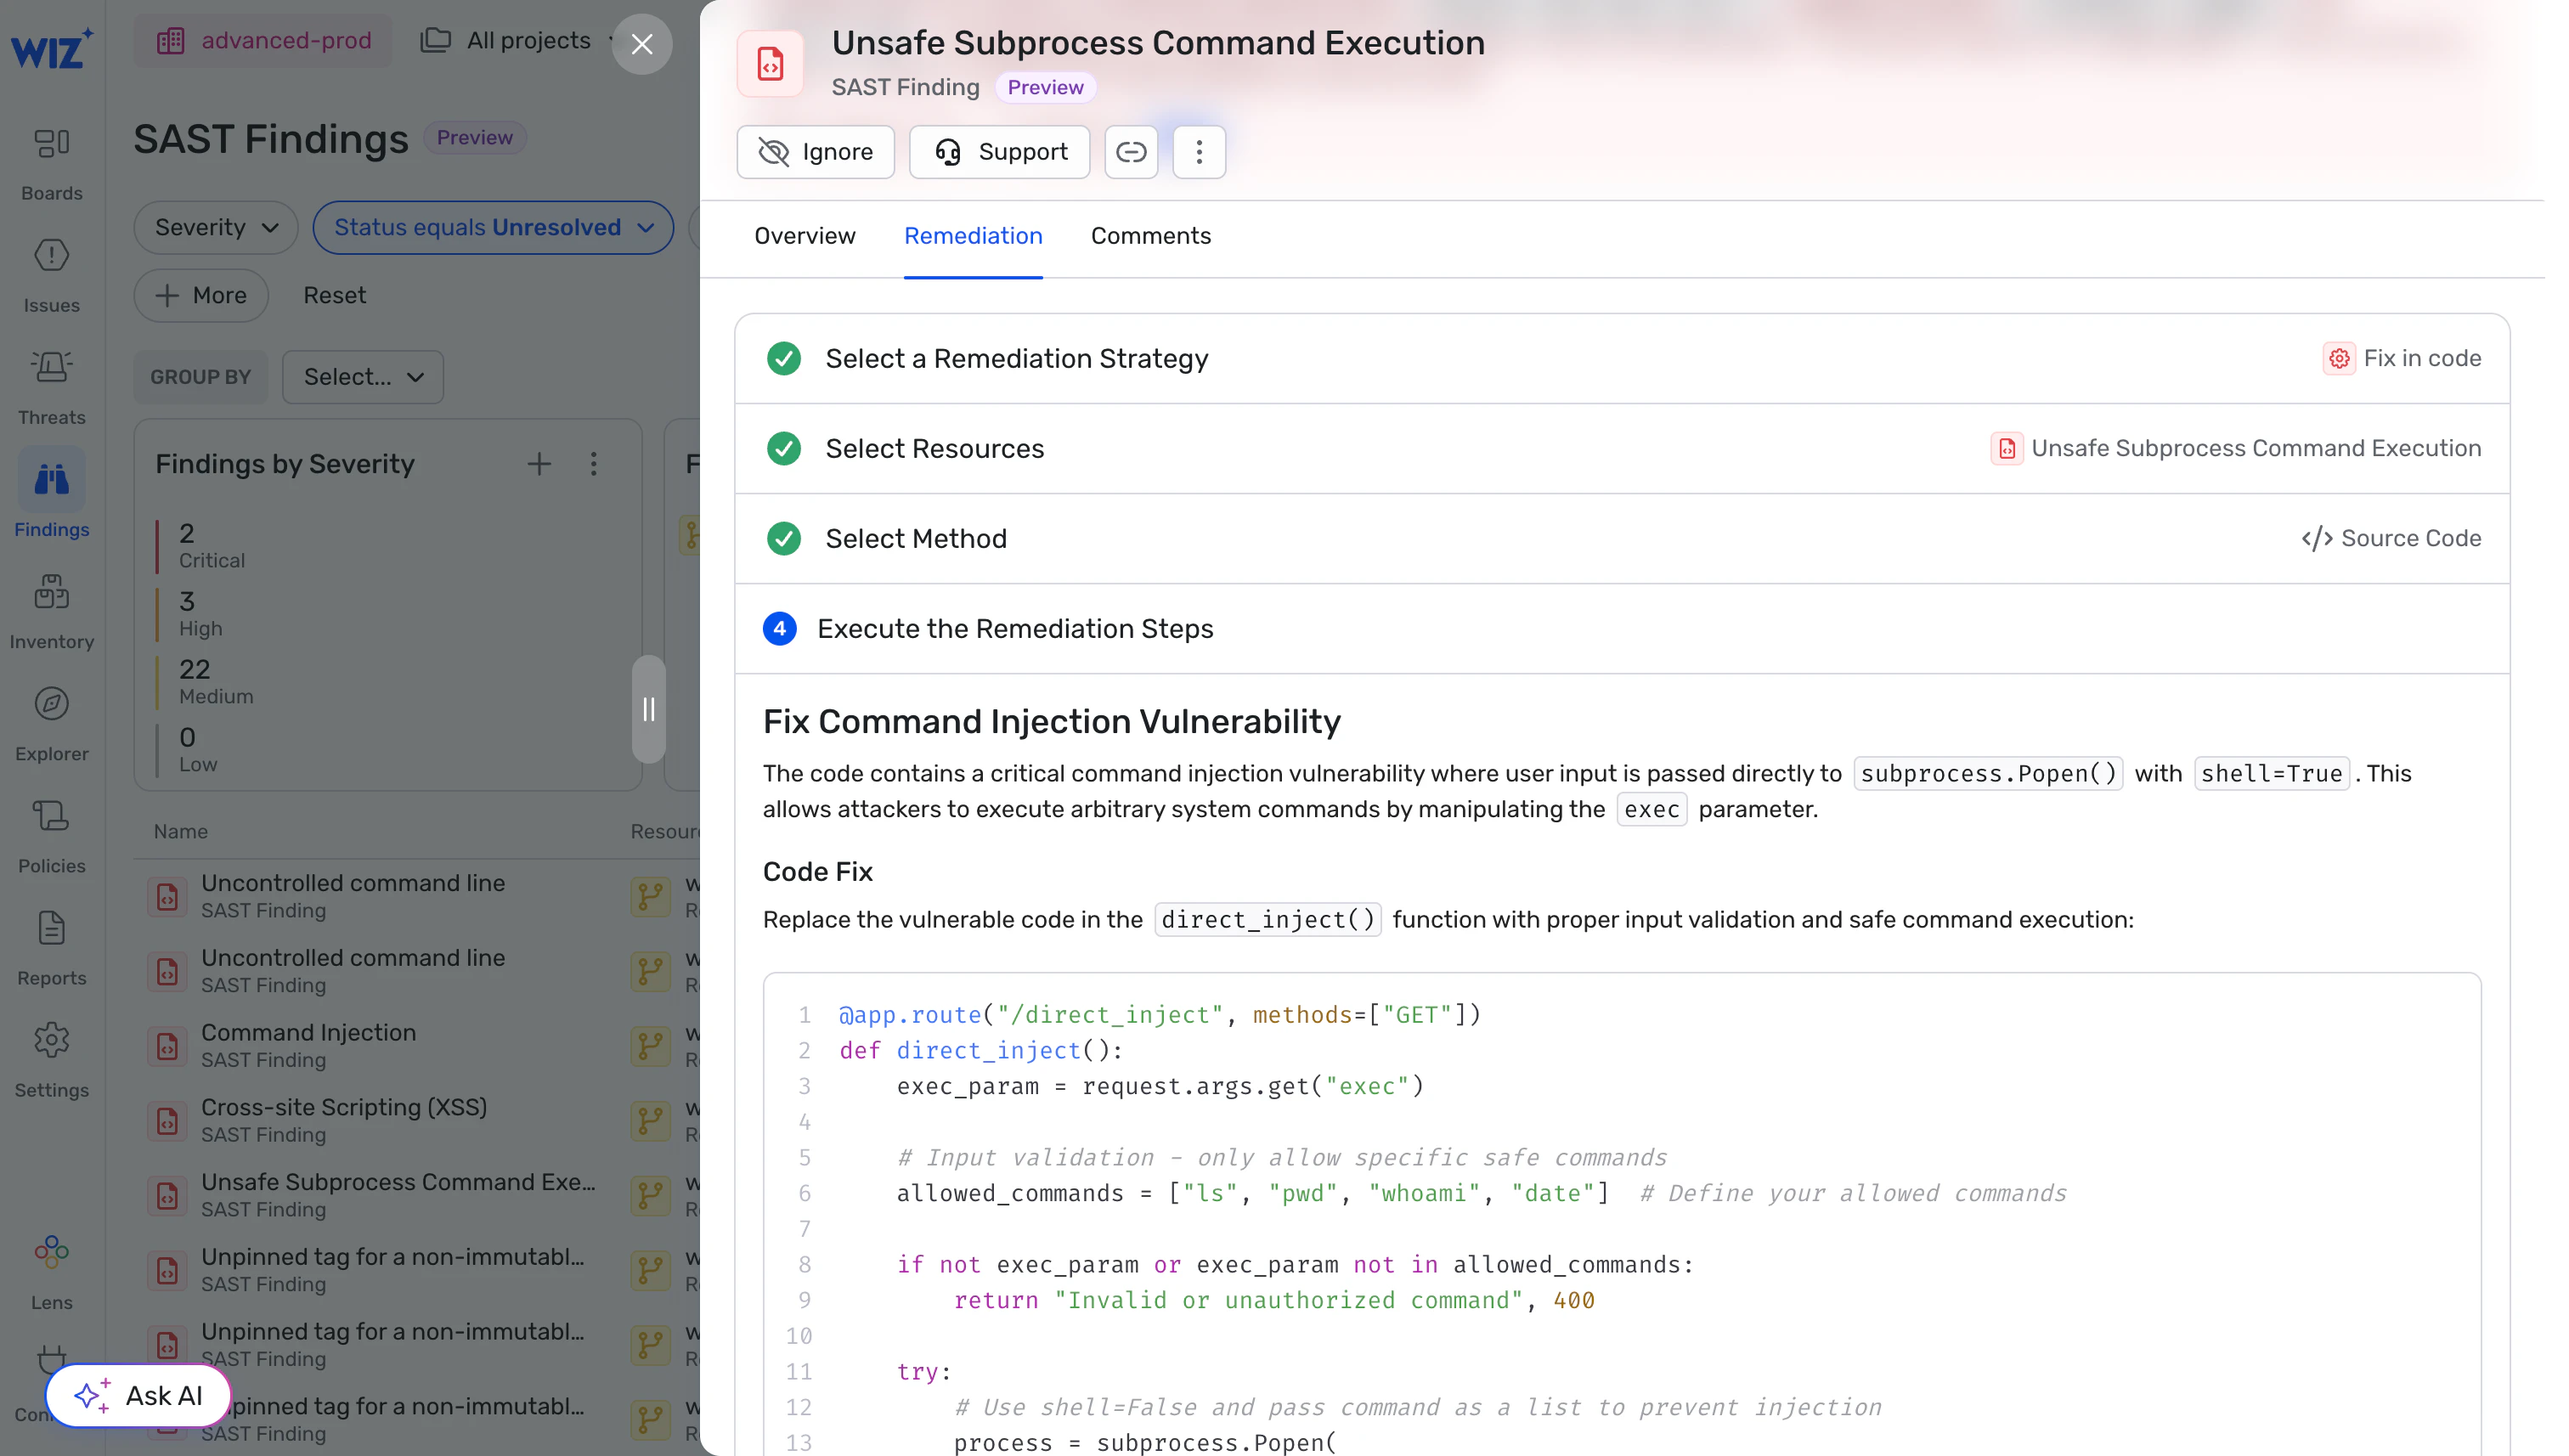
AI SAST should dramatically reduce the work required to get to an actionable issue list.
Measure:
False positive reduction (30–50% is a strong benchmark)
Time-to-triage (MTTT) from scan completion to a clean, grouped, prioritized list (<5 minutes is ideal)
Reduction in duplicate or redundant findings across microservices
Meaningfulness of grouping – multiple alerts collapsed into root-cause issues
This is core to the SAST AI Agent in Wiz Code, which turns thousands of raw findings into a structured, deduplicated set of issues.
Risk-based prioritization with real environment context
A modern AI SAST tool should not prioritize solely based on patterns. It should understand where the code runs and what it can impact.
Evaluate whether the platform can:
Connect SAST + SCA + IaC data
Map findings to the cloud resources and identities that execute them
Identify exploitable attack paths, not theoretical patterns
Incorporate runtime signals and data exposure levels
This is the primary differentiator of Wiz’s approach: code findings enriched with cloud context to highlight what is actually exploitable in production.
Developer experience and fix acceleration
AI SAST must fit seamlessly into developer workflows – and actually help developers fix issues faster.
Look for:
Clear explanations and data flow visualizations
High-quality code suggestions that match the project’s style
IDE guardrails that catch risky patterns before commit
CI/PR integrations that surface guidance in the tools developers already use
Fix acceptance rate, ideally >60% for AI-generated suggestions
The more the tool reduces friction, the more likely issues are to be fixed quickly.
Ownership mapping and automation
AI should help eliminate manual routing work by identifying who owns a particular issue.
Evaluate:
Automatic mapping to repos, services, and teams
Integration with CODEOWNERS, service catalogs, or monorepo metadata
Contextual fields (e.g., cloud account, runtime environment) to help owners understand impact
Support for SLA policies based on exposure levels
This is essential for reducing MTTR and enabling at-scale remediation.
Wiz's approach to AI SAST
Rules-based SAST catches known patterns, but plenty of serious bugs depend on what the code is meant to do. Wiz AI SAST reasons about how an application behaves to find those logic-based flaws. Think broken access control, insecure direct object references (IDOR), flawed input validation, and misapplied cryptography. It runs alongside deterministic Wiz SAST, which keeps handling those patterns.

Under the hood, AI SAST runs on the harness behind Atlas, Wiz's autonomous AI vulnerability researcher. Wiz grounds each investigation in the Wiz Security Graph, so the model sees infrastructure, identity, and runtime.
That context shows you whether an issue is reachable or touches sensitive data. For example, picture an IDOR in an internet-facing API that returns customer records. Here is how the workflow fits together:
Focused scans: Teams point AI scanning at their most critical repositories, since not every codebase needs deep AI reasoning.
Stable results: Automated retests and deduplication across scans keep the issue list steady.
Checkable evidence: Each finding ships with a confidence score, an investigation summary, and reproduction commands.
Root-cause fixes: The Green Agent investigates the underlying findings and builds a plan to fix the root cause.
Put together, a logic bug moves from detection to a fix plan with its context intact. To see how Wiz Code connects code risks to cloud context, request a demo.
Catch code risks before you deploy
Learn how Wiz Code scans IaC, containers, and pipelines to stop misconfigurations and vulnerabilities before they hit your cloud.
