The AI Security Summit
Join Figma, Perplexity, and Wiz to learn how to monitor rogue agents, automate triage, and secure code.
Nuevo modelo operativo de IA para la seguridad
Escala el impacto de tu equipo con agentes de seguridad especializados y Mika—tu omnipresente compañero de IA—todo en el contexto del Wiz Security Graph.
Defensa de código a nube impulsada por IA
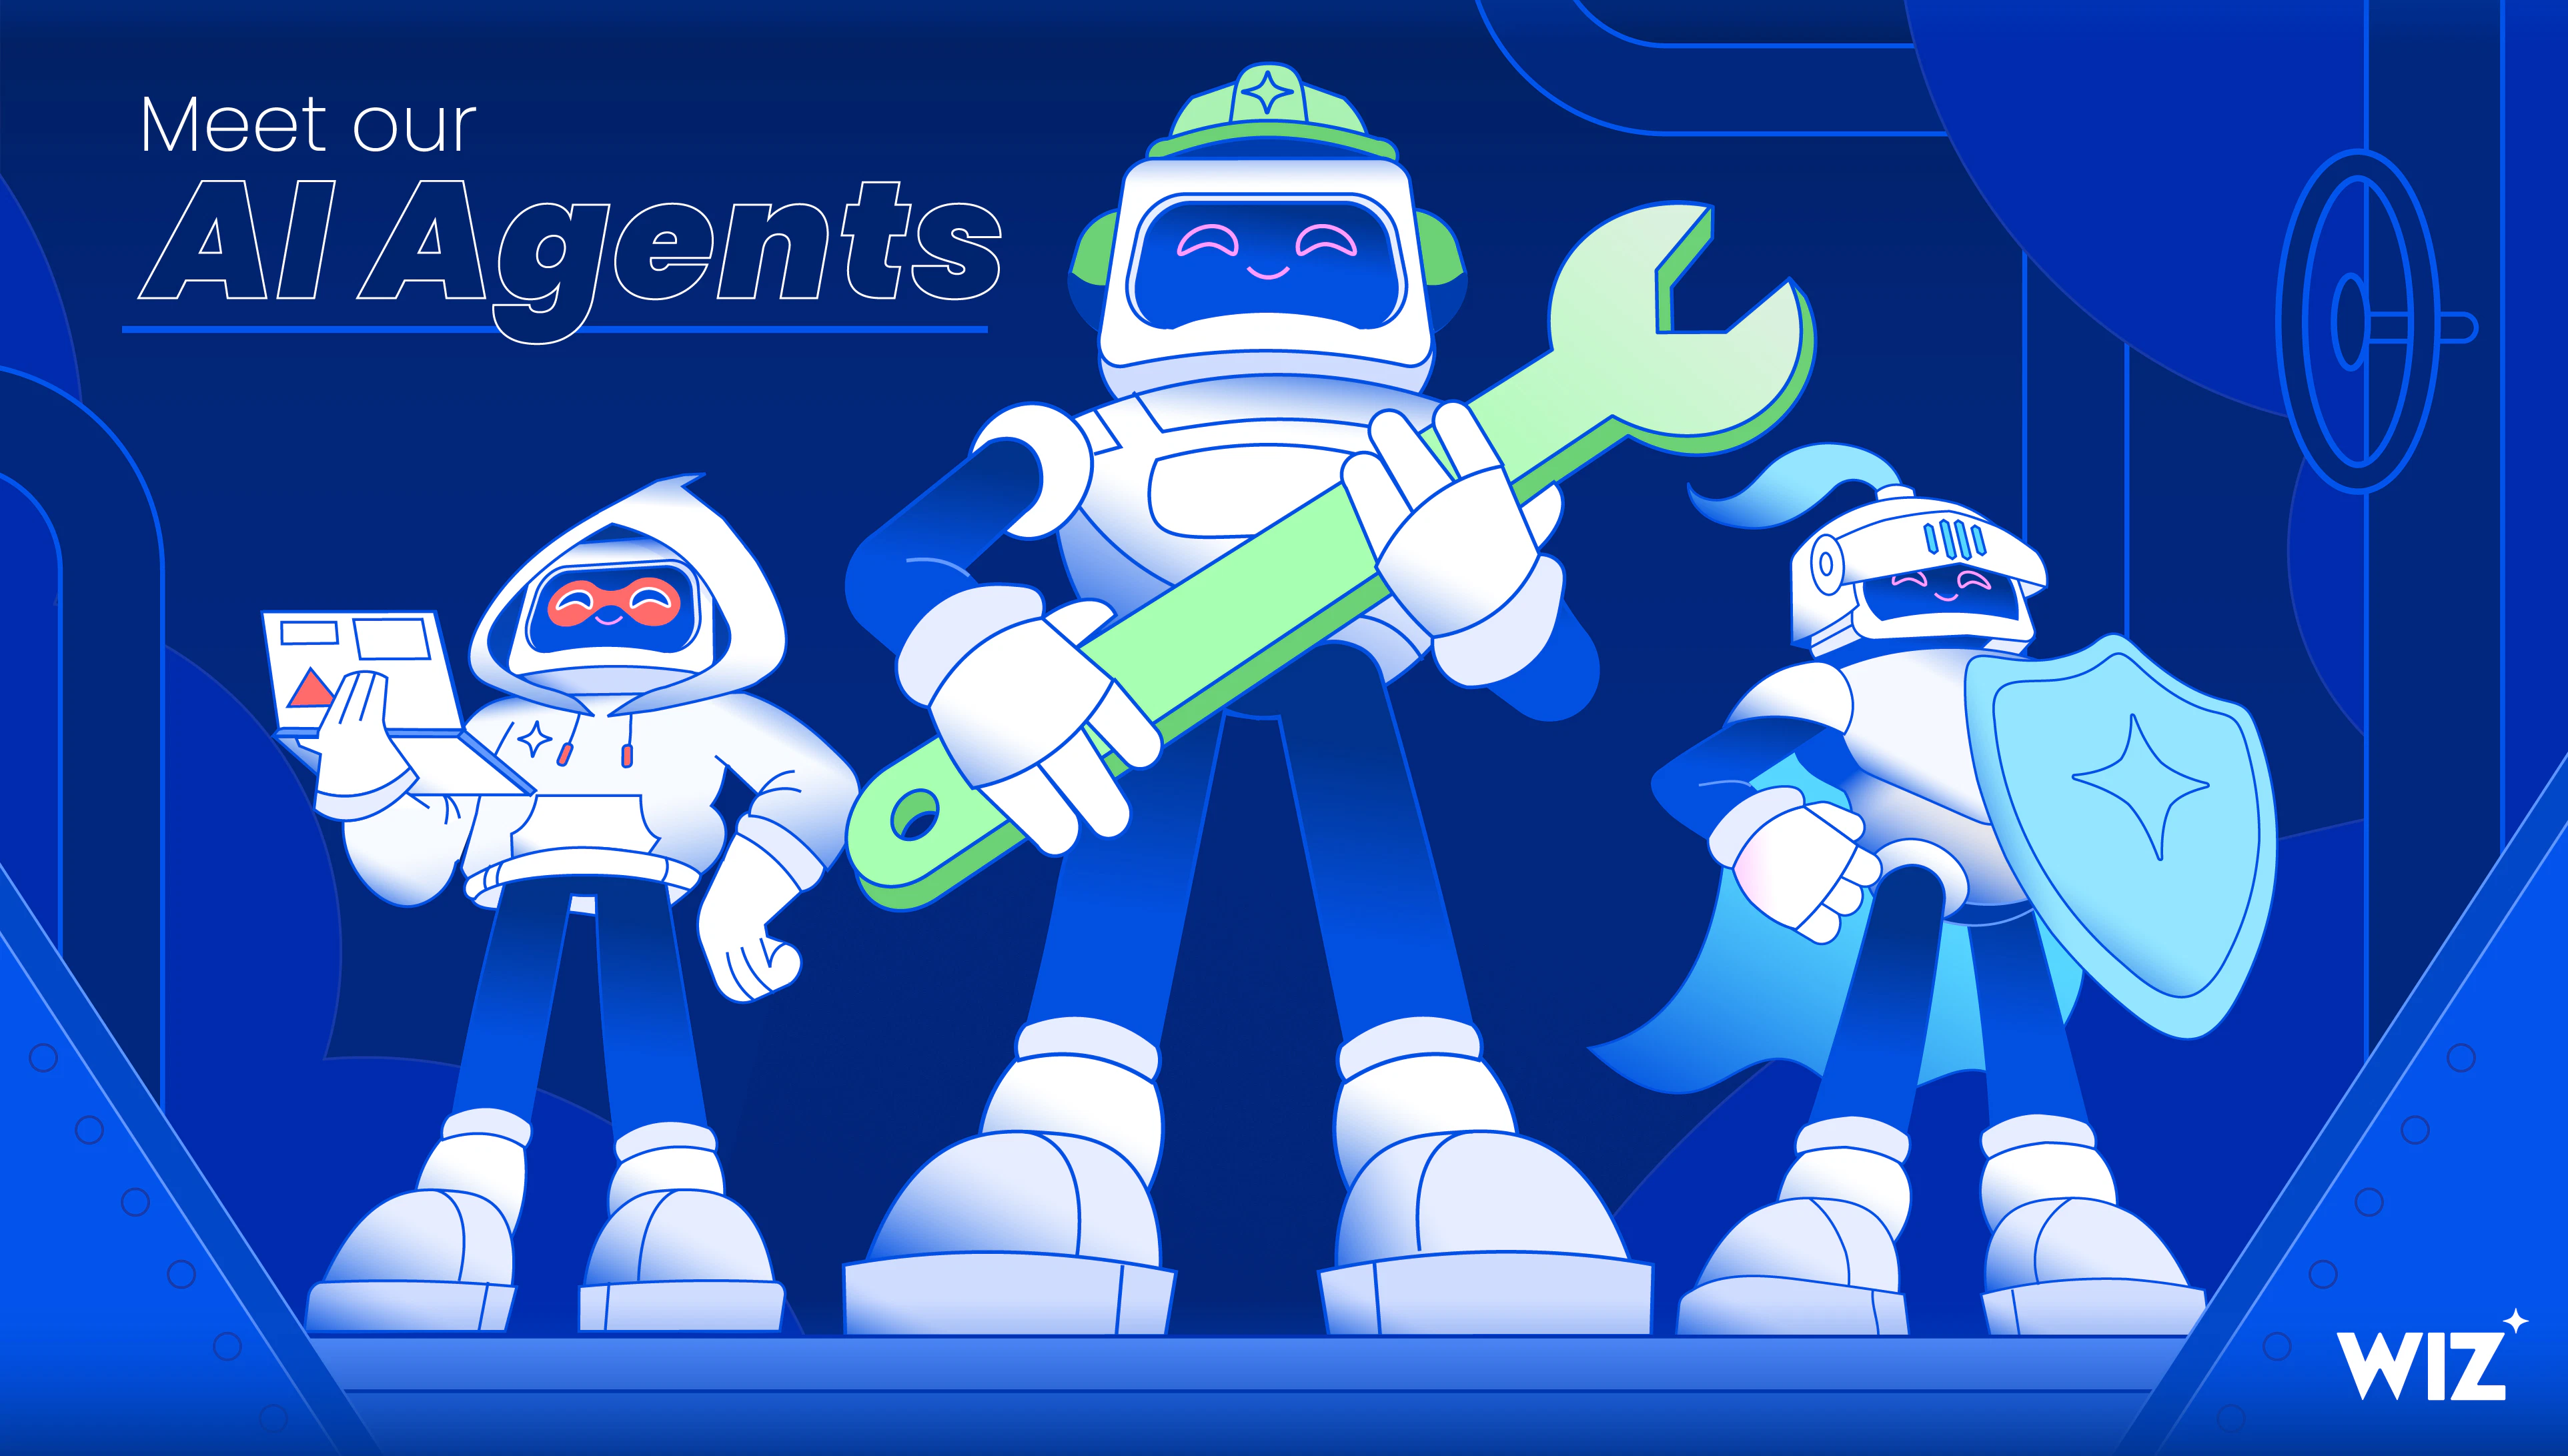
El multiplicador de fuerza de tu equipo: agentes de IA especializados que trabajan juntos para eliminar el trabajo manual y acelerar cada fase del ciclo de vida de la seguridad.
Bueno, bueno… un punto final expuesto. Veamos hasta dónde llega esto.
Simula continuamente rutas de ataque reales a través de tu nube y pila de IA para demostrar qué es realmente explotable, eliminando ruidos teóricos y poniendo a la luz los riesgos que realmente importan.
Modo detective activado… Veamos qué pasó realmente.
Investiga de forma autónoma las alertas en la nube y el código, correlaciona las pruebas de principio a fin y ofrece un veredicto claro y defendible con radio de máxima potencia.
Buena atrapada. Vamos a eliminar este crítico.
Cubre la brecha entre encontrar y corregir generando remediación consciente del contexto en la fuente, impulsando a los equipos hacia un riesgo crítico cero.
Visita guiada
Haz la visita guiada interactiva a continuación
Mika incorpora la inteligencia del Wiz Graph y agentes especializados a tus herramientas diarias, para que puedas tomar decisiones informadas sin salir nunca de tu flujo de trabajo.

La Puerta de Enlace a la Automatización Personalizada - El servidor Wiz MCP te permite conectar el Security Graph directamente a tus agentes personalizados, bases de conocimiento internas y IDEs de desarrolladores. Crea flujos de trabajo personalizados que combinen la inteligencia de Wiz con los datos únicos de tu negocio para automatizar la seguridad en cualquier lugar donde trabajes.

Red Agent finds what humans miss. It caught critical authorization flaws across services where traditional testing and our bug bounty program came up short. We had continuous AI-powered attack surface testing on our roadmap. Wiz got there first, and did it better than we would have.

We are now fully relying on the Blue Agent for some of the low severity alerts. Instead of having a lot of tickets, it's just one task at the end of each shift — checking all those detections that have been closed by the Blue Agent. That is allowing our team to focus more on the advanced work.

The Green Agent creates a Jira ticket with the full description, attack path analysis, and remediation steps already populated. Developers have everything they need to act immediately.

What is most amazing about Red Agent is the way that we can track and get alerting or visibility on endpoints that can be attacked or manipulated from the outside. It tells me: 'You have an endpoint here, you are missing authentication,you have an exposure.' All of those insights are really, really helping me to close gaps fast.

My favorite thing about the Blue Agent is how quickly it helps us understand why an alert happened and what it actually means in our environment.

At first we continued our manual investigation side by side with the agents, but 10 out of 10 times we were getting the same threat assessment conclusions, building this trust enabled us to rapidly accelerate.

AI workflows with Wiz MCP connectivity ensure our minimum level of triage is the same high standard our systems maintain consistently.
Diseña tus propios manuales de seguridad: Dirige a Mika y a tus agentes especializados con un lienzo visual y sin código. Encadena acciones en secuencias automatizadas personalizadas—desde triaje instantáneo hasta remediación a gran escala—adaptadas a la lógica de respuesta única de tu organización.