Today’s mission environments are operating under a rapidly increasing operational tempo. Security teams face a shrinking mean-time-to-exploit (MTTE) as threat actors leverage artificial intelligence to automate and scale their campaigns. Concurrently, agencies are deploying AI to accelerate and drive mission outcomes. This dual imperative forces security teams to simultaneously adapt to an AI-augmented threat landscape and verify that internal AI workloads are securely architected.
To outpace modern adversaries and secure mission AI adoption, organizations cannot depend on human speed alone. They need an approach that enables risk remediation at machine speed, while maintaining the strict security requirements for protecting public sector environments.
From CNAPP to AI-APP
For many, the Cloud-Native Application Protection Platform (CNAPP) has become the foundational standard for achieving continuous visibility and risk assessment across multi-cloud and connected hybrid environments. CNAPPs analyze infrastructure, identity, and applications with connected context. However, AI continues to transform how risk emerges and the speed at which teams must identify and remediate those risks.
This is why Wiz transformed CNAPP through AI-accelerated insights driven by the Wiz AI Agents. These agents enhance insights from signals across development, infrastructure, and live runtime behavior to elevate CNAPP into an AI-Application Protection Platform (AI-APP).
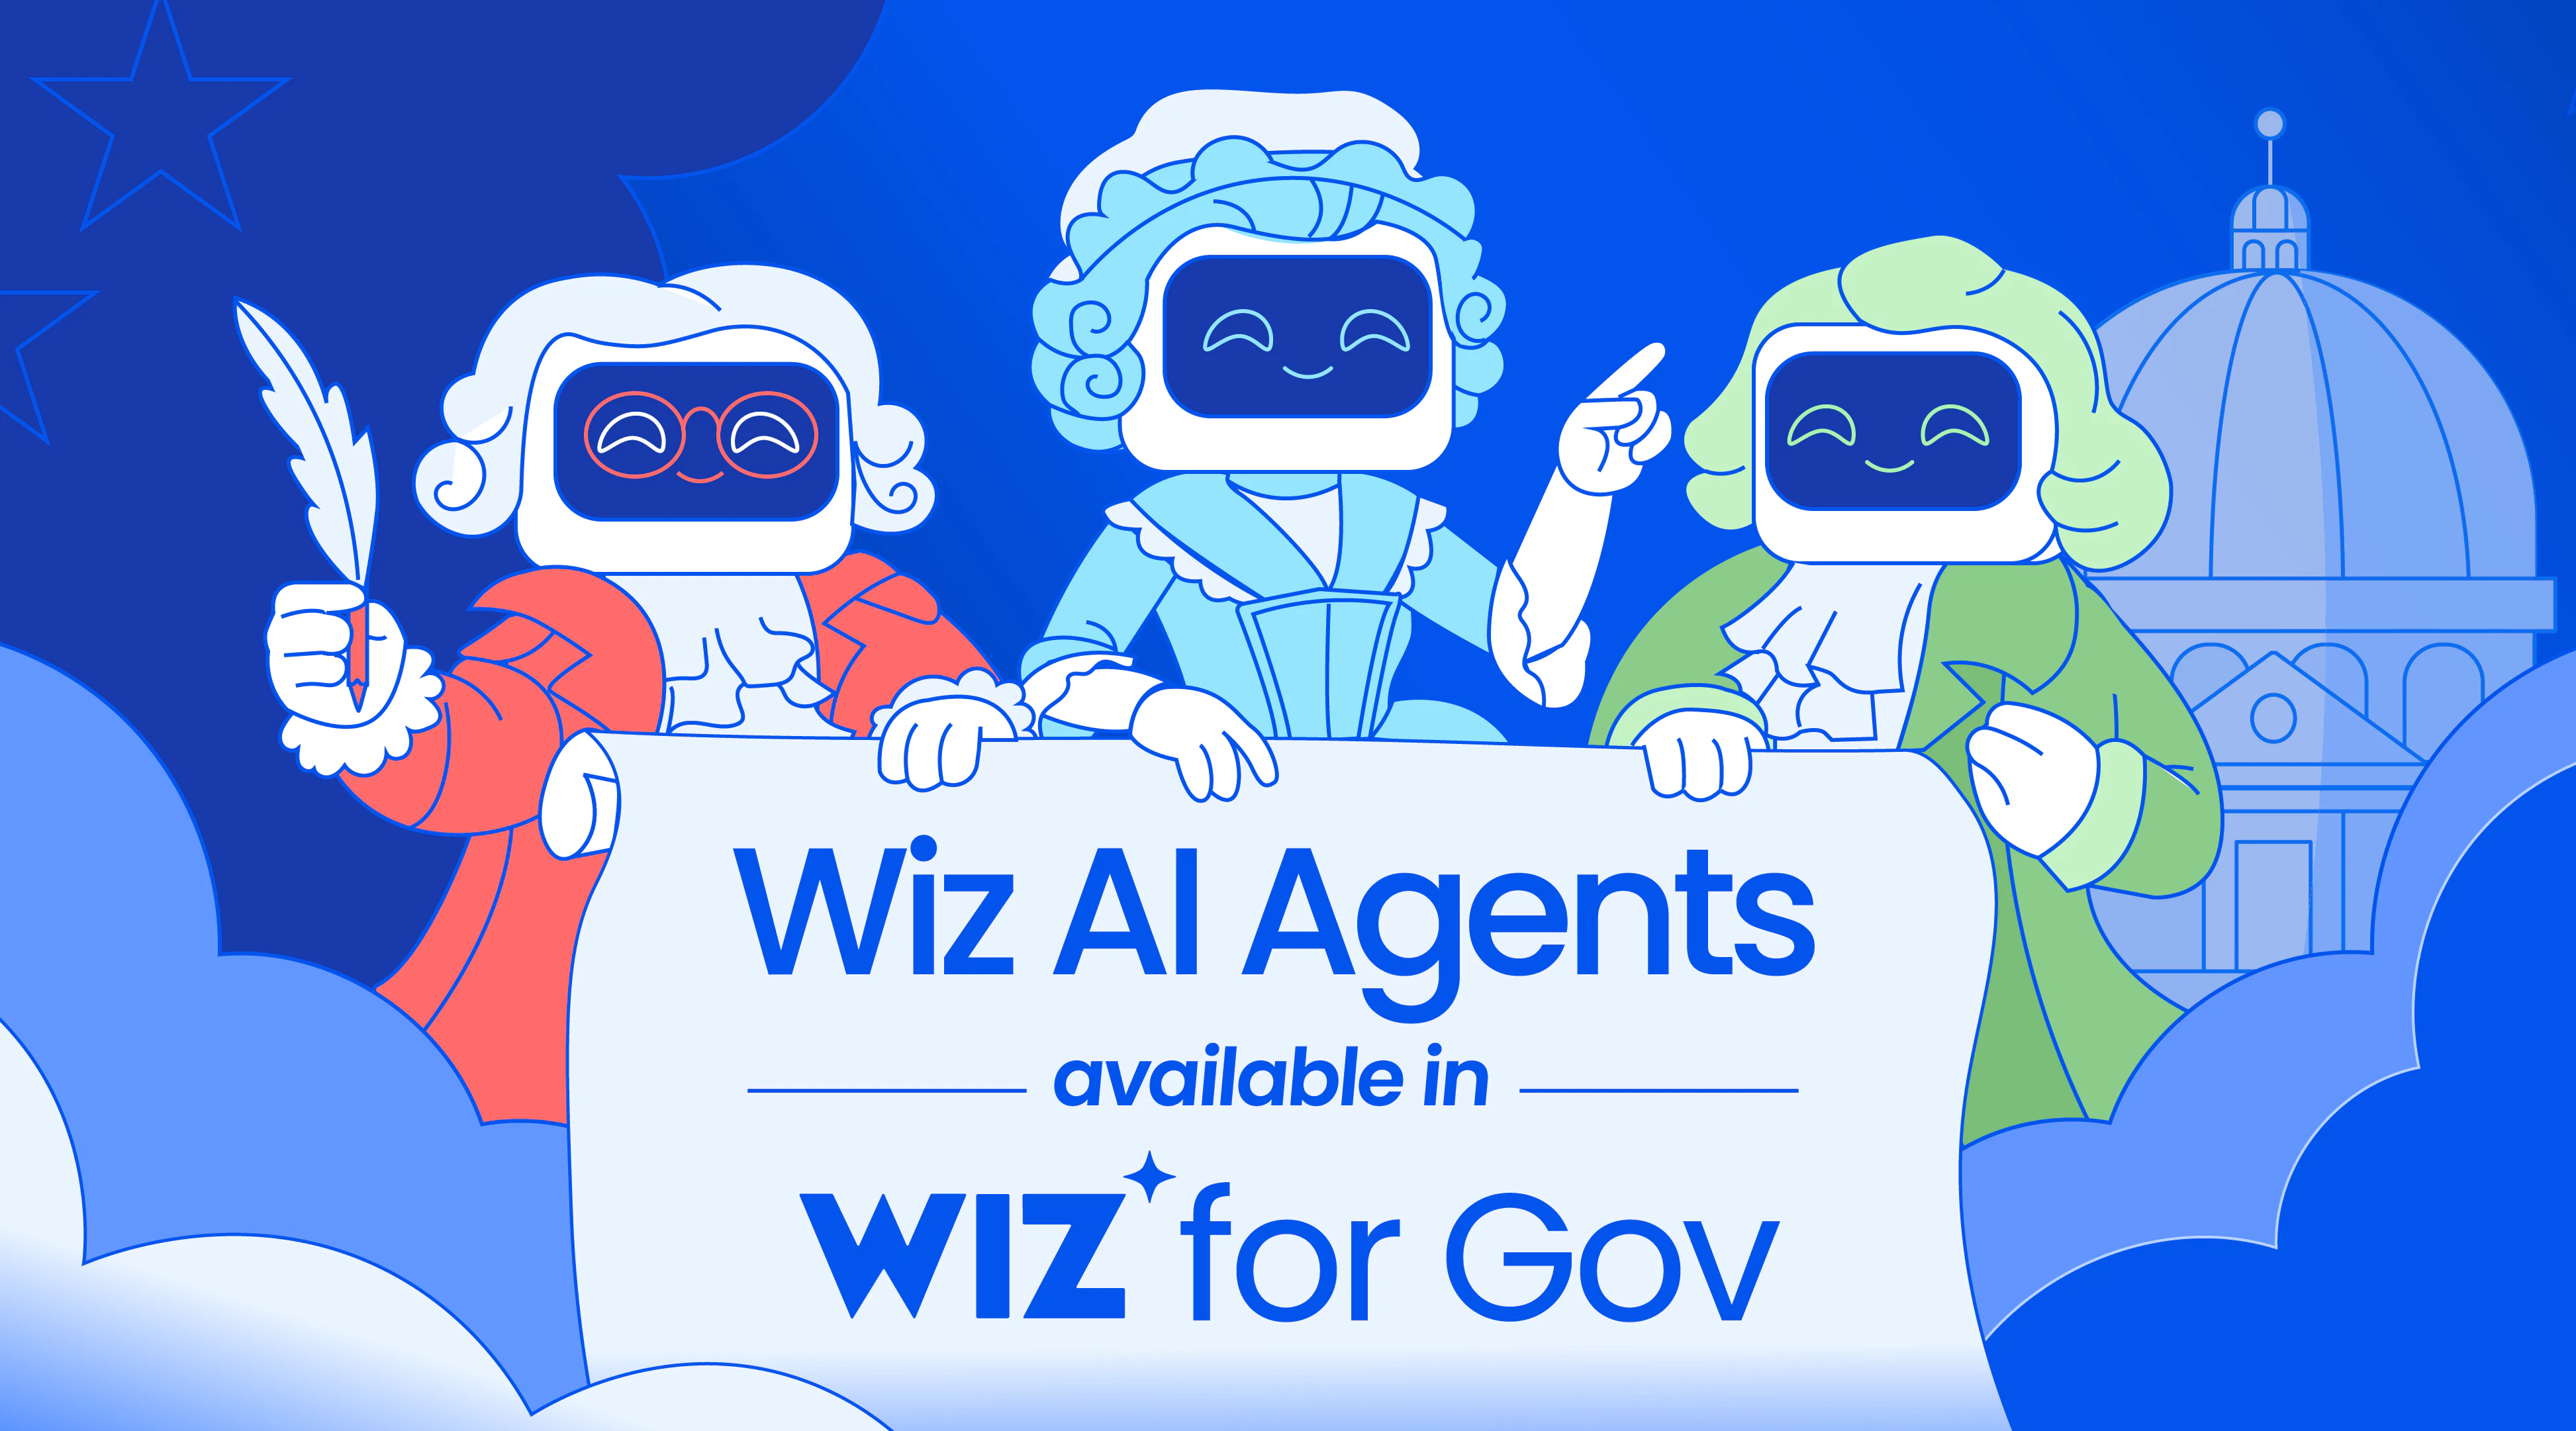
Today, we are excited to announce that the Wiz AI Agents are available within Wiz’s FedRAMP High authorized environment, Wiz for U.S. Government (Wiz for Gov). This makes Wiz for Gov the first AI-APP available for U.S. public sector organizations to protect systems managing highly sensitive, national security and mission-critical data.
This latest announcement signals our ongoing commitment to serving public sector entities, and it is especially meaningful that it comes on the heels of our Scan for Good initiative. Scan for Good is a program that is specifically geared towards supporting under-resourced organizations that play a vital role in the communities they serve, from non-profits to critical infrastructure.
At the core of Wiz for Gov remains the Wiz Security Graph and our agentless CNAPP architecture, which provides deep, ground-truth data and context for cloud and connected on-premises environments. This foundational context ensures that Wiz AI Agents act as a force multiplier for human operators, providing AI-enhanced insights and guided remediation, without relying on predictive risk modeling which can lead to false positives and/or negatives.
Introducing Wiz AI Agents in Wiz for Gov
To execute this unified risk model, Wiz AI Agents translate ground-truth Security Graph context into actionable, machine-speed operations across the application lifecycle.
Wiz AI Agents provide configurable operational boundaries, allowing security teams, for specific workflows, to authorize agents to execute routine remediations autonomously or require human-in-the-loop approval before applying changes on sensitive systems. This flexibility ensures operators maintain complete command and control over mission workloads.
Wiz Green Agent: The Wiz Green Agent delivers actionable remediation plans directly into developer workflows. It provides a transparent Investigation Summary detailing the root cause and generates ready-to-merge Pull Requests to resolve issues at the source.
Wiz Blue Agent: The Wiz Blue Agent provides automated investigation and response for security operations teams. For threats that fire in Wiz Defend, the Blue Agent immediately starts triaging, providing a comprehensive investigation summary and verdict on threat severity.
Wiz Red Agent: The Wiz Red Agent focuses on continuous runtime risk assessment. It will continuously analyze live production environments to map multi-step attack paths, prioritizing exploitable risks so defenders can remediate toxic combinations before threat actors exploit them.
Connecting Dev, Prod, and SOC: A Unified Risk Model
Traditional risk management and compliance models often divide security into isolated checkpoints across separate domains: pre-deployment scanning in development, continuous monitoring in production, and event triage within the SOC. In the modern cloud and AI era, treating these functions as disconnected silos slows down response times and leaves critical blind spots.
By linking development, production, and SOC operations through a single source of ground-truth data, an AI-APP enables federal security teams to transition from point-in-time compliance to continuous, lifecycle-wide risk management.

Delivering Mission Outcomes at Scale
By integrating Wiz AI Agents into Wiz for Gov, federal agencies and public sector organizations can move beyond siloed security tools to enhance and accelerate operational outcomes across five critical domains:
Continuous Authorization and Risk Posture Alignment: Traditional point-in-time compliance checks struggle to keep pace with dynamic cloud environments. By providing continuous visibility enhanced by AI analysis, Wiz for Gov simplifies evidence collection and risk posture tracking, supporting Continuous Authorization to Operate (cATO) initiatives and Continuous Monitoring (ConMon) objectives without increasing administrative burden. This accelerates time-to-deployment for new systems, helping to accelerate innovation and modernization.
Secure AI Workload Enablement and Shadow AI Discovery: As agencies rapidly deploy generative AI, LLMs, and custom machine learning pipelines to advance mission capabilities, security teams must maintain full visibility over these specialized architectures. Wiz AI-APP automatically discovers AI workloads, model repositories, and data pipelines across hybrid environments. This makes it easier to enforce baseline security controls from initial code to production, and quickly identify new introductions of AI workloads within organizational environments.
Accelerated SDLC without Security Bottlenecks: Green Agent helps embed secure-by-design guardrails directly into developer pipelines and Infrastructure-as-Code (IaC) templates. By delivering contextual fix recommendations, engineering teams can deploy mission applications rapidly while preventing security misconfigurations from ever reaching live production environments. This helps decrease the number of issues that appear on Plan of Action and Milestones (POA&M) reports, as well as help accelerate time-to-deployment for new code and resources.
Precision Remediation: Isolated CVE findings, lacking broader system context, frequently create vulnerability backlogs for security teams without a clear means for prioritized remediation. By leveraging the Wiz Security Graph, Wiz AI Agents evaluate true toxic combinations, identifying how vulnerabilities, exposed identities, misconfigurations, and sensitive data intersect to understand the potential for impact against likelihood of occurrence. This helps support defenders to focus remediation efforts on the small percentage of attack paths that represent an immediate threat to mission systems first, while still having the broader system visibility needed to meet directives such as CISA’s BOD 26-04.

SOC Operational Efficiency via Code-to-Cloud Traceability:. When security incidents occur, analysts shouldn’t lose critical hours piecing together logs across siloed tools. The Wiz Blue Agent takes on the heavy lifting of initial threat triage. By evaluating environment telemetry and assessing root causes, Blue automatically generates a clear, defensible verdict on threat severity. Security operations teams can then review the evidence, validate the findings, and remediate the threat—saving valuable time and keeping human defenders focused on what matters most. This accelerated insight and root cause analysis helps to greatly reduce mean-time-to-acknowledge (MTTA) and mean-time-to-respond (MTTR).
As public sector cloud adoption accelerates and threat actors leverage automation to shrink exploit windows, security operators must match that tempo with tools built for machine speed. By embedding Wiz AI Agents into Wiz for Gov, defenders can maintain continuous, lifecycle-wide security across every mission workload.
See Wiz in Action
Ready to see how the Wiz AI Agents can help your agency meet today’s security demands at machine speed? Get a demo today.