
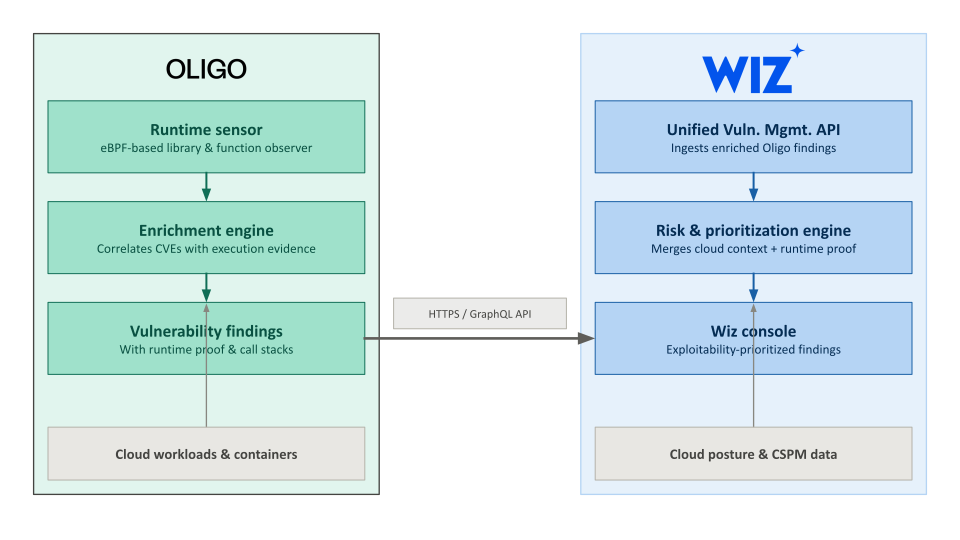

Integration overview
The Wiz and Oligo integration enhances cloud risk prioritization with deterministic runtime proof. Wiz ingests vulnerabilities found by Oligo with enriched real-time execution telemetry that shows which vulnerable libraries and functions are actually loaded and invoked in production. This allows security teams to focus on exploitable risk, reduce vulnerability backlogs by 90 percent or more, and accelerate remediation without slowing developers or disrupting the business.
Market Challenge
Cloud and application security tools generate thousands of vulnerability findings, but often lack visibility into what is actually running in production. Without runtime telemetry, teams rely on CVSS scores and reachability estimates to prioritize risk. This results in developer friction, long triage cycles, growing backlogs, and increased risk exposure.
Key Benefits of the Integration
Deterministic exploitability validation
Prove whether a vulnerable library is loaded and whether the specific function introducing the vulnerability is executed in production.
Risk-based prioritization inside Wiz
Enrich Wiz findings with runtime context so teams can focus on vulnerabilities that present real business risk.
Reduce vulnerability backlogs by 90 percent or more
Eliminate non-executed findings and dramatically decrease remediation workload.
Faster triage across teams
Provide shared runtime evidence and call stacks for Product Security and Developer teams to align on what matters most.
Developer trust and adoption
Replace theoretical alerts with proof-based findings that developers are confident fixing.
Better Together
Wiz delivers comprehensive cloud and AI visibility across infrastructure, workloads, identities, and configurations. Oligo extends that visibility into the application runtime, where modern attacks most often begin.
Wiz identifies vulnerable assets and risky exposure paths across the cloud and AI environment. Oligo determines which vulnerabilities are truly exploitable by observing real-time library loading and function execution inside running applications.
Together, Wiz and Oligo connect cloud and AI posture with live application behavior. Customers gain full-stack risk context, from environment to executing code and can prioritize based on observed runtime activity.
The result is stronger risk reduction, faster remediation, and better alignment between security and engineering, all without introducing friction into development or cloud operations.

Use case overview
A Wiz customer discovers thousands of vulnerabilities across cloud workloads and containerized applications. Many are rated high or critical based on CVSS scores or reachability analysis. However, security teams lack proof of whether vulnerable components are actually used in production. Triage becomes manual and time-intensive. Developers question whether issues are real, which slows remediation and creates friction between teams.
Solution
With Oligo connected to Wiz, vulnerabilities are enriched with deterministic runtime telemetry. Oligo proves whether a vulnerable library is running and whether the specific vulnerable function is invoked in production. Wiz surfaces this runtime context directly within its risk and prioritization workflows, allowing teams to distinguish exploitable risk from dormant code.
Impact
Security teams quickly reduce noise and eliminate non-executed vulnerabilities from remediation queues. Backlogs shrink by 90 percent or more within days. Developers focus only on vulnerabilities that present real business risk. SOC and Cloud Security teams gain confidence that high-priority findings represent genuine exposure. The organization reduces mean time to remediation, improves cross-team collaboration, and meaningfully lowers breach risk.
cloud security provider?
Become a Wiz Technology Partner

Get a personalized demo
Ready to see Wiz in action?
"Best User Experience I have ever seen, provides full visibility to cloud workloads."
"Wiz provides a single pane of glass to see what is going on in our cloud environments."
"We know that if Wiz identifies something as critical, it actually is."