




- AI
- Wiz Code
- Product & Company News
Introducing Wiz AI SAST: Application Security that Understands Your Code and Your Infrastructure


Salman Ladha, Sharon Ben ZeevOctober 6, 2026
Protect AI generated code from first commit to production with unified security across code, CI/CD, and cloud.

Trusted by more than 65% of Fortune 100 companies




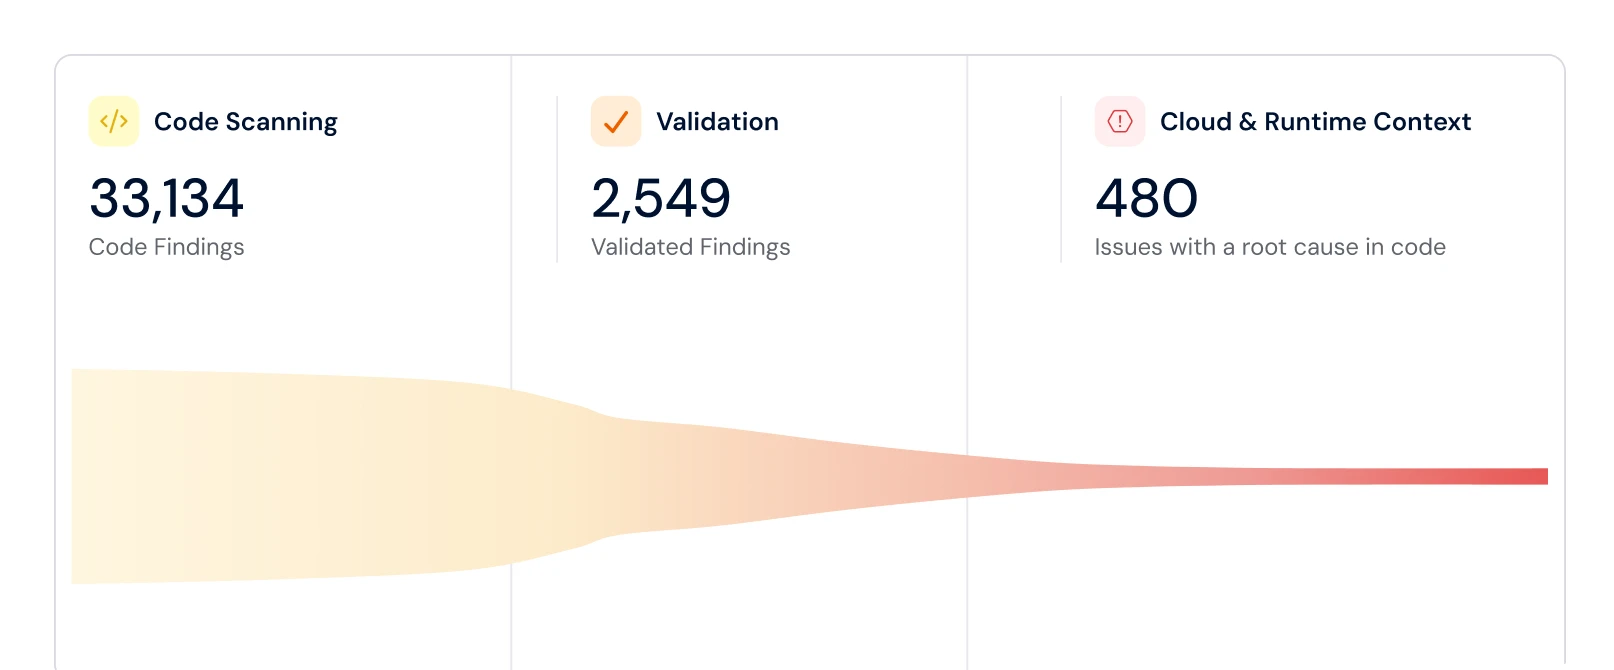
Wiz Code connects code, cloud, runtime, and adversarial validation to identify exploitable attack paths. Developers receive prioritized issues and AI generated fixes, while security teams focus on reducing real risk.
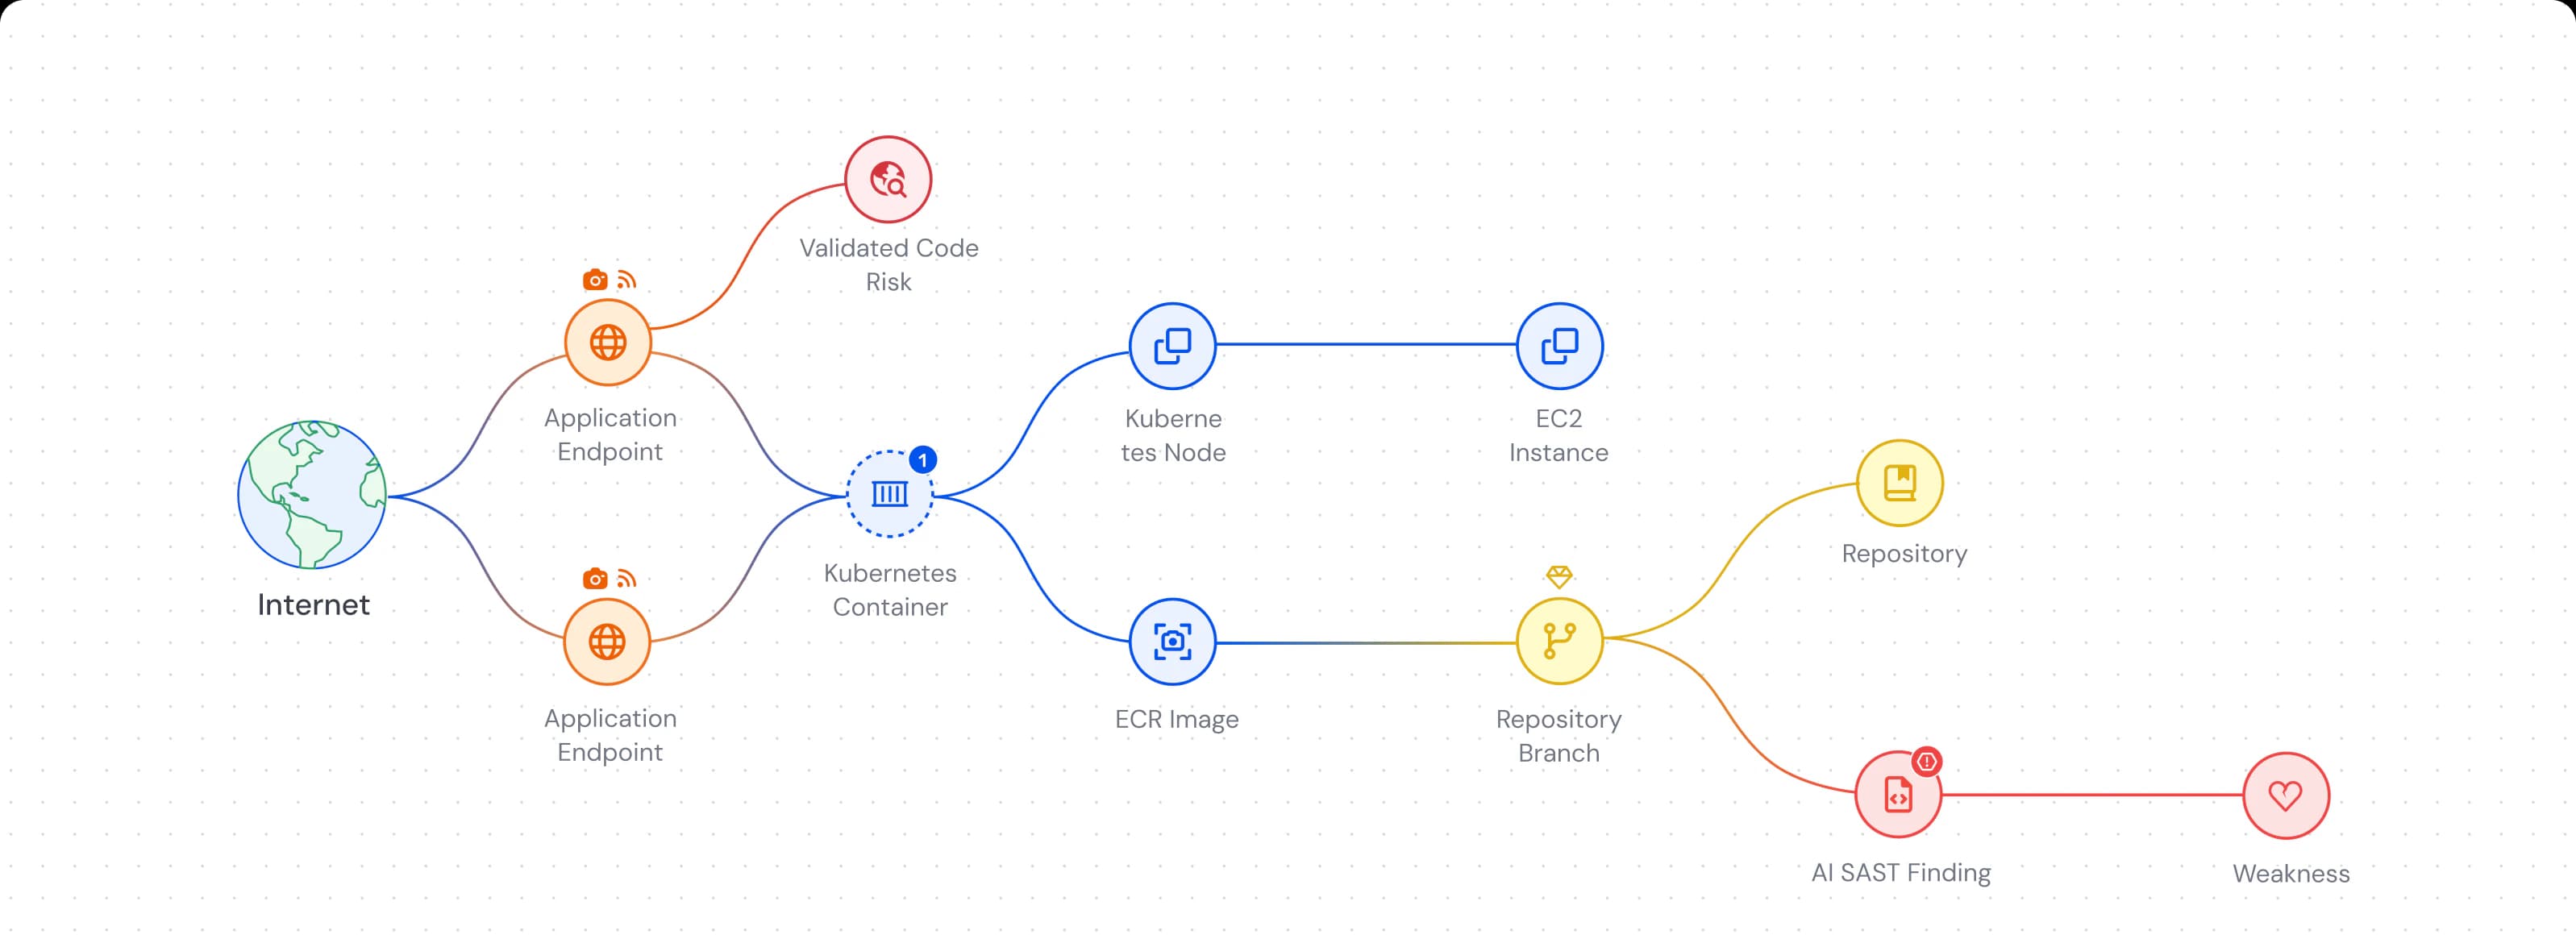
Embed security directly into the tools developers already use. Catch vulnerabilities and AI specific risks early, without slowing development or breaking developer flow.
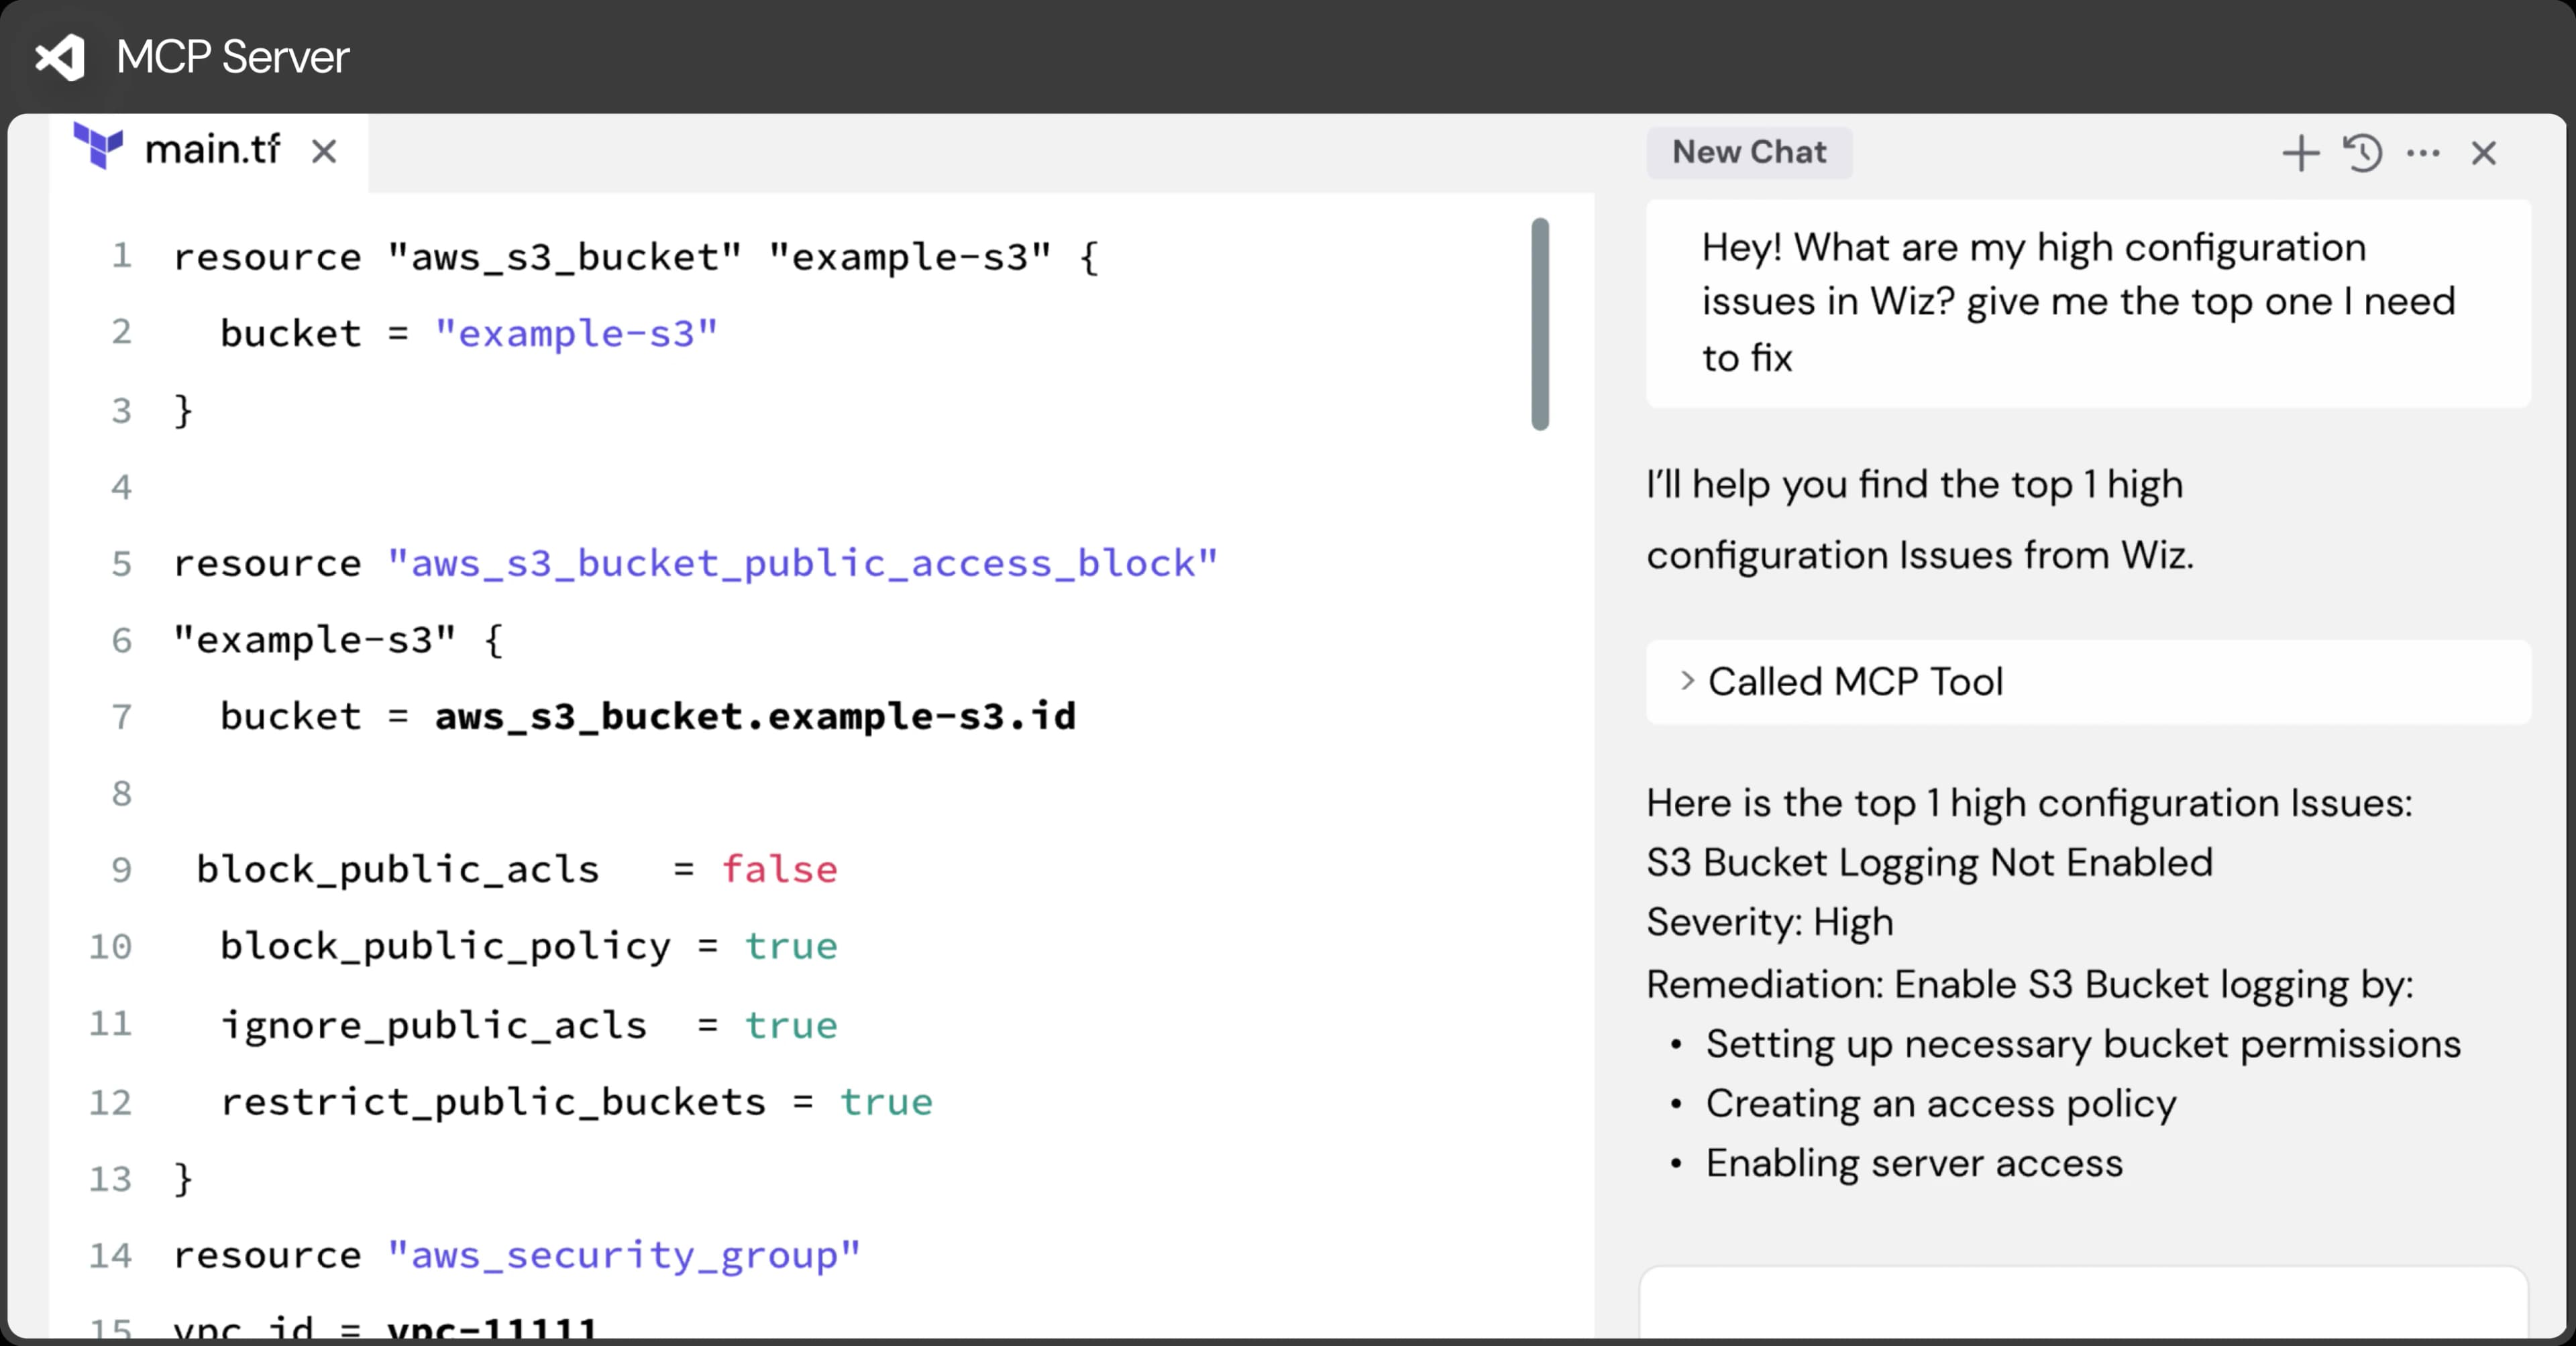
Remove the manual back-and-forth between finding a vulnerability and patching it. Deliver exact code fixes and tailored remediation plans directly to developers so they can secure applications at machine speed.
Consolidate application and cloud security on a single platform with shared context from code to cloud. Eliminate silos, prioritize risk faster, and give security and development teams one view of what matters.


“...the main value of Wiz doesn't come from detection alone, it comes from contextualization. The ability to link exposure, identity, vulnerability, and sensitive data completely changes how you prioritize.”

Nicolas Poulain,
Deputy CTO

“Wiz’s unified platform makes risk visible early in the software lifecycle and actionable for both security and developer teams.”

Yash Mehta,
Senior Security Engineer

“Wiz Code gives our developers real-time feedback in the tools they already use. It means we can prevent vulnerabilities at the source, rather than firefighting after deployment.”

Shane Burnham,
Lead Security Engineer
Take the interactive guided tour below
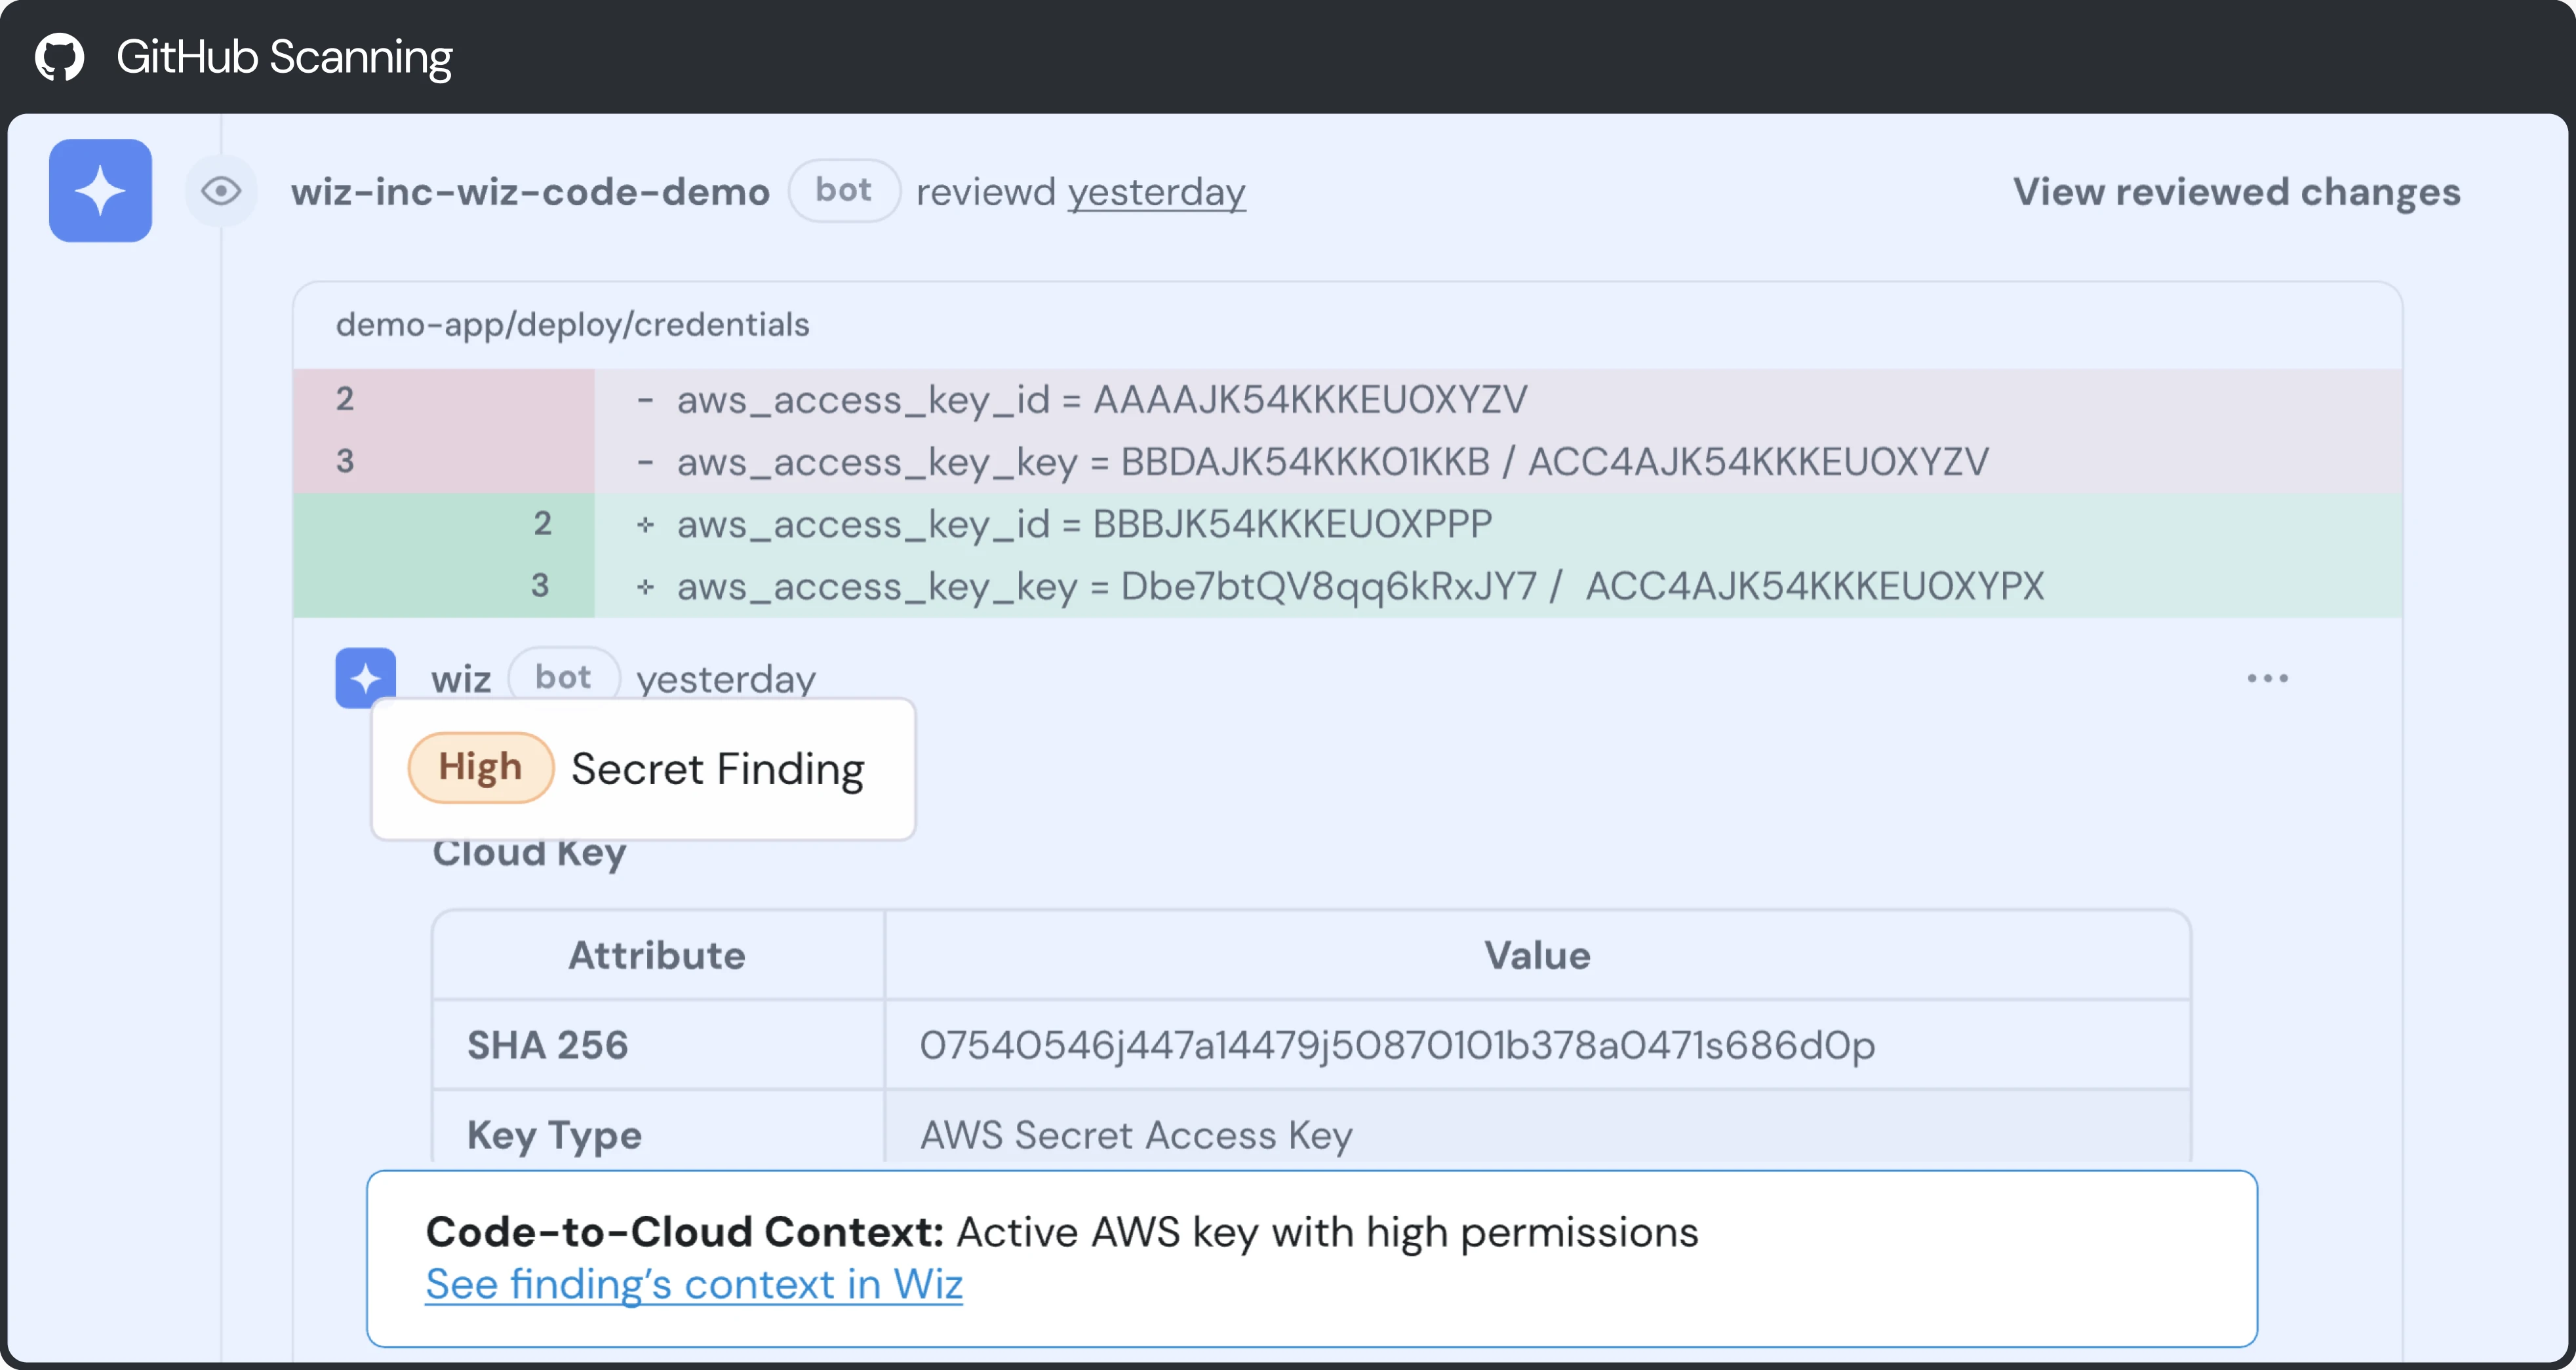
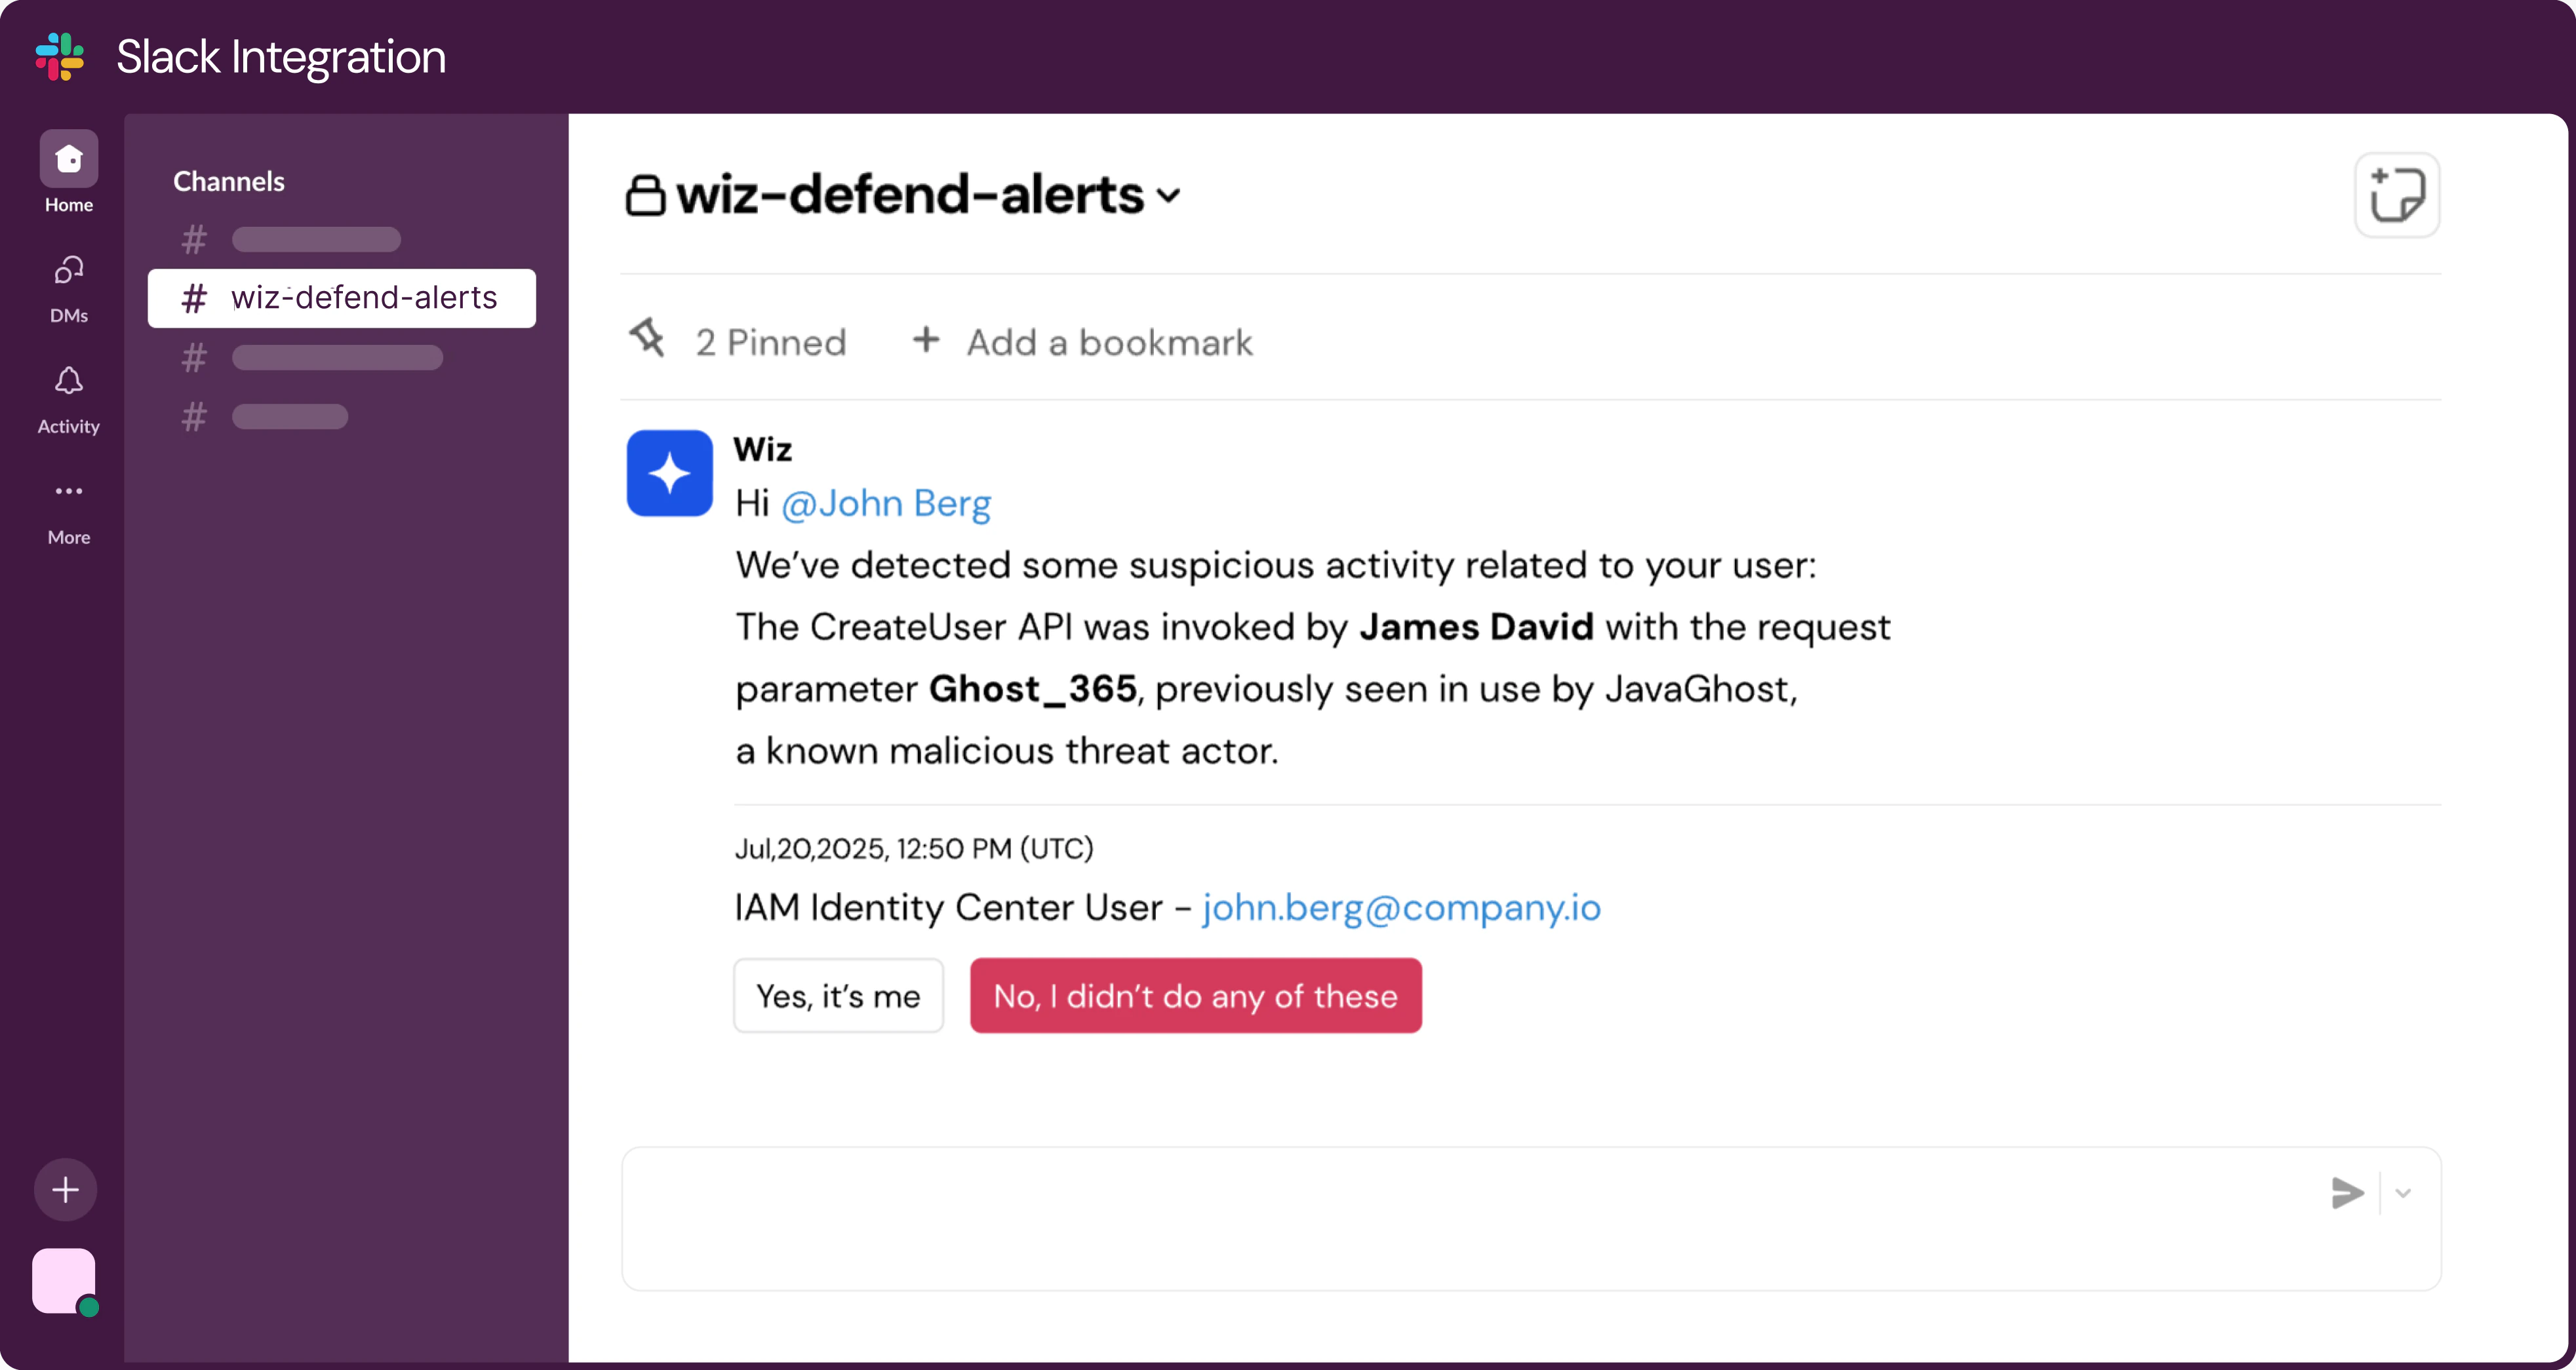
Wiz meets developers in the pull requests, IDEs, and pipelines they already use, surfacing only validated risks with clear ownership and ready-to-merge fixes. Teams remediate real issues in the flow of work, accelerating delivery instead of gating it.
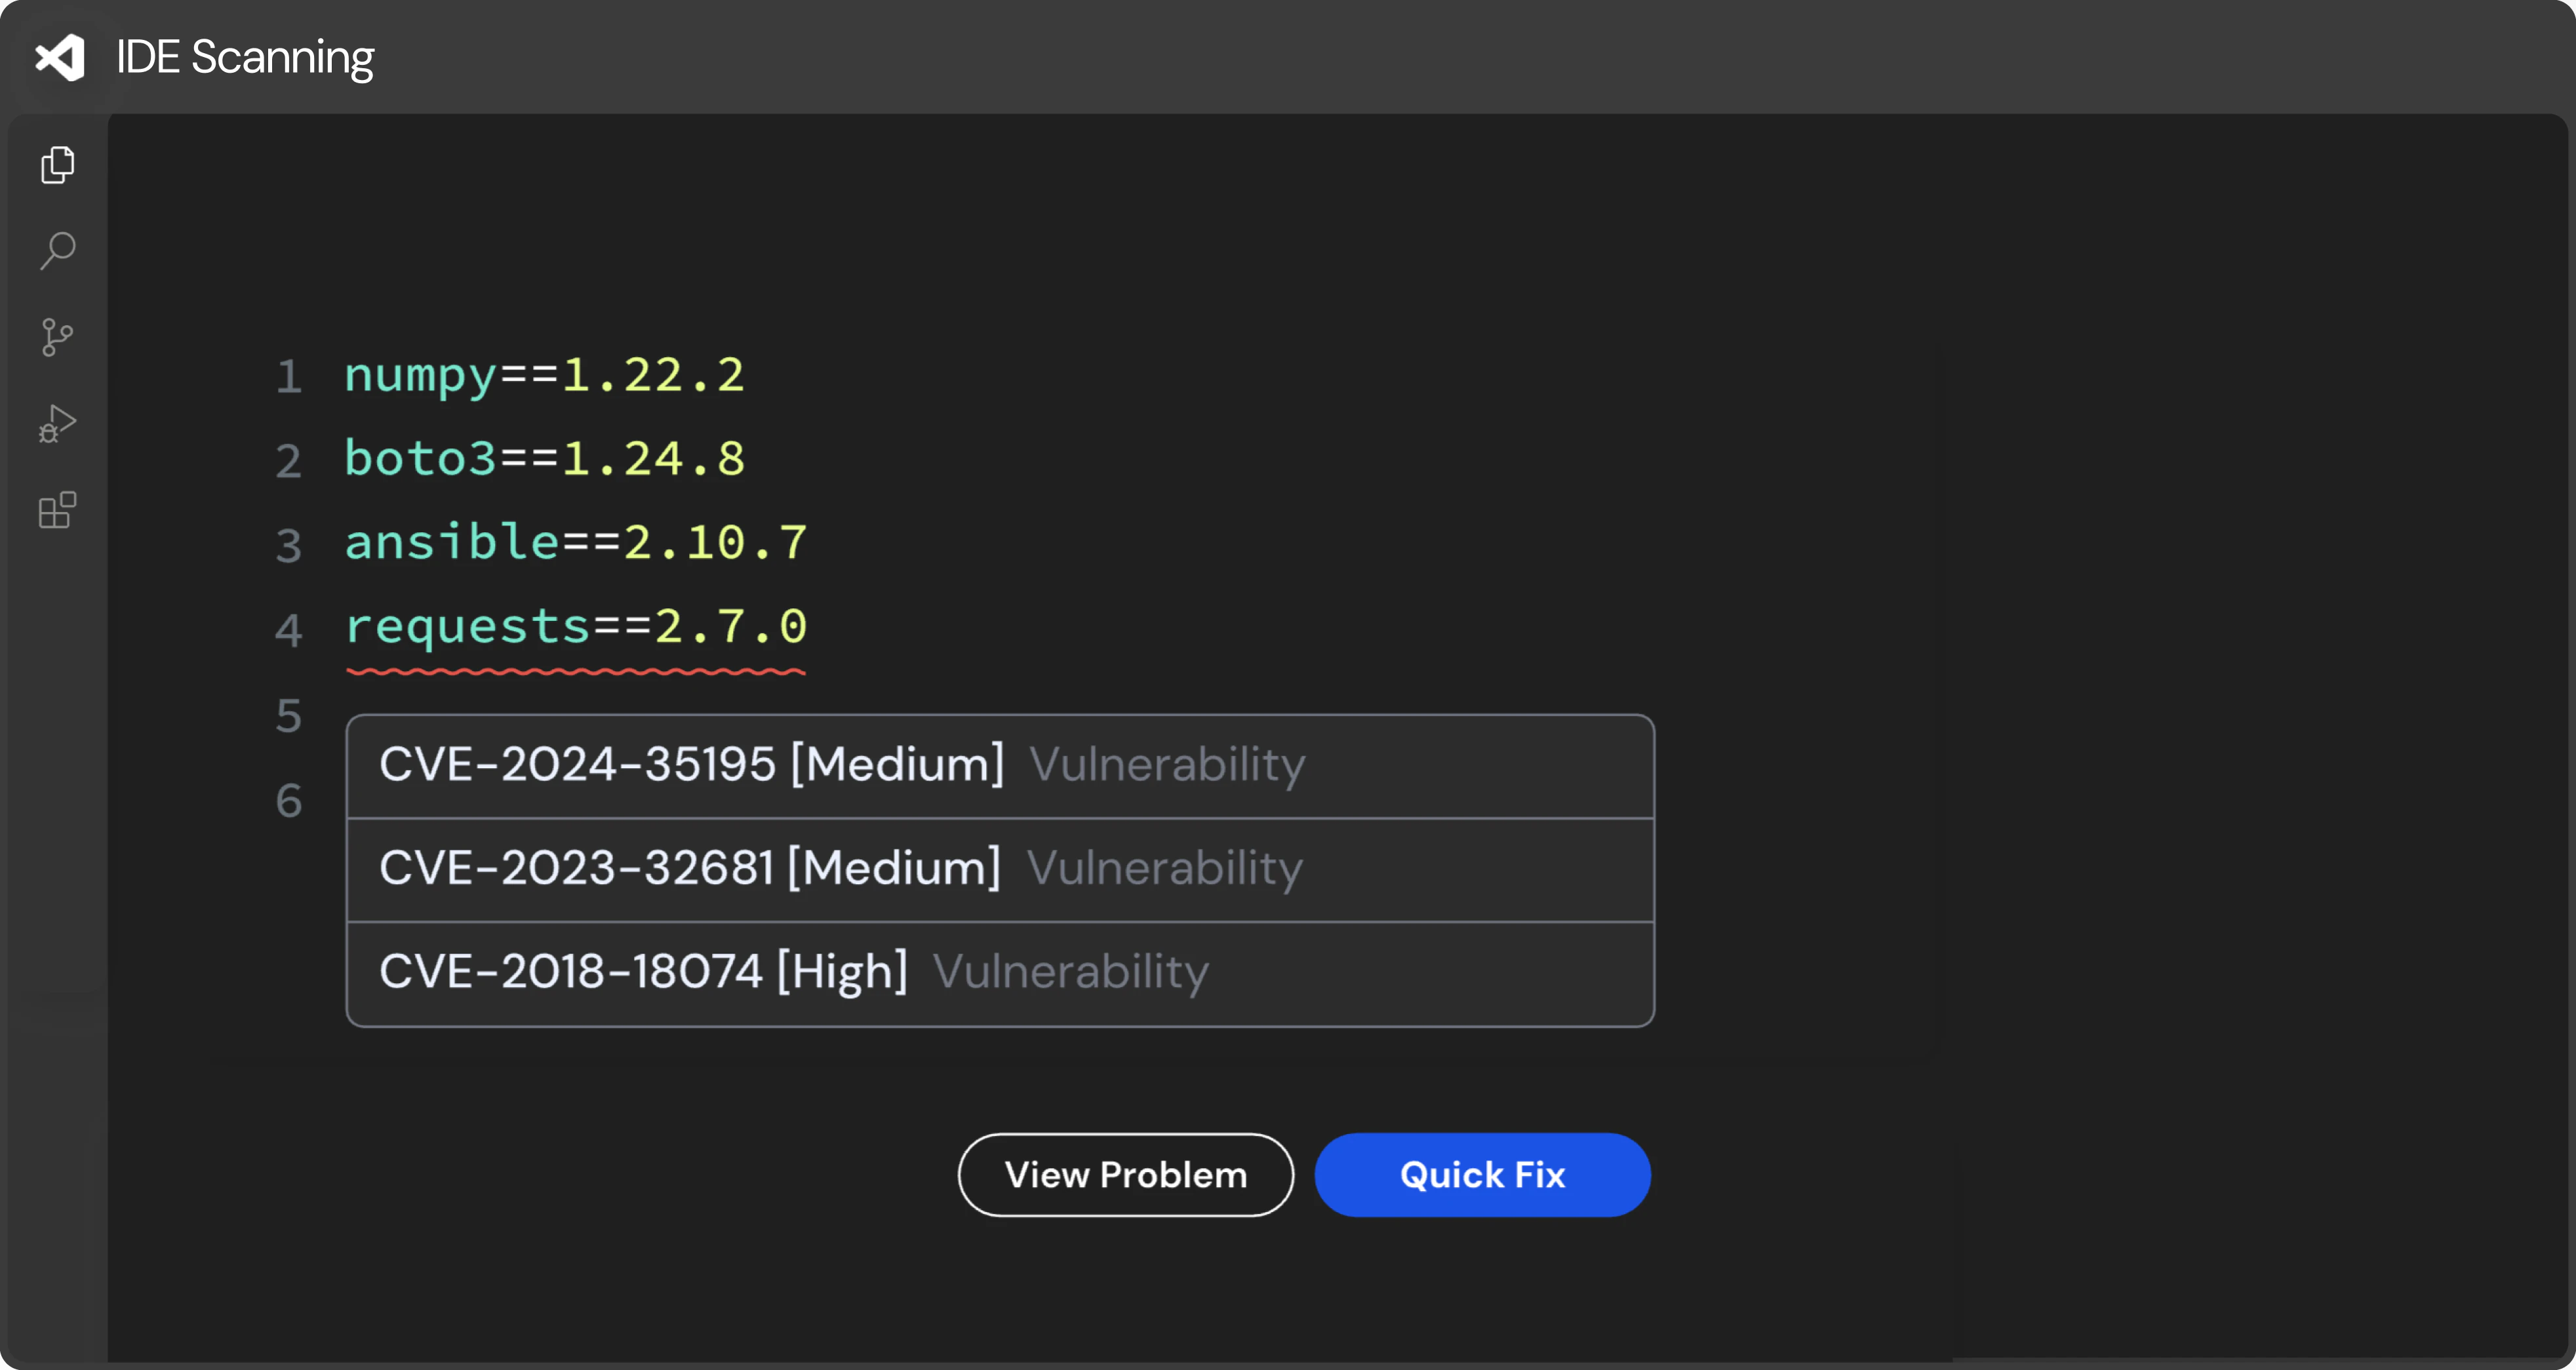


Siloed tools mean less context and prioritization
Find complex business logic flaws and syntax based errors in first party code. Wiz uses rules based engines and agentic reasoning for comprehensive detection coverage across several CWE types.
Learn more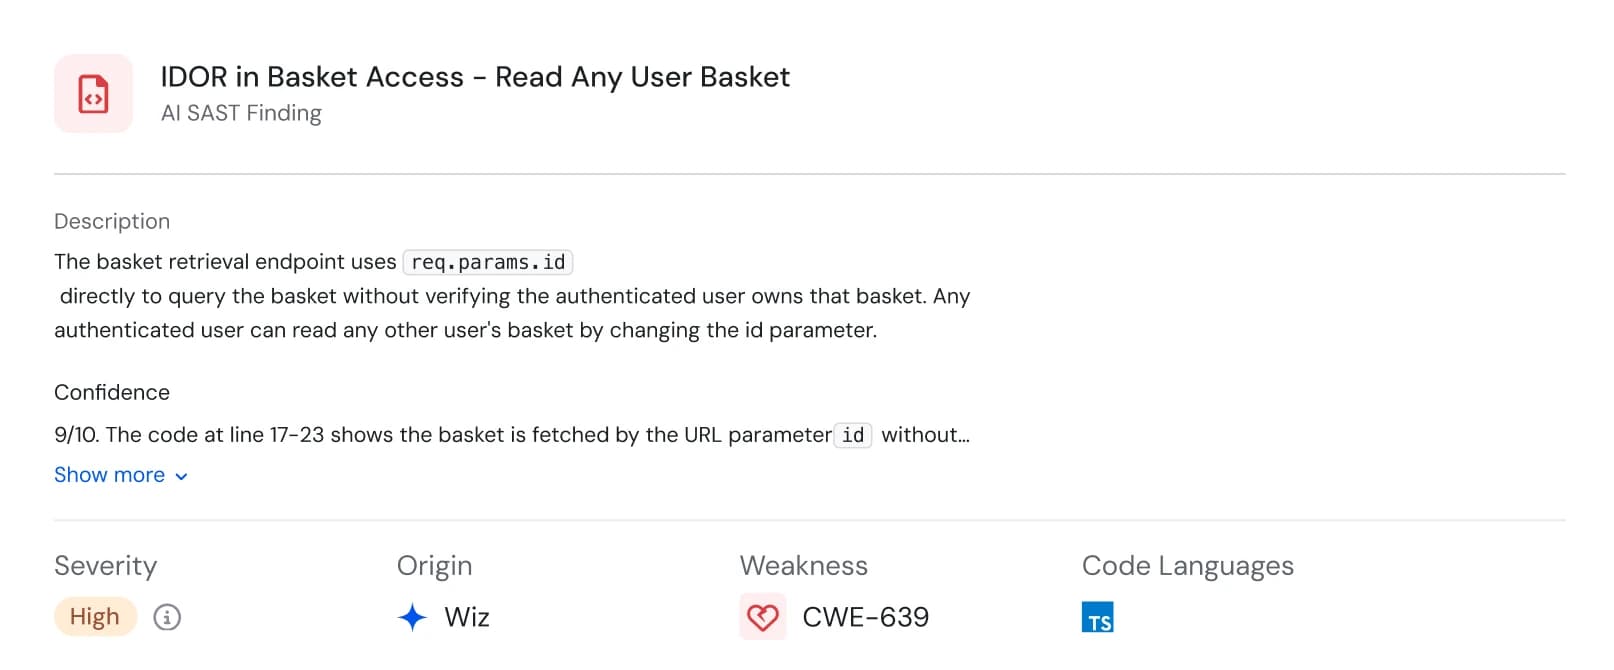
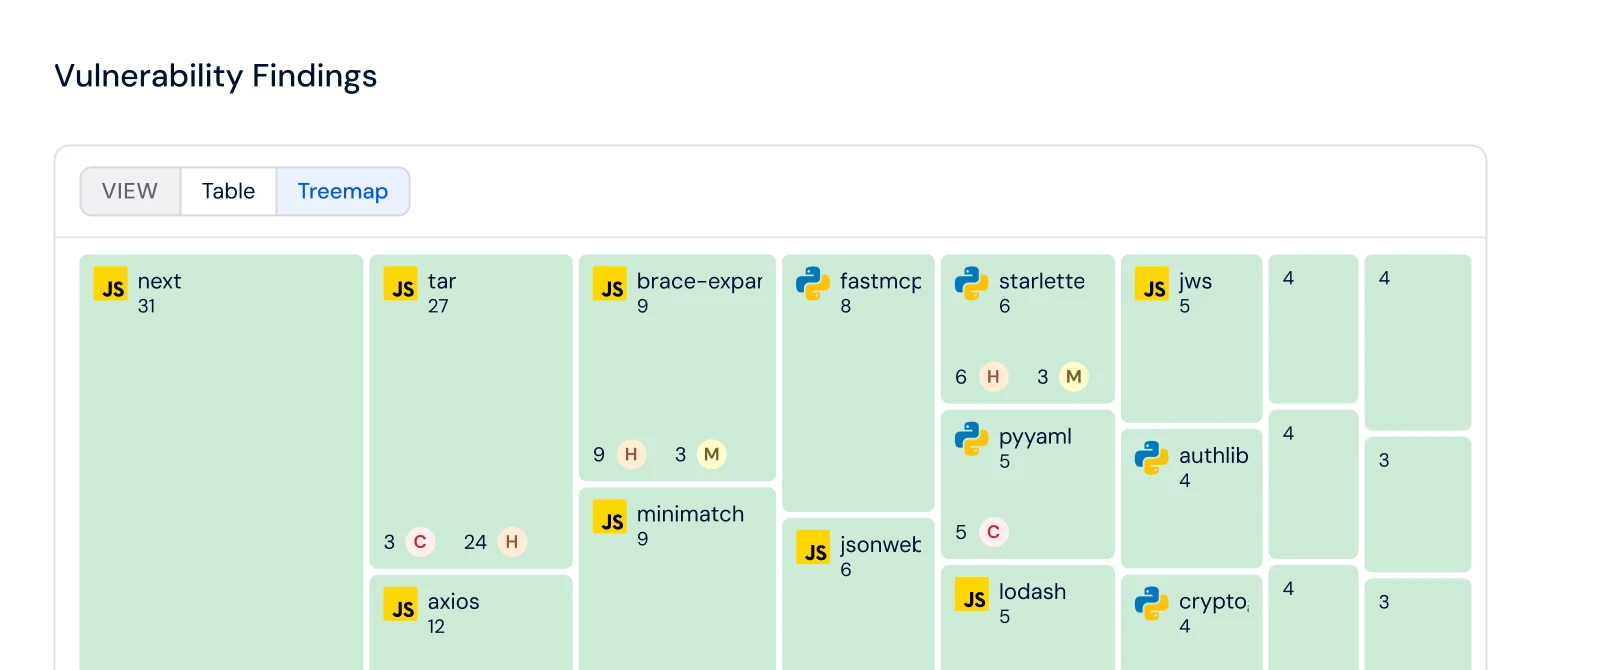
Gain visibility into every software component. Detect vulnerabilities in direct and transitive dependencies and prioritize the reachable ones with runtime context from the Wiz sensor.
Scan IaC for misconfigurations and validate against 1,000+ rules for Terraform, CloudFormation, Azure Resource Manager, Kubernetes, Docker, and more. Detect drift and trace resources from the cloud to your code for precise and effective remediation.
Learn more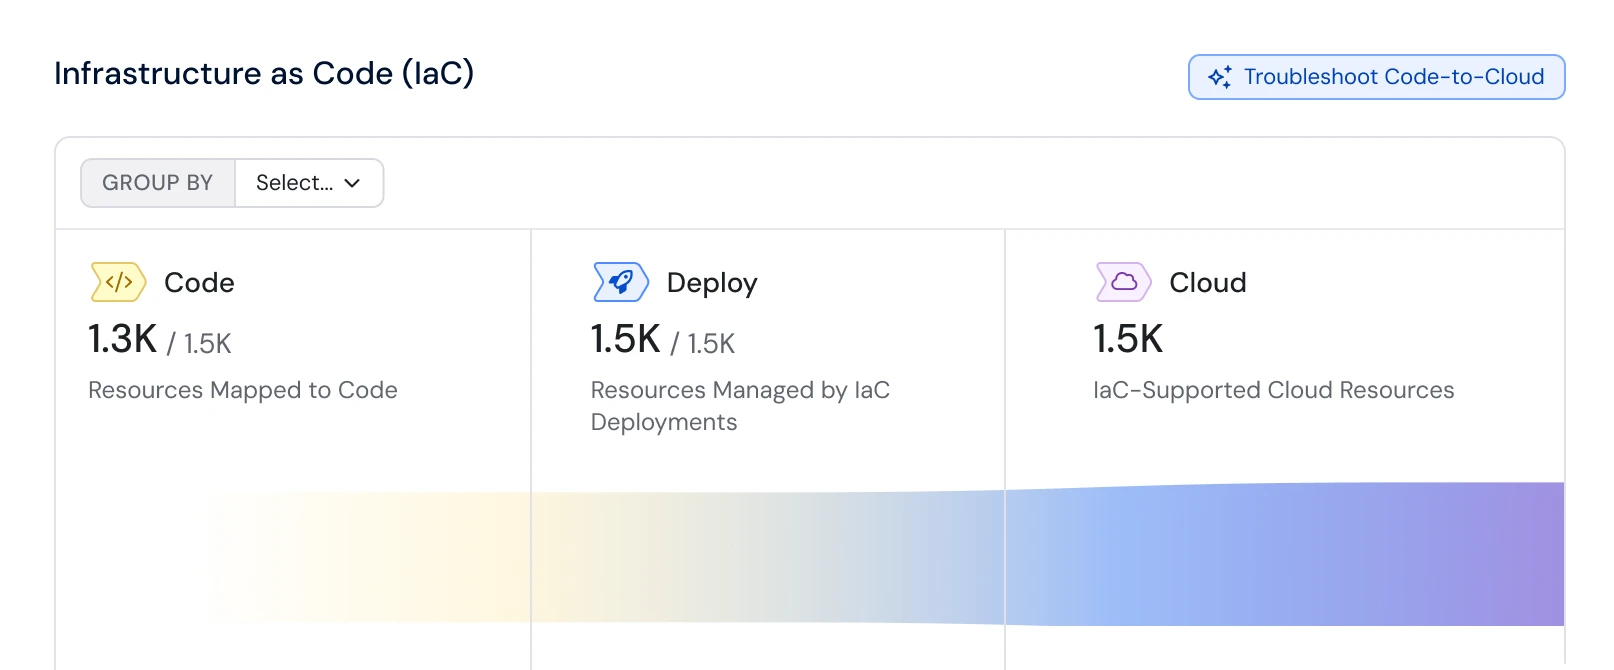
Find and fix hardcoded secrets in code, IaC templates, and container images. Prevent lateral movement and protect your cloud resources and sensitive data.
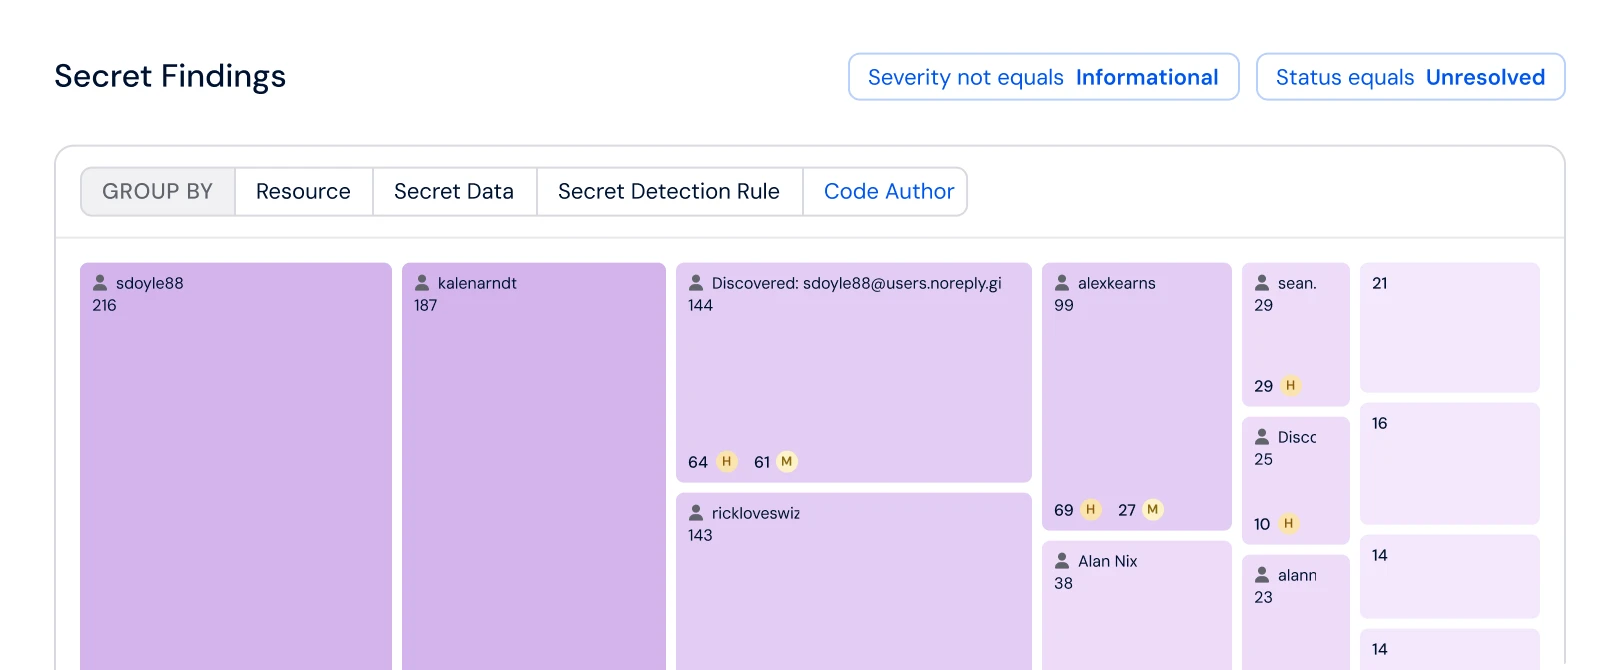
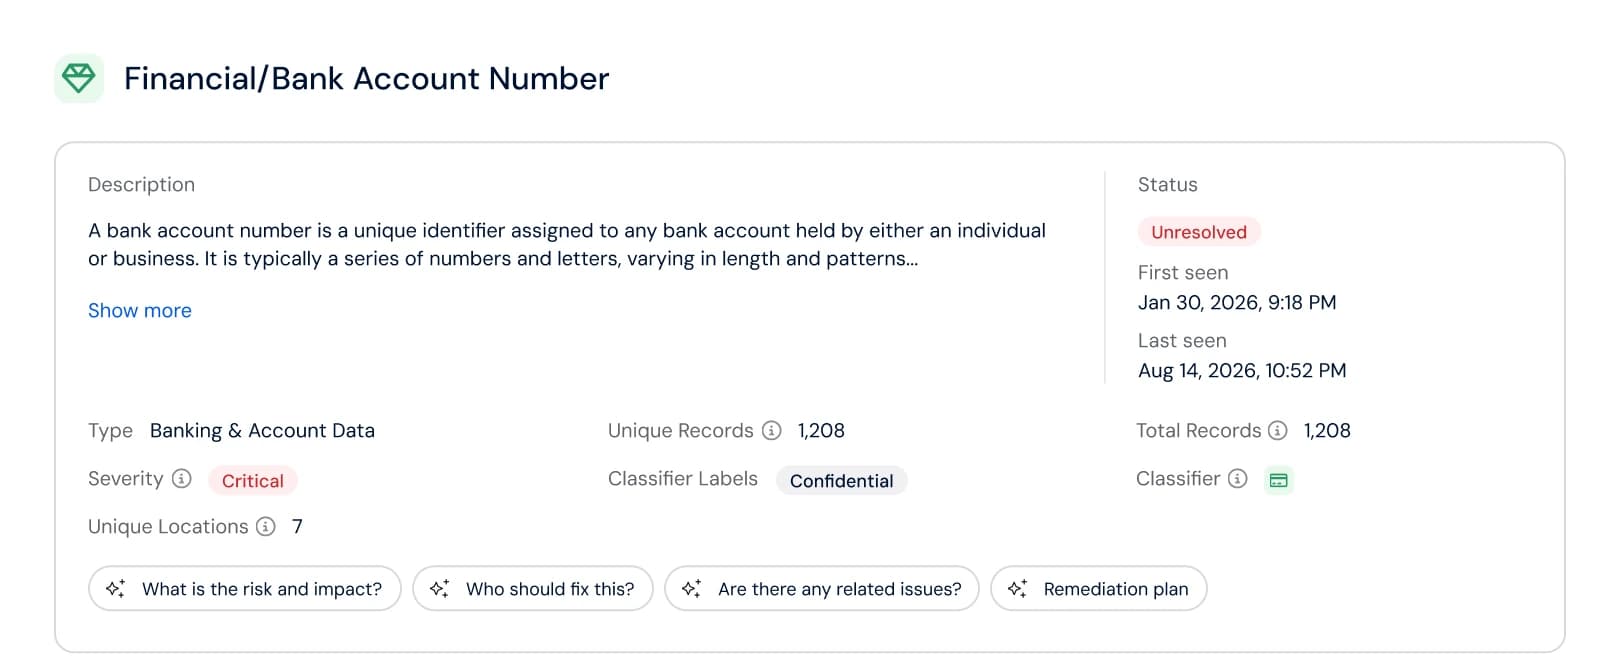
Identify and classify sensitive data like PHI and PII within your codebase. Ensure compliance and protect against accidental data exposure.
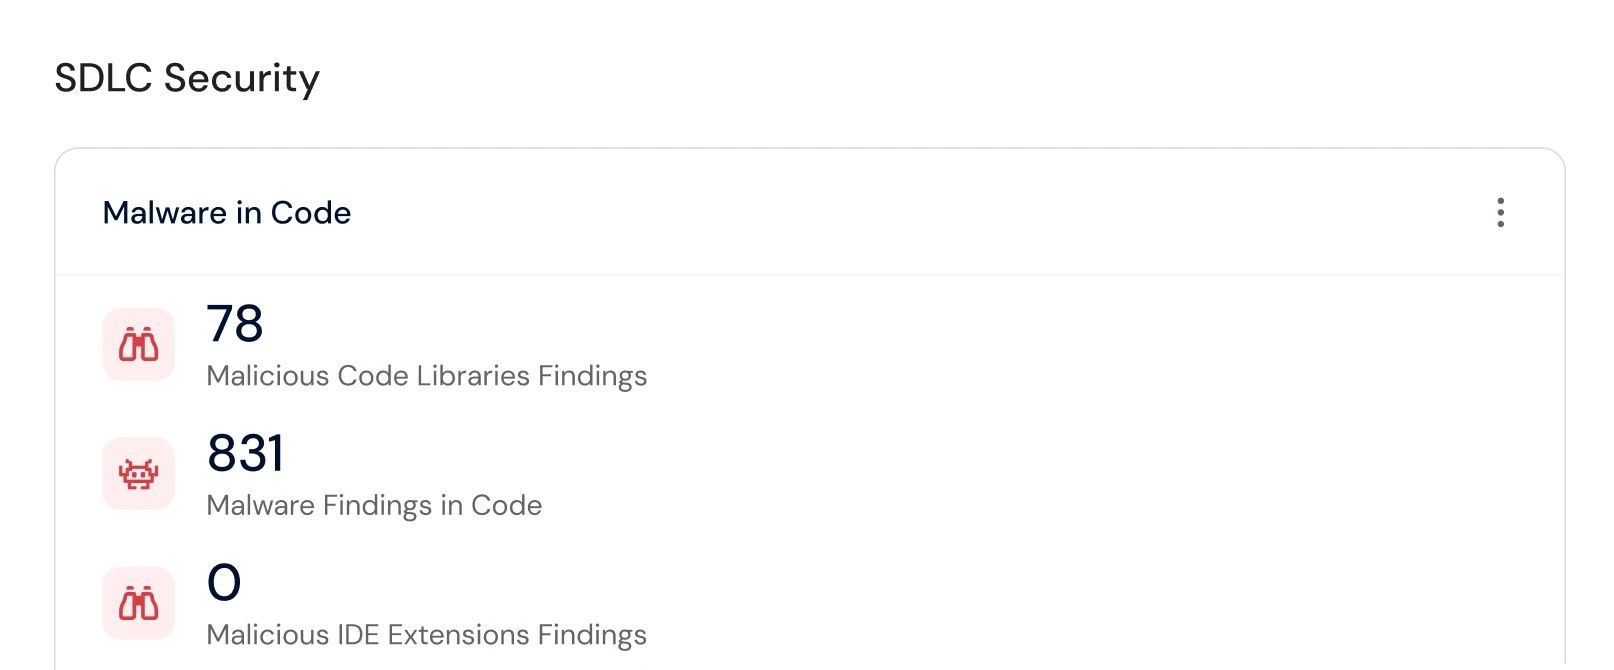
Detect and eliminate malware in your codebase before it reaches your CI runners and cloud environments.
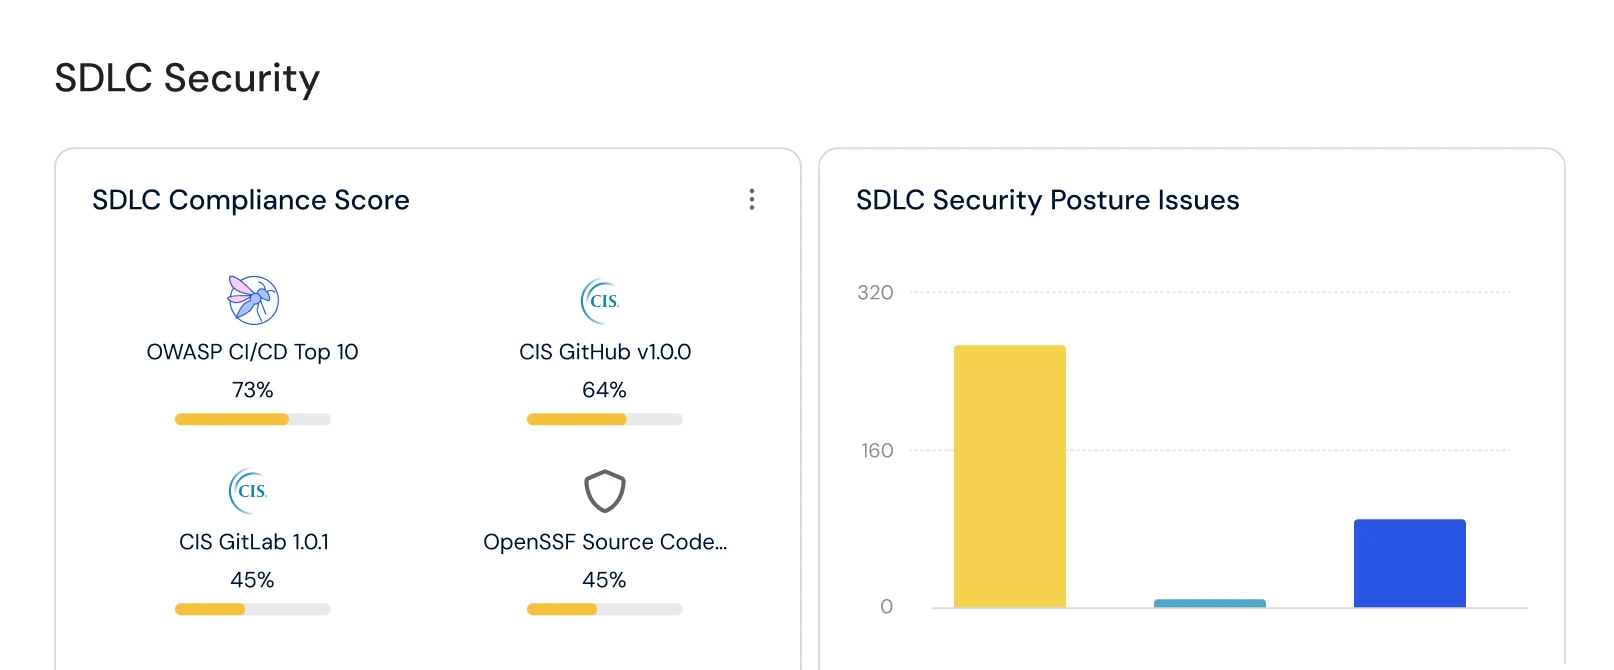
Harden VCS and CI/CD systems against misconfigurations and insecure defaults. Build trust in your software delivery pipeline and supply chain. Ensure compliance with industry standards.
Aggregate and correlate findings from built-in and third-party scanners, SAST, SCA, DAST, and more. Connect code risks to cloud impact, enforce policies across the SDLC, and drive remediation with context and ownership.
Learn more