
What are cloud security controls?
Cloud security controls are the policies, procedures, and technical safeguards that keep your cloud apps, data, and infrastructure protected, so a single misstep doesn't turn into an exposure. They span critical disciplines, including cryptographic encryption, identity governance, microsegmentation, and continuous runtime logging to preserve confidentiality, integrity, and availability.
Under the Shared Responsibility Model, your cloud service provider (CSP) guarantees the hardware, virtualization stack, and physical security of the data center. You are entirely responsible for the assets running inside that infrastructure, and PwC's 2026 Digital Trust Insights survey of 3,887 executives ranks cloud security second among budget priorities.
CNAPP Market Guide
Cloud security control coverage provides a practical lens for evaluating unified security platforms with Gartner’s CNAPP Market Guide.

Why do cloud security controls matter?
Because the cloud control plane is inherently software-defined, configuration errors or overly permissive access states can instantly expose an enterprise. In practice, much of the day-to-day risk sits on your side of the shared responsibility line, which is good news: configuration and access are things your team can see and fix.
Without robust controls, a single minor misconfiguration can scale automatically across an entire environment. Wiz's Cloud Data Security Snapshot found 72% of cloud environments have publicly exposed PaaS databases lacking sufficient access controls, the kind of minor oversight that becomes an enterprise-wide incident. Implementing structured, automated controls ensures that security parameters scale dynamically alongside your infrastructure.
Types of cloud security controls
To build an effective defense-in-depth strategy, enterprise security teams must balance four distinct categories of controls:
| Control type | What they do | Examples |
|---|---|---|
| Deterrent controls | Discourage attackers before they act | Security warning banners, compliance certifications displayed to vendors, and visible audit logging that signals monitoring is active |
| Preventive controls | Block threats from succeeding | Encryption at rest and in transit, MFA enforcement, network segmentation, and least-privilege IAM policies |
| Detective controls | Identify threats and anomalies in progress | Cloud-native SIEM, intrusion detection systems, and configuration drift monitoring |
| Corrective controls | Contain damage and restore normal operations | Automated remediation workflows, immutable backups, and incident response runbooks |
In practice, strong programs layer all four types on the same asset, so one bucket can carry encryption, access logging, and an automated fix if it goes public.
Cloud security tools that enforce each control type
Most teams enforce these controls through a handful of tool categories, each covering a different slice of the cloud. Here's how they map to the four control types:
| Tool category | What it does | Control types it supports |
|---|---|---|
| Cloud security posture management (CSPM) | Checks cloud configurations against benchmarks and flags drift, such as public buckets or open security groups | Preventive and detective |
| Cloud infrastructure entitlement management (CIEM) | Maps which users, roles, and services can reach each resource, then flags unused or excessive permissions to trim | Preventive |
| Cloud workload protection platform (CWPP) | Scans VMs, containers, and serverless functions for vulnerabilities and malware, and watches workload behavior at runtime | Preventive and detective |
| Cloud detection and response (CDR) | Monitors cloud audit logs and runtime signals for active threats, then helps contain them by revoking credentials or isolating resources | Detective and corrective |
| Data security posture management (DSPM) | Finds and classifies sensitive data across cloud data stores and shows where it is exposed or over-shared | Detective |
| Cloud access security broker (CASB) | Sits between users and SaaS apps to enforce access and data policies, and makes usage rules visible to employees | Preventive and deterrent |
The catch is that each tool keeps its own alert queue, which Ciena tackled when it consolidated 5–6 independent security tools into a single platform. One risky VM can surface as three unrelated tickets, and nobody sees that together they form an attack path. That's why a cloud-native application protection platform (CNAPP) brings these categories into one view. Instead of triaging three queues, teams see the connected risk and fix the piece that breaks the path.
Common challenges that weaken cloud security controls
The biggest challenges with cloud controls are missing inventory, unnoticed changes, and slow enforcement. When teams can't see what exists or what changed, even well-designed controls quietly drift out of place.
According to the Wiz 2026 CISO Security Budget Benchmark, tool sprawl has hit a critical breaking point: 58% of organizations now run more than 25 security tools, and nearly half of CISOs say cloud complexity and tool sprawl are holding back their security programs. Close these gaps first, and every control you add afterward produces fewer, clearer findings.
Here are the capabilities that make controls work in practice:
Centralized asset inventory: You need a reliable list of accounts, subscriptions, projects, workloads, identities, and data stores, including ephemeral resources, unified across a single control plane.
Native integration with cloud control planes: Controls should map directly to real provider enforcement points (like IAM, organizational policies, security groups, KMS, and workload configurations) rather than operating as detached, top-heavy overlays.
Automation for enforcement and rollback: If you detect a public bucket or an over-privileged role, you need a repeatable, programmatic way to fix it fast and prevent it from reappearing without waiting for human intervention.
Evidence and ownership: A control is only useful if you can instantly prove it is active, see exactly where it is failing, and route the remediation data straight to the specific engineering squad that owns the infrastructure.
If any of these are missing, you will end up with a long list of fragmented findings, severe alert fatigue, and slow remediation cycles.
The top cloud security control frameworks
Frameworks provide the organizational structure for selecting and implementing controls. Rather than treating them as compliance checklists, use them to map your control coverage across the four types discussed above and identify gaps in your security program.
MITRE ATT&CK®
MITRE ATT&CK catalogs adversary tactics and techniques based on real-world observations. For cloud environments, the Cloud Matrix documents how attackers exploit cloud-specific services across platforms (including Office Suites, Identity Providers, SaaS, and IaaS), from initial access through credential theft to data exfiltration.
Implementing defensive controls requires knowing how threat actors actually get in. According to the Wiz Cloud Threats Retrospective 2026, initial access most often came through vulnerabilities, exposed secrets, and misconfigurations, while AI expanded the attack surface.
Use ATT&CK to map your detective and preventive controls against these entry points and the techniques that follow them. If your controls don't address common cloud tactics like "Valid Accounts: Cloud Accounts" or "Account Manipulation," you have critical coverage gaps where attackers are most active.
NIST Cybersecurity Framework
The NIST Cybersecurity Framework (CSF) is a widely used guide for organizing security work, and in the cloud it gives teams a shared way to map controls. The current version, NIST CSF 2.0, organizes cybersecurity outcomes into six functions: Govern, Identify, Protect, Detect, Respond, and Recover. These functions map directly to cloud security control types: Govern sets policy and ownership, Protect covers preventive controls, Detect covers detective controls, and Respond and Recover cover corrective controls.
NIST CSF is particularly useful for organizations that need to communicate security posture to executive leadership or align with U.S. federal requirements. Regulators look for the same evidence: SEC examiners say they will review registered firms' access controls, governance, and incident response.
Cloud Security Alliance (CSA) Security, Trust, Assurance, and Risk (STAR) program
The CSA's STAR program uses the Cloud Controls Matrix (CCM), CSA's catalog of cloud-specific controls, as its baseline for assessing how well cloud services protect customer data. This framework emphasizes transparency so you can make informed decisions about cloud service providers based on their security posture.
The program includes several levels, including the following:
Level I (Self-assessment): Communicates that organizations practice foundational security, which the certificate holder proves
Level II (Third-party audit): Centers on an independent assessment that proves expertise and focuses on security protocols and advanced security
Level III (Continuous auditing): Proves the top level of assurance that verifies continuous monitoring and best security practices
ISO/IEC 27017:2015
This international standard is a code of practice for information security controls for cloud services, building on ISO/IEC 27002 and addressing both cloud providers and their customers. This ISO/IEC framework also helps you align your cloud security practices with globally recognized standards.
Used together, these frameworks show where your coverage is thin and give compliance and engineering teams a common language.
Watch 12-min demo
Cloud security controls rely on visibility across configurations, identities, and workloads, and a 12-minute recorded Wiz demo shows how connected risk context supports prioritization.

Deterrent control best practices
Deterrent controls make policy violations visible and unattractive before anyone tries them. Two practices do most of the work here.
1. Tailor and implement governance frameworks for cloud environments
Governance frameworks deter violations by making policy enforcement visible and automatic. When teams know that tagging policies, resource quotas, and configuration standards are codified and continuously enforced, they're far less likely to attempt workarounds.
You can implement governance frameworks using infrastructure-as-code tools like Terraform or AWS CloudFormation. The example below enforces a tagging policy that requires a "Project" tag before resources can be created:
resource "aws_organizations_policy" "require_project_tag" {
  name = "require-project-tag"
  type = "SERVICE_CONTROL_POLICY"

  content = jsonencode({
    Version = "2012-10-17"
    Statement = [
      {
        Sid      = "DenyEC2WithoutProjectTag"
        Effect   = "Deny"
        Action   = ["ec2:RunInstances"]
        Resource = ["arn:aws:ec2:*:*:instance/*"]
        Condition = {
          Null = { "aws:RequestTag/Project" = "true" }
        }
      }
    ]
  })
}
Your team can also create reusable modules for each NIST function, so the same policies apply in every account from day one.
2. Embed Policy-as-Code warnings and guardrails directly into CI/CD
Deterrent controls are most effective when they provide immediate, visible feedback during the development lifecycle rather than after deployment. When engineers know their pull requests are automatically evaluated against codified organizational standards, they are deterred from introducing risky configurations or attempting workarounds.
Using Policy-as-Code tools (such as Open Policy Agent, Checkov, or native CI/CD security linters), security teams can establish automated checks that flag non-compliant infrastructure as code before it merges. For instance, you can configure an automated pull request check that blocks a merge if a storage bucket is defined with public read permissions or disabled encryption.
Surfacing policy failures directly inside the developer's pull request provides clear guardrails, making non-compliance immediately visible and holding squads accountable before infrastructure is ever provisioned.
Preventive control best practices
Preventive controls stop an attack before it starts by limiting who can do what and closing known gaps. These three practices carry the most weight.
1. Enforce strict permissions
Zero trust assumes that no user, device, or network segment is inherently trustworthy. Every access request must be verified based on identity, device posture, and context before granting the minimum privileges needed.
In modern cloud ecosystems, this principle must aggressively extend to automated, non-human entities. Wiz research indicates that machine-to-machine control planes are expanding rapidly, with 57% of organizations deploying self-hosted AI agents and 80% adopting Model Context Protocol (MCP) servers. These orchestration layers handle highly sensitive data paths. McKinsey, citing SailPoint research, reports that 80% of organizations say they have encountered risky behaviors from AI agents, including access to systems without authorization. If an AI service account or autonomous agent is left over-privileged, it introduces an aggressive, automated attack path where a compromise allows lateral movement straight into corporate data stores.
In cloud environments, mitigating this requires continuous authentication, microsegmentation between workloads, and just-in-time access grants rather than standing privileges. This model significantly reduces organizations' attack surface by thoroughly vetting each access request.
For example, in AWS, IAM policies allow you to specify permissions and conditions:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AllowBucketAccessWithMFA",
      "Effect": "Allow",
      "Action": ["s3:GetObject", "s3:PutObject"],
      "Resource": "arn:aws:s3:::example-bucket/*",
      "Condition": {"Bool": {"aws:MultiFactorAuthPresent": "true"}}
    }
  ]
}
You can implement a zero-trust architecture with these key strategies:
Set up guardrails to enforce least-privilege access, which minimizes the blast radius of potential breaches.
Use AWS CloudTrail for continuous auditing. It provides a detailed record of all actions users have taken within your AWS environment.
Review unused roles and access keys every quarter and remove anything that hasn't been used, so standing access keeps shrinking.
2. Enforce immutable infrastructure over in-place patching
Traditional in-place patching does not scale in dynamic cloud environments. Modern preventive controls replace manual updates with immutable infrastructure: rebuilding and redeploying fresh, pre-patched golden images and hardened container templates through automated CI/CD pipelines. When critical vulnerabilities emerge, teams do not patch live production instances—they update the upstream base image and trigger an automated rolling redeployment, eliminating configuration drift and ensuring all running workloads remain secure by default.
3. Prioritize risk management
To automate this, you can correlate vulnerability scanner findings with network exposure and identity permissions using the AWS SDK to isolate genuine attack paths:
import boto3

ec2 = boto3.client("ec2")
inspector = boto3.client("inspector2")

def find_prioritized_attack_paths():
    """
    Prioritize risk by toxic combination:
    Critical CVE + Public Internet Exposure + Attached IAM Role.
    """
    # 1. Fetch active critical findings
    findings = inspector.list_findings(
        filterCriteria={
            "severity": [{"comparison": "EQUALS", "value": "CRITICAL"}],
            "findingStatus": [{"comparison": "EQUALS", "value": "ACTIVE"}]
        }
    ).get("findings", [])

    for finding in findings:
        resource = finding.get("resources", [{}])[0]
        if resource.get("type") != "AWS_EC2_INSTANCE":
            continue

        instance_id = resource.get("id")

        # 2. Check for exposure (Public IP) and blast radius (IAM Role)
        instances = ec2.describe_instances(InstanceIds=[instance_id])["Reservations"]
        for res in instances:
            for inst in res["Instances"]:
                public_ip = inst.get("PublicIpAddress")
                iam_profile = inst.get("IamInstanceProfile")

                # 3. Escalate only if the vulnerability forms a viable attack path
                if public_ip and iam_profile:
                    print(f"[CRITICAL ATTACK PATH DETECTED] Instance: {instance_id}")
                    print(f"  CVE Title   : {finding['title']}")
                    print(f"  Public IP   : {public_ip}")
                    print(f"  IAM Profile : {iam_profile['Arn']}\n")
Ranking risks this way puts your effort on the most critical vulnerabilities first. Wiz's State of Cloud Risk 2026 places the vast majority of high- and critical-severity exploitable issues in information disclosure, credentials and secrets, and unauthorized access.
Detective control best practices
Below are two best practices you can implement today:
1. Implement event-driven anomaly detection and automated response
Modern cloud detection relies on event-driven telemetry to catch behavioral anomalies in real time and trigger immediate containment, as demonstrated in this Lambda handler reacting to credential exfiltration:
import json
import boto3

iam = boto3.client("iam")

def lambda_handler(event, context):
    """
    Event-driven detection & response: React to behavioral control plane anomalies
    such as compromised IAM credentials or instance metadata exfiltration.
    """
    detail = event.get("detail", {})
    finding_type = detail.get("type", "")

    # Detect high-fidelity runtime behavioral anomaly
    if "UnauthorizedAccess:IAMUser/InstanceCredentialExfiltration" in finding_type:
        user_name = detail.get("resource", {}).get("accessKeyDetails", {}).get("userName")
        access_key_id = detail.get("resource", {}).get("accessKeyDetails", {}).get("accessKeyId")

        print(f"[ALERT] Credential exfiltration detected for entity: {user_name}")

        # Automated containment: revoke compromised credentials via the control plane
        if access_key_id:
            iam.update_access_key(
                UserName=user_name,
                AccessKeyId=access_key_id,
                Status="Inactive"
            )
            print(f"[CONTAINED] Revoked access key {access_key_id}")

    return {"statusCode": 200, "body": json.dumps("Anomaly processed")}
2. Conduct consistent configuration audits
Practicing audits consistently for your cloud configuration settings will help you identify misconfigurations or unauthorized changes and verify that your security posture meets standards. One way to conduct regular audits and vulnerability scanning is to use automated tools that detect inconsistencies and errors, such as AWS Audit Manager or Azure Security Center.
Corrective control best practices
Corrective controls limit damage and get you back to a known-good state once something slips through. In the cloud, most of that work happens through APIs.
Build a cloud incident response plan
Cloud incident response differs fundamentally from traditional IR because containment happens through APIs, not network cables. When a workload is compromised, you don't physically isolate a machine. Instead, you modify security groups, revoke IAM credentials, or snapshot the instance for forensics, all through the control plane.
Your incident response plan should include cloud-specific playbooks for common scenarios:
Data exfiltration: Automatically isolate affected resources, revoke credentials, and trigger forensic analysis.
Privilege escalation: Disable compromised accounts, alert security teams, and audit recent permission changes.
Misconfigurations: Revert unauthorized changes using IaC state files and prevent recurrence through policy enforcement.
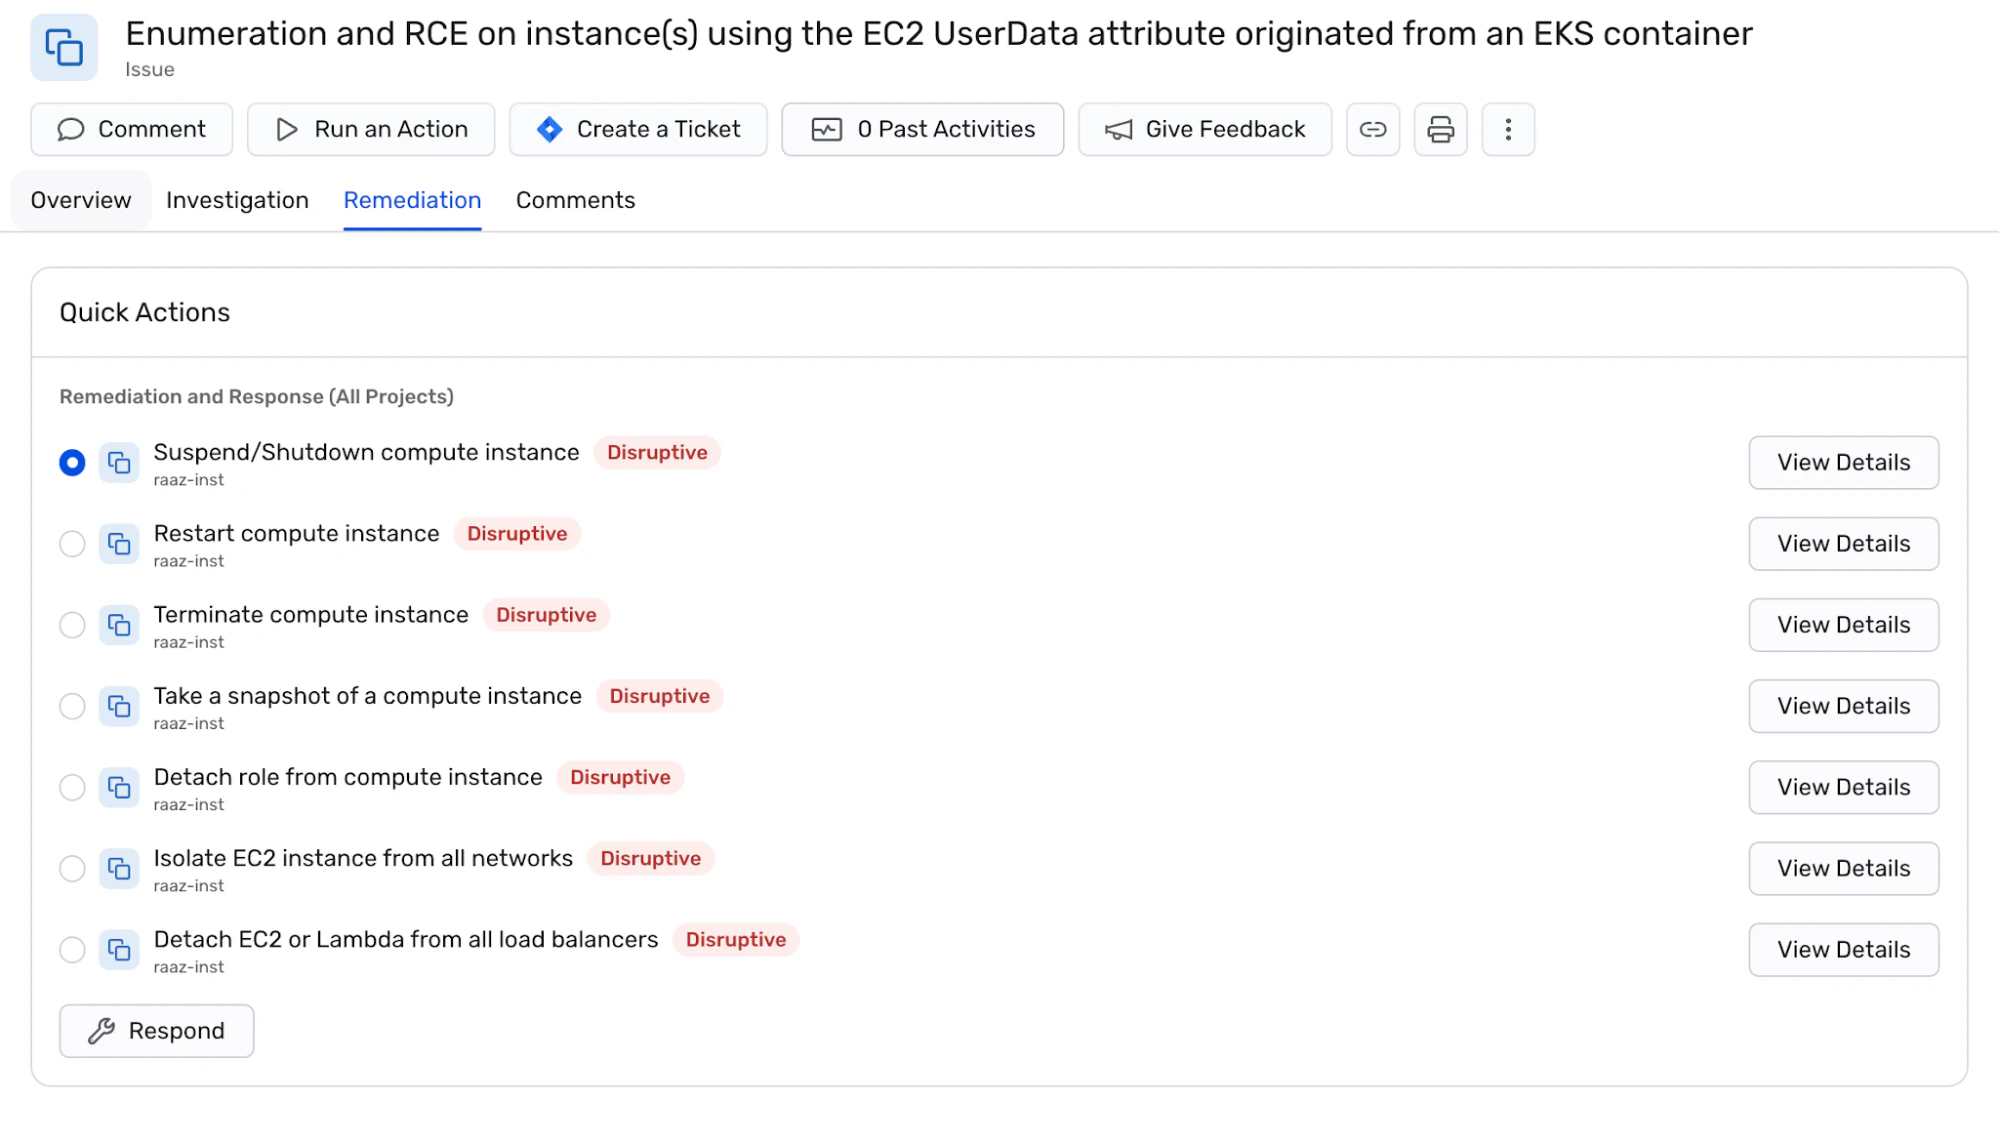
Automated workflows in a unified platform like Wiz help you contain and resolve these threats faster across complex cloud infrastructure.
How Wiz strengthens cloud security controls
Most control tools operate in silos: a CSPM flags an open security group, a vulnerability scanner flags a CVE on a VM, and an IAM analyzer flags an over-privileged role. None of them knows whether another control already mitigates the risk, leaving security teams drowning in disconnected alerts.
The Wiz Security Graph contextualizes control failures across network exposure, vulnerabilities, identities, secrets, and sensitive data, surfacing the toxic combinations that create viable attack paths. Wiz builds this picture agentlessly through cloud provider APIs, extending unified visibility across multi-cloud, container, SaaS, and hybrid environments.
Deterrent: Continuous compliance monitoring and automated governance frameworks give teams visibility into which policies are active, audited, and enforced across every account.
Preventive: IaC scanning blocks misconfigurations in the CI/CD pipeline before deployment, while agentless CSPM, CIEM, and DSPM continuously enforce least privilege, correct storage exposures, and protect AI models and training data in live environments.
Detective: Wiz Defend provides Cloud Detection & Response (CDR), correlating runtime telemetry and cloud audit logs with the Security Graph’s real-time inventory to catch active attacks—including shadow AI usage—while filtering out false alarms.
Corrective: When control failures occur, contextual findings and clear remediation guidance are automatically routed to the owning engineering squad, and Wiz validates that the exposure has been eliminated.
Cloud security controls require context to turn hundreds of flat findings into clear operational priorities. Request a demo to see how the Wiz Security Graph maps attack paths and accelerates remediation.
Cloud security controls with Wiz
Cloud security control gaps become easier to prioritize when risks are connected, and a Wiz demo shows how the platform maps attack paths and guides remediation.
