

Modern vulnerability management is harder than ever. Cloud environments change by the minute, multi-cloud estates continue to grow, and teams deploying code every day can't rely on weekly scans to understand their attack surface.
The challenge goes beyond finding vulnerabilities. Teams need the context to know which ones actually matter.
What is vulnerability management?
Vulnerability management is the continuous process of finding, prioritizing, and fixing security weaknesses before attackers can exploit them. It spans source code, build pipelines, cloud infrastructure, workloads, applications, endpoints, and your external attack surface. A vulnerability is any flaw an attacker can exploit to gain unauthorized access or cause damage, distinct from a threat (the actor) or a risk (the likelihood and impact of exploitation).
The practice has become harder, not easier. Cloud resources are ephemeral, multi-cloud sprawl is the norm, and teams that deploy daily cannot rely on weekly scans. In that environment, the problem is rarely finding vulnerabilities. It’s having enough context to know which ones actually matter. A critical common vulnerabilities and exposures (CVE) entry on an isolated dev box is very different from a medium-severity issue on an internet-facing service with access to sensitive data. Modern programs evaluate risk based on who can reach the asset, what permissions exist, whether active exploits are circulating, and where sensitive data lives.
Why vulnerability management matters
The window between disclosure and exploitation is collapsing. Attackers once needed weeks to reverse engineer a patch and weaponize it. Today, AI is compressing that timeline to hours. Claude Mythos, Anthropic's frontier model, has demonstrated the ability to discover and exploit previously unknown vulnerabilities far faster than traditional manual research. Access is currently limited to approved researchers, but our researchers estimate that similar capabilities will reach openly available models within 12 to 18 months.
This shrinking response window is why vulnerability management has shifted from a periodic IT task to a continuous security discipline. When that happens, patch windows measured in weeks become a liability.
The data already reflects this pressure. According to the Wiz 2026 Cloud Threats Retrospective, 80% of documented cloud intrusions in 2025 began with vulnerabilities, exposed secrets, or misconfigurations, and 40% involved the exploitation of weaponized vulnerabilities. When the React2Shell vulnerability (CVE-2025-55182) dropped, over 60 distinct campaigns exploited it within a single week.
The financial stakes are equally clear. IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at $4.44 million, driven largely by regulatory penalties and slow detection.
AWS Vulnerability Management Best Practices Cheat Sheet
Secure your AWS environment with this definitive guide to cloud defense. From agentless visibility to automated patching, get the essential blueprint for hardening your workloads and neutralizing risks before they scale.

Consequences of weak vulnerability management
Weak vulnerability management creates three compounding problems.
The first is cost: data breaches that start with an unpatched flaw or exposed asset carry the multimillion-dollar averages above, plus downstream expenses like incident response, legal fees, and customer churn.
The second is compliance exposure. Frameworks such as PCI DSS, HIPAA, and ISO 27001 mandate documented remediation timelines, and failed audits bring penalties and lost contracts.
The third is operational disruption. Without an up-to-date inventory of security weaknesses, teams burn critical hours during incidents just figuring out what is exposed, and unplanned emergency patching pulls engineers off roadmap work. Each gap widens the others. An expanding attack surface slows response. Slow response gives cyberattackers more opportunity to exploit weaknesses, and every incident drains the resources needed to fix root causes.
The benefits of strong vulnerability management
A mature vulnerability management program delivers measurable advantages across security and operations:
Stronger security posture: Continuously identifying and remediating security weaknesses reduces your attack surface before attackers can exploit it, improving your overall security posture.
Improved compliance: Consistent remediation, evidence trails, and documented workflows help teams meet requirements under frameworks such as PCI DSS, ISO 27001, and internal SLAs.
Faster operations: Integrating vulnerability management into DevOps workflows reduces manual effort, accelerates remediation, and helps security teams work without slowing development.
Clearer visibility: Continuous discovery and contextual prioritization give teams a single, real-time view of vulnerabilities, misconfigurations, and other risks across every environment.
Shared ownership: Developers, platform engineers, and security teams get the context they need to understand ownership, prioritize work, and remediate the risks that matter most.
Vulnerability management vs. vulnerability assessment
The two terms are related, but they are not interchangeable.
A vulnerability assessment is a point-in-time activity: a scan or review that identifies potential weaknesses. It is a snapshot, similar in spirit to periodic penetration testing.
Vulnerability management is the ongoing, code-to-cloud process that wraps around those snapshots. It includes continuous discovery, contextual prioritization, remediation, validation, and reporting to reduce exploitable risk over time.
The vulnerability management process in 5 steps
Practitioners often refer to the vulnerability management lifecycle as the organizing framework behind a mature program. It is a continuous process rather than a one-time project, with each stage feeding into the next as your environment changes.
The five steps below break that lifecycle into the operational activities teams perform every day.
Discover — Build a complete inventory across code, cloud, and your external attack surface.
Prioritize — Rank findings by real-world exploitability and business impact.
Remediate — Fix the highest-risk issues first.
Validate — Confirm fixes removed the risk and remain effective.
Report — Measure progress and guide continuous improvement.
1. Discover
Discovery builds a living inventory that spans code repositories and pipelines, cloud accounts, and the internet-facing edge: VMs, containers, serverless functions, ephemeral resources, identities, data stores, and external assets like domains and exposed services. Continuous scanning combines scheduled scans, real-time inventory updates, and event-triggered checks, while agentless collection inspects workloads without installing software on hosts. Outside-in attack surface management complements this view by uncovering unmanaged assets, dangling DNS, and shadow subdomains that internal vulnerability scanners miss. The result is a single, always-current graph of what you own, how it connects, and where attackers could begin.
2. Prioritize
The Common Vulnerability Scoring System (CVSS) gives every finding a standardized severity baseline, but it cannot tell you whether the vulnerability is actively being exploited or whether the affected asset holds business-critical data. A high CVSS score on an isolated sandbox can represent far less real risk than a medium score on an internet-facing database. Risk-based vulnerability management (RBVM) fills that gap by combining CVSS with threat intelligence such as EPSS scores and CISA KEV entries, asset criticality, and attack path analysis across network exposure, identity permissions, and data sensitivity. Risk-based prioritization produces a remediation queue ranked by actual risk, so teams fix the small set of findings on a viable path to critical assets instead of chasing every critical-severity CVE.
3. Remediate
Remediation closes the exploitable paths that discovery and prioritization surfaced. Attack path analysis shapes the queue: a medium-severity flaw on a reachable path to sensitive data may warrant an immediate fix, while a critical CVE on an isolated host can wait. Actions vary by finding, from patching software and decommissioning dormant assets to right-sizing entitlements and making targeted configuration changes. Integrating fixes into existing workflows keeps teams fast. Pull-request fixes and automated ticket routing let developers remediate issues without leaving the tools they already use.
4. Validate
Validation proves that risk was actually removed and stays removed. In practice, that means confirming the vulnerability is no longer exploitable, the exposure that made it risky is gone, the fix introduced no regressions, and the remediation remains effective as the environment changes. Validation also produces the evidence trail auditors require: scan results, ticket closures, and re-test reports that satisfy remediation requirements under frameworks like PCI DSS and ISO 27001. Continuous re-scans and drift detection ensure closed issues stay closed.
5. Report
Reporting turns work into outcomes. Reporting should include scheduled, role-based reports for executives, platform owners, and auditors, alongside on-demand dashboards for daily operations. Focus on trends that prove risk is dropping: exploitable-risk reduction, mean time to remediate (MTTR), recurrence rate, and SLA adherence. Use those insights to recalibrate priorities and set goals for the next cycle, so the program gets measurably safer over time.
Watch 12-min demo
Learn about the full power of the Wiz cloud security platform. Built to protect your cloud environment from code to runtime.

AI and vulnerability management
AI is transforming vulnerability management in two ways: it expands the attack surface while helping security teams identify and remediate risk more effectively.
For many organizations, AI is no longer just another application. It's another environment that needs to be continuously discovered, assessed, and protected.
On the risk side, AI workloads are now core infrastructure. Wiz’s 2026 State of AI in the Cloud Report found that at least 81% of cloud environments use managed AI services, and Model Context Protocol (MCP) servers appear in at least 80% of environments, placing new services, identities, and data paths closer to sensitive resources. These workloads rely on open-source models, third-party APIs, and dynamically generated code, creating new attack vectors that traditional vulnerability scanners struggle to understand in context.
On the opportunity side, AI can correlate vast amounts of security telemetry, linking findings to identity paths, data sensitivity, and runtime behavior to surface what is actually exploitable. This is where Wiz's AI agents become practical. The Red Agent validates whether a finding is realistically exploitable, while the Green Agent generates root-cause analysis and merge-ready code fixes, helping teams move from prioritization to remediation much faster.
How to implement an effective vulnerability management program
An effective vulnerability management program depends on consistent processes, clear ownership, and continuous improvement. These six practices provide the foundation.
Prioritize coverage first. Start with a comprehensive inventory of devices, applications, endpoints, and cloud resources, including shadow IT. An up-to-date baseline ensures you assess every component and provides the context needed for accurate risk-based prioritization.
Shift risk ownership left. Embed security from development through deployment by integrating checks into CI/CD pipelines. Developers who catch flaws as they write code prevent issues from ever reaching production.
Build a dedicated vulnerability management team. Assign clear ownership across security operations, compliance, and DevOps. Defined ownership for scanning, risk assessment, and remediation keeps the program accountable.
Align with risk. Develop a risk-based framework that weighs business impact, exploitability, and data sensitivity. This keeps your team focused on the issues that threaten essential functions first.
Automate and integrate for scale. Choose vulnerability management tools that scan across cloud, on-prem, and hybrid environments and offer contextual prioritization. Automating patching and compensating controls reduces manual effort, minimizes human error, and accelerates remediation.
Track what matters. Monitor continuously and measure outcomes such as time to triage, time to patch, and the percentage of exploitable critical risk resolved in production. Refine your processes as new attack vectors and compliance requirements emerge.
Vulnerability management in the cloud era

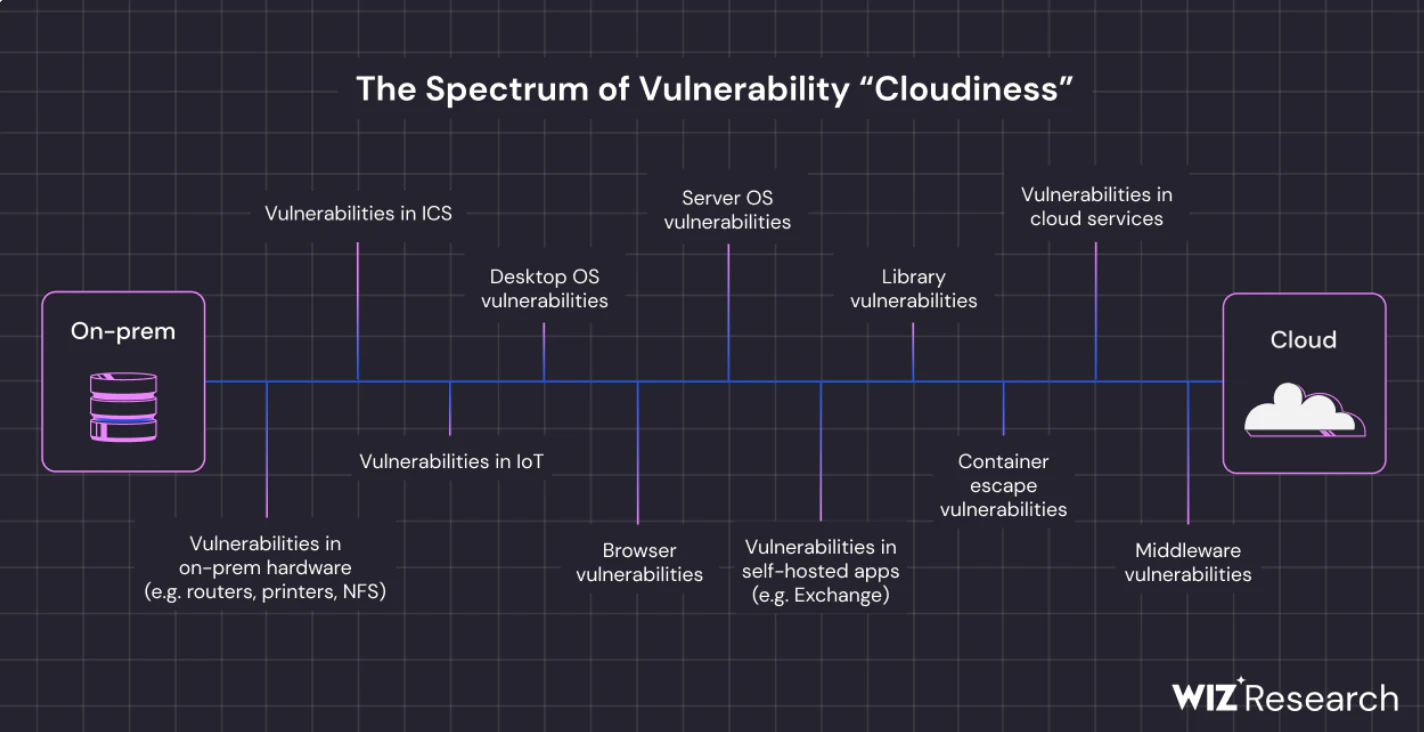
Traditional vulnerability management tools were built for static, on-premises systems with predictable inventories and monthly patch cycles. Cloud environments break every one of those assumptions. Resources spin up and disappear before a weekly scan finishes, workloads sprawl across multiple providers with different native tooling, and engineering teams deploy dozens of times a day. A scanner that reports against last week's environment describes infrastructure that no longer exists.
The tooling landscape compounds the problem. Most organizations run separate scanners for cloud configuration, containers, code, and the network edge, each producing its own findings in its own console with its own severity logic. Teams often end up triaging the same CVE across multiple tools, while true exposure hides in the gaps between them.
Unified Vulnerability Management (UVM) is the modern response. UVM consolidates every signal from code to runtime into one context-rich view of risk, deduplicating findings across scanners and enriching each one with the cloud, identity, and data context needed for accurate prioritization. Paired with a cloud native application protection platform (CNAPP) and a broader exposure management practice, UVM gives security teams a single, prioritized view of what is genuinely exploitable right now, not what happened to exist during the last scan window.
How Wiz approaches vulnerability management
Wiz delivers Unified Vulnerability Management through four connected capabilities.
Wiz UVM centralizes and deduplicates findings from cloud, on-prem, and application environments, enriching each with Security Graph context.
Wiz XM extends that visibility across the exposure management lifecycle, with the Exposure Management Dashboard serving as the command centre.
Wiz ASM discovers and validates your external attack surface, surfacing internet-facing risks internal scanners miss.
Wiz Code catches application security issues before they reach production, filtering false positives and helping developers remediate problems earlier in the software lifecycle.
Wiz UVM helps us pivot away from focusing on isolated infrastructure vulnerabilities to holistic risk-based contextual findings in a centralized place
Not sure where your biggest vulnerability gaps are? Wiz's cloud security assessment evaluates your posture across nine security domains, including vulnerability management, and shows you where to focus first. Start your free assessment.
Uncover Vulnerabilities Across Your Cloud
Stop chasing alerts—Wiz maps your entire cloud to find and prioritize real risks immediately.
